
 Do Son
Chatbots are classified into different categories, ranging from menu-based to AI chatbots. Read here to learn the most secure chatbot options
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

CVE-2024-4434 (CVSS score of 9.8), is an unauthenticated time-based SQL Injection through the ‘term_id’ parameter.

The reliability of public cloud services, Google Cloud accidentally deleted the entire online account of UniSuper

The vulnerabilities, tracked as CVE-2024-28075 and CVE-2024-23473, were discovered by ZDI vulnerability researcher Piotr Bazydło

Tycoon 2FA operates by using an adversary-in-the-middle (AitM) approach. Its primary function is to harvest session cookies

The flaw, tracked as CVE-2024-27793, was discovered by Willy R. Vasquez, a security researcher at The University of Texas at Austin.

A high-severity security vulnerability (CVE-2024-32655) has been discovered in Npgsql, a widely used open-source data provider

Technical details have emerged about a significant security vulnerability, CVE-2024-21115, which has been discovered in Oracle VM VirtualBox
The flaw, designated CVE-2024-4671, is a "use after free" bug located within the browser's "Visuals" component.

Recent discoveries have exposed CVE-2024-34350 & CVE-2024-34351 which could compromise user data and server operations

CVE-2024-4701 (CVSS 9.9) has been discovered in Genie, Netflix's popular open-source job orchestration engine for big data processing

CVE-2024-3806 (CVSS 9.8): An unauthenticated LFI vulnerability within the porto_ajax_posts function of the Porto theme

TRU have uncovered a disturbing trend in FIN7 attacks demonstrating the notorious cybercrime group's evolving tactics for infiltrating systems

CVE-2024-32980 (CVSS 9.1) has the potential to allow network sandbox escapes in specifically configured Spin applications.
The Qt Group has released a security advisory and accompanying patch in response to a vulnerability (CVE-2024-33861)

eSentire's Threat Response Unit (TRU) has detailed a sophisticated intrusion campaign by the SocGholish cyber threat group
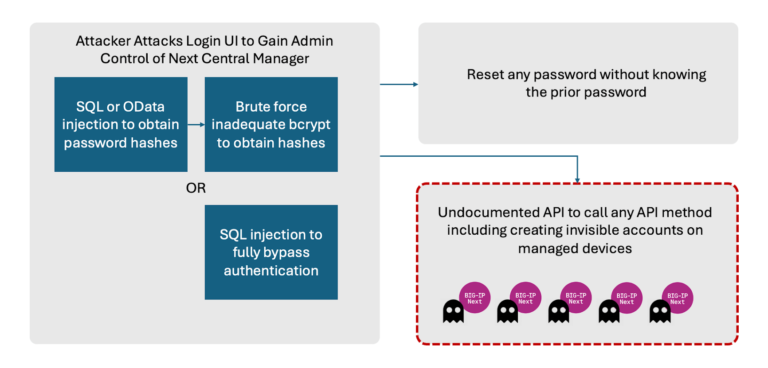
A recent investigation by Eclypsium, a prominent supply chain security firm, has unveiled a series of critical...

These flaws could potentially allow arbitrary code execution (CVE-2024-24787) and cause infinite loops (CVE-2024-24788) in DNS operations

Researchers have exposed a dangerous set of vulnerabilities within CyberPower's PowerPanel Business Software

AsyncRAT, which stands for Asynchronous Remote Access Trojan, is a sophisticated malware variant meticulously engineered

CVE-2024-34346 (CVSS 8.5) presents a significant risk as it allows for permission escalation through the mishandling of privileged files

Trend Micro has released a security update for its Maximum Security software suite, addressing a privilege escalation flaw (CVE-2024-32849)