
 Do Son
The campaign, dubbed UNK_SweetSpecter, utilizes a Remote Access Trojan (RAT) known as SugarGh0st to infiltrate systems and exfiltrate sensitive data
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

A critical SQL injection vulnerability (CVE-2024-32888) has been discovered in the Amazon JDBC Driver for Redshift
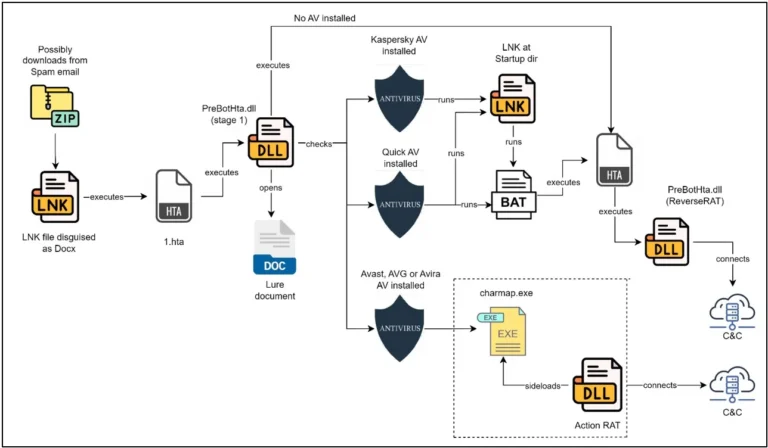
Upon further investigation, CRIL uncovered the use of malicious LNK files in the SideCopy malware campaign. These files, once executed

The PrestaShop project has recently issued a security advisory revealing two significant vulnerabilities (CVE-2024-34716 & CVE-2024-34717)

The campaign exploits GitHub, a legitimate platform for software development, to distribute various malware families

The campaign's success lies in its ability to bypass MFA, a security measure designed to protect accounts from unauthorized access

Two of the vulnerabilities, CVE-2014-100005 and CVE-2021-40655, affect specific models of D-Link routers (DIR-600 and DIR-605)

CVE-2024-22039, CVE-2024-22040, and CVE-2024-22041, reside within the network communication stack of the affected systems

CVE-2024-4984 could allow malicious actors to inject harmful scripts into websites, potentially compromising visitor data, redirecting traffic

Git project addressed a series of critical security flaws that could expose users to remote code execution (CVE-2024-32002, CVE-2024-32004)

One of the most prevalent scams involves the Instagram influencer program, designed to connect content creators with brand partnerships

A critical vulnerability (CVE-2024-34070) has been discovered in Froxlor, a popular open-source web hosting control panel

The Russia-linked Advanced Persistent Threat groups continues to evolve, posing a significant threat to Operational Technology globally

Forcepoint's X-Labs research team has uncovered a sophisticated and stealthy phishing campaign orchestrated by the notorious Darkgate malware

A widespread malvertising campaign is actively targeting individuals searching for popular utilities like WinSCP and PuTTY
CVE-2024-4947 allow attackers to execute harmful code on users' systems, compromising sensitive data and taking control of their devices

Microsoft Threat Intelligence has uncovered a sophisticated ransomware campaign orchestrated by the cybercriminal group Storm-1811

A new report reveals four critical vulnerabilities in ThroughTek's Kalay platform, a cornerstone of the IoT ecosystem

CVE-2024-32741 (CVSS 10): Hardcoded Root Password: The presence of a hardcoded password for the root user and boot loader

HPE Aruba Networking has issued an urgent security advisory, urging customers to patch their Aruba Access Points running InstantOS and ArubaOS 10

This vulnerability, identified as CVE-2023-52424 and dubbed the SSID Confusion Attack, was uncovered by security researcher Mathy Vanhoef

Microsoft swiftly assigned the CVE-2024-30051 identifier to the vulnerability and released a patch during this month's Patch Tuesday