
 Do Son
A vulnerability in Microsoft Access that allows cybercriminals to exploit the "linking to remote SQL Server tables" feature
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Imperial Kitten uses Microsoft Excel documents with embedded macros to activate the infection and install a Python shell

ESET has discovered a new type of mobile spyware called Kamran, targeting Urdu-speaking residents of the Gilgit-Baltistan region

Shortly thereafter, Trend Micro researchers observed Cerber ransomware exploiting the vulnerability to deploy its payload.

Ducktail is a malware family that has been active since the second half of 2021 and aims to steal Facebook business accounts

the American branch of the Industrial and Commercial Bank of China has suffered a cyber attack, resulting in the bank's inability to settle

Anonymous Sudan intends to continue its offensive against OpenAI, which could affect the steadiness of both the OpenAI API and ChatGPT services

Team Huntress has been able to create an exploit that chains the CVE-2023-47246 flaw to execute code remotely

The vulnerability, which has been assigned the CVE identifier CVE-2023-43791 and a CVSS score of 9.8, is a hardcoded Django secret key

Kaspersky Lab has unveiled a comprehensive analysis of the operations of Asian cyber espionage groups conducting espionage activities globally

CVE-2023-47248 in PyArrow, the Python bindings for Apache Arrow, could allow attackers to execute arbitrary code on vulnerable systems

It identified the phishing email's journey to the Outlook inbox, the victim's interaction with the Dracoon-hosted PDF

SafeBreach has engineered the first entirely undetectable cloud-based cryptocurrency miner, exploiting Microsoft Azure's automation service

Russia-affiliated group Sandworm has emerged as a formidable force, orchestrating an intricate cyber-physical attack on Ukrainian infrastructure
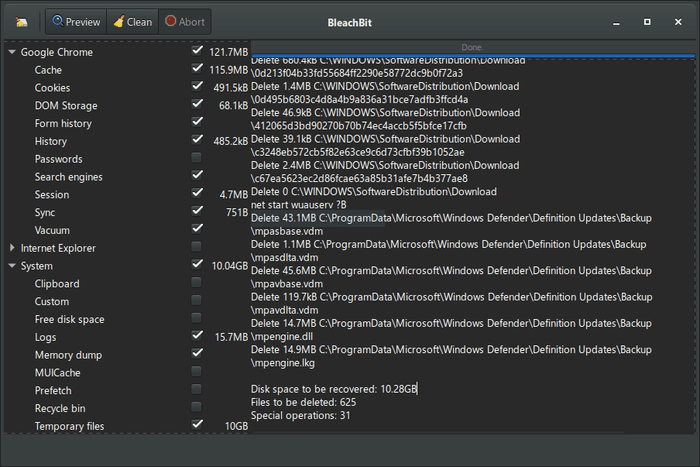
This vulnerability, known as CVE-2023-47113, exposes users to the risk of DLL Search Order Hijacking attacks.

The ad, designed to attract Windows aficionados seeking the CPU-Z tool, is a trapdoor to malware.

In the wake of these findings, Deep Instinct has unearthed additional suspected MuddyC2Go servers at Stark Industries

The zero-day flaw, CVE-2023-47246, resides in SysAid on-premises software, allowing hackers to execute arbitrary code on vulnerable systems

CVE-2023-29552 has already been added to the KEV catalog by CISA highlighting the active exploitation of this vulnerability by threat actors.

You take precautions when you do your banking at the ATM. You make sure to hide your...

Kaspersky Lab has illuminated the cyber threats lurking in the shadows, preying upon the enthusiasts of computer gaming

CVE-2023-39913 arises from the deserialization of untrusted data, specifically Java-serialized CAS objects, without proper input validation