 Do Son
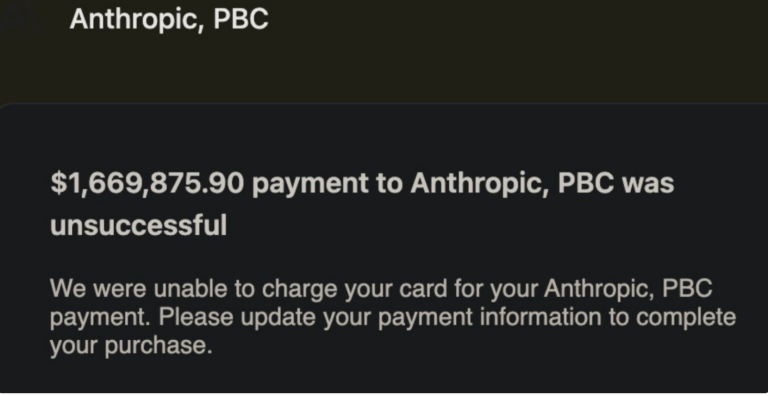
A Shocking Initial Invoice Last week, a Korean developer named REMY reported a bizarre incident online. He...
Do Son
Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
VMware Avi Load Balancer Authentication Bypass (CVE-2026-47865, CVSS 9.8) Headlines Seven-Flaw Patch
VMware Avi Load Balancer Authentication Bypass (CVE-2026-47865, CVSS 9.8) Headlines Seven-Flaw Patch
TL;DR Broadcom has patched seven vulnerabilities in VMware Avi Load Balancer under advisory VMSA-2026-0005. The most serious,...
In the generative AI computing arms race, Meta shatters the investment ceiling for AI infrastructure. Meta recently...
Last week, security researcher @Cereblab exposed a troubling behavior in Grok Build. The tool silently transmitted developers’...
TL;DR SAP Security Patch Day July 2026 shipped 16 new security notes and one GitHub advisory. The...
TL;DR CrowdStrike added 18 new methods to its AI security taxonomy. These new prompt injection attacks target...
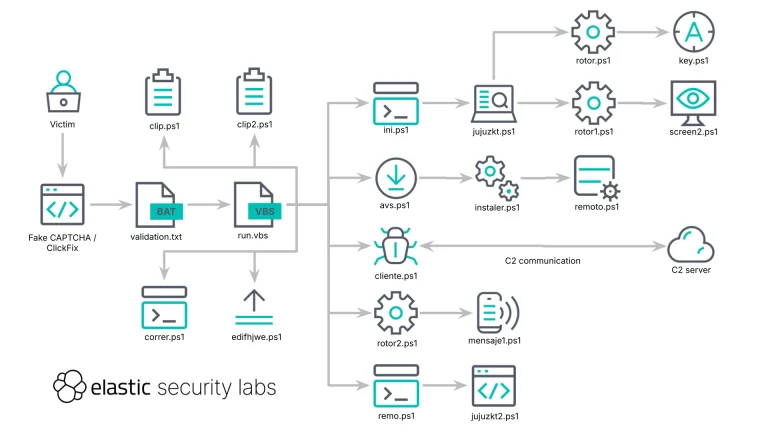
On June 18, 2026, security analysts detected a host downloading suspicious PowerShell scripts from an open directory....
TL;DR The WinFsp project has fixed two WinFsp vulnerabilities, CVE-2026-3006 (CVSS 7.0) and CVE-2026-7162 (CVSS 7.8). Both...
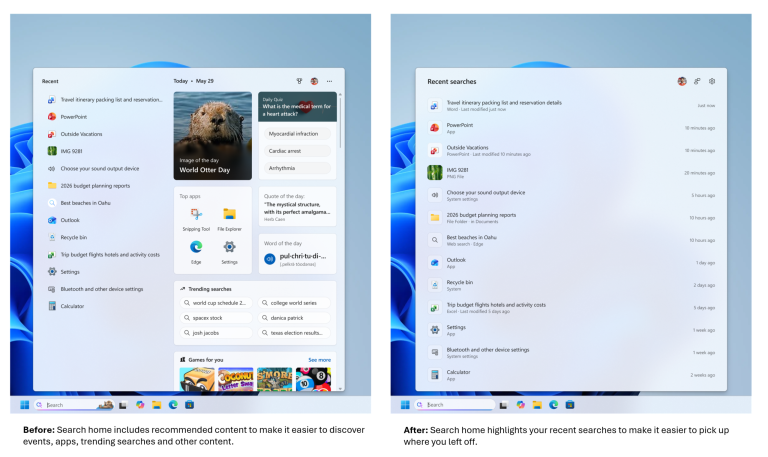
A Clean, Dedicated Search Utility Microsoft corporate executives recently published an official blog post detailing a refined...
Telegram is experiencing a service degradation caused by an external issue. Telegram’s t.me short domain has been...
SpaceXAI Responds to Rising Backlash Following intense weekend scrutiny, SpaceXAI finally issued an official statement regarding the...
TL;DR Netwrix has fixed two Netwrix Password Secure vulnerabilities disclosed in advisory ADV-2026-008. The most severe flaw,...
TL;DR ServiceNow has patched a critical ServiceNow sandbox escape flaw, tracked as CVE-2026-6875 (CVSS 9.5), in its...
TL;DR A critical Better Auth SSRF flaw, tracked as CVE-2026-53513, lets any logged-in user reach internal services....
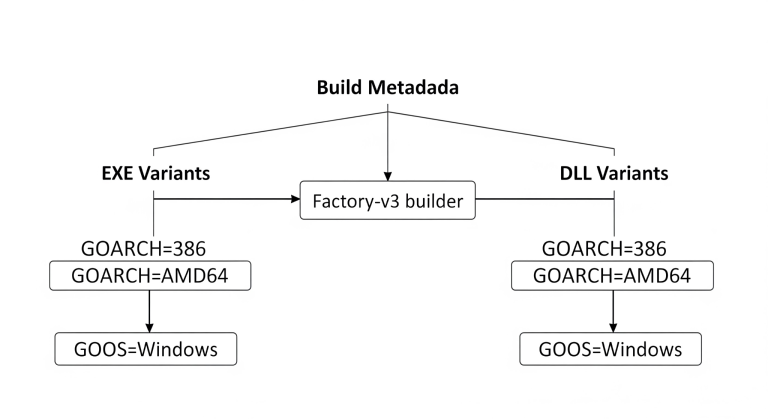
In April 2026, security researchers uncovered a massive Vidar stealer campaign distributing data theft and cryptocurrency mining...
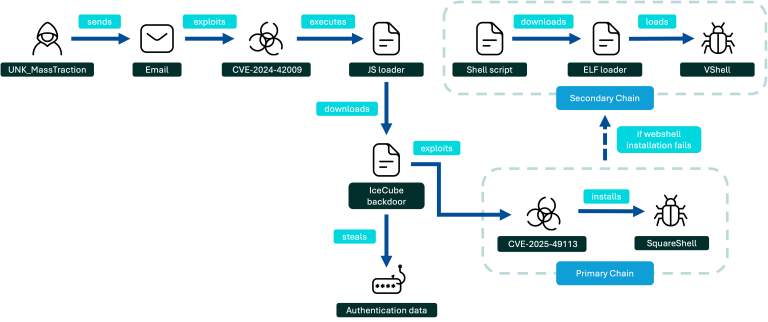
At a glance Actor UNK_MassTraction — suspected China-aligned espionage cluster Activity Roundcube exploitation for credential theft, webshells,...

At a glance Actor UAT-7810 — assessed China-nexus APT (Cisco Talos, high confidence) Activity Building and expanding...
Hydro-Québec recently disclosed a severe privilege escalation flaw impacting its electric vehicle charging network. This critical vulnerability...
As cyber threats continue to evolve, attackers are increasingly targeting people rather than technology alone. Social engineering...
At a Glance Malware Family: AsyncRAT Threat Actor: Unknown cybercriminals Target or Victims: Individual consumers and corporate...
Speeding Up Threat Hunts Microsoft recently shared insights on its smart systems. Thus, smart tech now hastens...
TL;DR Summary WatchTowr researchers disclosed a critical remote code execution flaw in Veeam Backup & Replication. The...