Skip to content
November 22, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
    • Citrix
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability News
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Cyber Security
  • BGP Hijack Factory on Portuguese company’s Bitcanal
  • Cyber Security

BGP Hijack Factory on Portuguese company’s Bitcanal

Do Son July 12, 2018 1 minute read
BGP Hijack

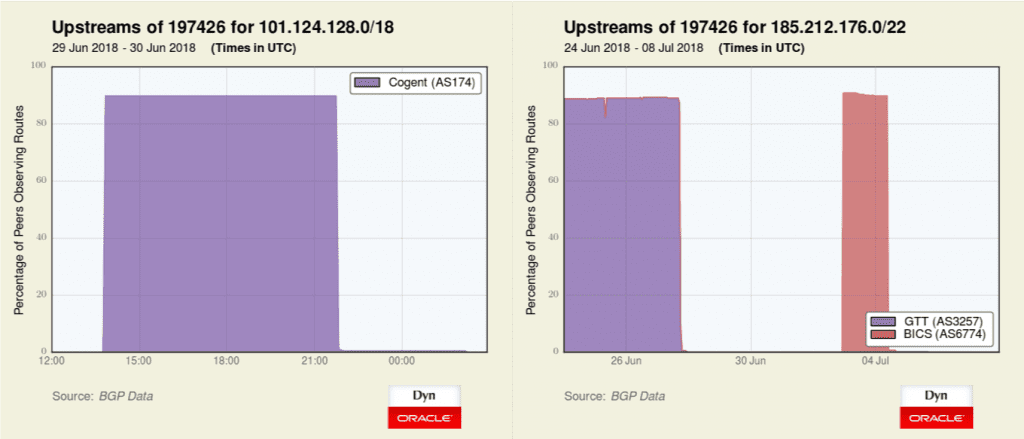
The notorious Portuguese hosting company Bitcanal was kicked out of the internet. Bitcanal has accused of helping spammers hijack IP segments for years, and its six upstream bandwidth providers have now decided to sever cooperation with the company. Because BGP works, a malicious attacker can declare some unused IP segments to the entire Internet to their hosting facilities. If there is no objection, then these IP segments will fall into the hands of the hijackers.

Security researchers have found that Bitcanal hijacks millions of IPv4 addresses and then sells or leases them to spammers to send spam. Most of the hijacked routes to Bitcanal’s IP address belong to organizations that no longer exist today, but many hijacked addresses are assigned to still active organizations, including the US Department of Defense.

Ron Guilmette, an anti-spam activist, an independent security researcher described Bitcanal’s suspicious activity on the NANOG mailing list on June 25th, asking why the company’s upstream network operators continued to hijack BGP routes. The discussion eventually led to Bitcanal. The upstream ISP terminated its cooperation with the company         

Add Daily CyberSecurity as a preferred source on Google
Why add Daily CyberSecurity as a preferred source?
  • See our zero-day and actively exploited CVE coverage more often in Google Top Stories.
  • Catch breaking security news from us as soon as it is published.
  • One click, free, and you can change or remove it anytime in your Google settings.
  • Your other sources stay. We only add ours.

Related coverage

  • $405 Million Forfeited: Texas Pharmacist’s Fraudulent Compound Cream Scheme Exposes Vulnerabilities in Healthcare Systems
  • ENISA Calls for Urgent Action as EU Cyberattacks Reach Record High
  • Kaspersky Lab: TetrisPhantom targets government entities in APAC
  • WazirX Faces Backlash Over Socialized Losses from $230M Cyberattack
  • GoSerpent Backdoor Drives a Patient Cyber Espionage Campaign Against Southeast Asian Governments
  • “OtterCookie” Malware Nibbles at Developers in “Contagious Interview” Campaign
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: BGP Hijack

🚨 Active Exploits in the Wild

  • CVE-2026-133968CVSS 9.8
    monailabel (aka MONAI Label) through 0.8.5 allows directory traversal, with resultant remote code execution, via the image parameter...
    Watchtower Verified📅 Updated: Nov 21, 2026
  • CVE-2025-42884CVSS 6.5
    SAP NetWeaver Enterprise Portal allows an unauthenticated attacker to inject JNDI environment properties or pass a URL used...
    CISA KEV📅 Added to KEV: Nov 20, 2026
  • CVE-2026-76466CVSS 9.8
    A vulnerability in the database service feature of Cisco Expressway Series could allow an unauthenticated, remote attacker with...
    CISA KEV📅 Added to KEV: Nov 20, 2026
  • CVE-2026-129448CVSS 9.8
    Deserialization of Untrusted Data in Apache Roller versions 4.0.0 through 6.1.4 allows an unauthenticated remote attacker to execute...
    CISA KEV📅 Added to KEV: Nov 20, 2026
  • CVE-2026-123890CVSS 9.8
    VMware vCenter contains an authentication bypass vulnerability in the VMware Directory Service. Affected versions: 9.1.x (fixed in 9.1.1.0200);...
    CISA KEV📅 Added to KEV: Nov 20, 2026
  • CVE-2026-114938CVSS 8.1
    Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java...
    Admin intel📅 Updated: Nov 19, 2026
  • CVE-2010-20126CVSS 5.1
    Virtual Keyboard plugin for SquirrelMail through 0.9.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20007CVSS 9.3
    ThinkPHP 2.0 through 2.2 and 3.0 Lite mode contains an eval injection vulnerability in the Dispatcher PATH_INFO parsing,...
    Watchtower Verified📅 Updated: Nov 18, 2026
Powered by CVE Watchtower

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Get free CVE alerts Pro from $7/mo

Critical Vulnerabilities

  • CVE-2026-99679CVSS 9.4
    In the Linux kernel, the following vulnerability has been resolved: xfs: refuse a pNFS LAYOUTCOMMIT of a range...
    📅 Updated: Nov 22, 2026
  • CVE-2026-99680CVSS 9.4
    In the Linux kernel, the following vulnerability has been resolved: xfs: mark the inode preallocated for pNFS write...
    📅 Updated: Nov 22, 2026
  • CVE-2026-99676CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: net: restore refcount ordering for lockless socket access...
    📅 Updated: Nov 22, 2026
  • CVE-2026-99634CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: mptcp: do not use Fast Open on MP_JOIN...
    📅 Updated: Nov 22, 2026
  • CVE-2026-99590CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ceph: clamp the inline data length in ceph_fill_inline_data()...
    📅 Updated: Nov 22, 2026
  • CVE-2026-99544CVSS 9.3
    In the Linux kernel, the following vulnerability has been resolved: Drivers: hv: vmbus: Bounds check the shared ring...
    📅 Updated: Nov 22, 2026
  • CVE-2026-99513CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: lockd: Fix use-after-free in nlmsvc_retry_blocked nlmsvc_retry_blocked() examines the...
    📅 Updated: Nov 22, 2026
  • CVE-2026-99370CVSS 9.4
    In the Linux kernel, the following vulnerability has been resolved: NFSD: copy SETXATTR data from all XDR buffer...
    📅 Updated: Nov 22, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.