 Do Son
Explore the rise of the Bloody Wolf cybercrime group and their evolution in targeting Russian organizations with advanced tactics.
Cyber Security
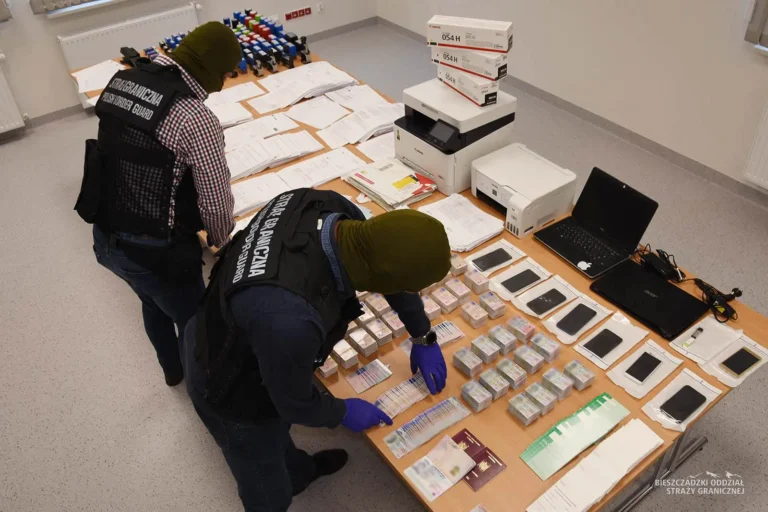
Europol's recent operation dismantled a criminal group involved in forgery and smuggling within the European Union.

Explore the allegations about the Equation Group's tactics in a new Chinese cybersecurity report regarding U.S. cyber operations.

Explore the activities of TA2726 and TA2727 as they utilize fake browser updates to spread malware and deceive users.

Explore the cyber espionage campaign REF7707, revealing novel malware and operational oversights by attackers in South America and Southeast Asia.

Learn about the StaryDobry Campaign and its impact on users worldwide through malicious torrent downloads of popular games.

Beware of the Amazon phishing scam targeting Prime users looking to steal your login and payment information.

Explore the findings on BitLaunch hosting provider and its potential links to ransomware activities in the cybercrime ecosystem.

Uncover the TRIPLESTRENGTH threat group. Learn about their ransomware tactics, cloud attacks, and illicit operations since 2020.

Amsterdam police shut down ZServers/XHost, a hub for cybercriminals that offered bulletproof hosting services to hackers.

Explore the activities of Emperor Dragonfly, a Chinese hacker group linked to ransomware and cyber espionage in 2024.

Understand the RedMike threat: a state-sponsored group exploiting Cisco vulnerabilities for persistent cyber espionage.

Uncover the EarthKapre cyber espionage campaign targeting organizations with stealthy techniques and sophisticated attacks.

Understand the malicious strategies employed by the Earth Preta APT Group, including the use of the TONESHELL backdoor for attacks.

Uncover the latest on Storm-2372, a phishing campaign exploiting device code authentication to access high-value targets.

Uncover the dangers of SEO Poisoning affecting Indian government and financial websites, redirecting users to scams.

Explore the risks of Device Code Authentication phishing targeted at Microsoft 365 users by Russian threat actors.

Uncover the dangers of the Astaroth Phishing Kit, which bypasses two-factor authentication to steal sensitive credentials.

Uncover the dangers of North Korea’s IT worker scam. Learn how it threatens global tech with espionage and fraud.

Uncover the threats posed by Seashell Blizzard, a cyber espionage group behind the BadPilot campaign targeting critical sectors.

Uncover the dangers of Adobe Drive X in the new phishing campaign targeting Microsoft users. Stay informed and secure.

Uncover the alarming details of a sophisticated phishing campaign targeting users through fake CAPTCHA images on Webflow CDN.