 Do Son
The Splunk Threat Research Team (STRT) has uncovered a new variant of a .NET steganographic malware loader...
Malware

A new macOS stealer campaign—internally dubbed “Nova” by researchers—has been uncovered by reverse engineer Bruce, revealing a...

Researchers from the Israel National Digital Agency (INDA) have revealed a highly sophisticated, ongoing cyber-espionage operation they...

Jamf Threat Labs has uncovered a new macOS infostealer—named DigitStealer—that demonstrates an unusually high degree of sophistication,...

Researchers at Palo Alto Networks Unit 42 have uncovered two expansive and interconnected malware campaigns active throughout...

eSentire’s Threat Response Unit (TRU) has uncovered a widespread malware operation leveraging a deceptive social-engineering technique known...

Elastic Security Labs has uncovered a highly sophisticated malware campaign led by the Dragon Breath APT group...

The United States Cybersecurity and Infrastructure Security Agency (CISA), alongside a coalition of global law-enforcement and cybersecurity...

Security researchers at NVISO have identified a significant evolution in the long-running Contagious Interview malware campaign, a...

In one of the largest open-source supply chain incidents ever recorded, Amazon Inspector security researchers have uncovered...

Trend Micro researchers have observed a significant resurgence in Lumma Stealer activity—also tracked as Water Kurita—despite a...
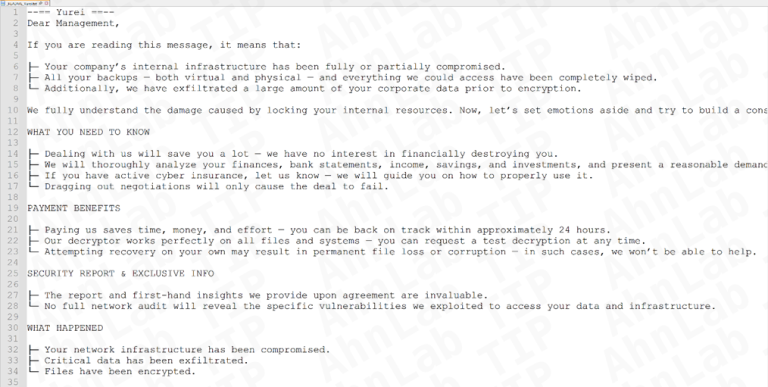
Security researchers at AhnLab have identified Yurei, a newly emerging ransomware group first observed in early September...

The Socket Threat Research Team has uncovered a highly sophisticated malicious Chrome extension posing as an Ethereum...

A new malware distribution trend is emerging across the macOS threat landscape, according to fresh research from...

Researchers from the AhnLab Security Intelligence Center (ASEC) have discovered a new malware campaign that abuses a...

The Lat61 Threat Intelligence Team has uncovered a new campaign using Bitcoin-themed lures to distribute DarkComet RAT,...

Researchers from the AhnLab Security Intelligence Center (ASEC) have uncovered a new malware campaign exploiting Remote Monitoring...

The Genians Security Center (GSC) has uncovered a new phase in the KONNI APT campaign, revealing a...

Cybersecurity researchers at ENKI have identified a new variant of the Comebacker backdoor, attributed to the North...

The Acronis Threat Research Unit (TRU) has identified a new DragonForce ransomware variant that showcases a dramatic...

Researchers from Unit 42, the threat intelligence team at Palo Alto Networks, have discovered a previously unknown...

Researchers at zLabs have uncovered a sophisticated Android Remote Access Trojan (RAT) known as Fantasy Hub, being...