
 Do Son
SUSE patches three flaws in Rancher Manager. A phishing vulnerability (CVSS 8.1) can steal admin tokens, while a DoS flaw can lock out administrators.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Formbricks has a critical auth flaw (CVSS 9.4) in its JWT validation. Attackers can forge tokens to reset user passwords and achieve full account takeover.

Rack patches CVE-2025-59830 (CVSS 7.5), a flaw where attackers could use semicolon separators to bypass the parameter count limit and trigger DoS attacks.

Cisco patches a Critical 9.9 zero-day (CVE-2025-20333) in ASA/FTD VPN web servers. Authenticated attackers can exploit the flaw for root-level Remote Code Execution.
Cisco disclosed a Critical RCE flaw in its Firewall ASA/FTD, IOS, IOS XE, and IOS XR web services. Unauthenticated attackers can gain root access.

Cisco patches CVE-2025-20362, a medium-high zero-day vulnerability in ASA/FTD VPN web servers that is being exploited to gain unauthorized access to restricted resources.

Apache Airflow 3.0.3 has a bug (CVE-2025-54831) exposing sensitive connection details, including passwords, to all users with only READ permissions. Update immediately.

GitLab urges immediate upgrade to patch versions 18.4.1+ for high-severity DoS flaws that allowed unauthenticated attackers to crash self-managed instances.

NVIDIA released an urgent update for its Megatron-LM LLM framework, patching four high-severity code injection flaws that could allow attackers to compromise AI workflows.

Two WordPress Core vulnerabilities (XSS and Info Exposure) affecting versions up to 6.8.2 were accidentally exposed before patches were ready.

A critical SNMP flaw (CVE-2025-20352) in Cisco IOS/IOS XE is being actively exploited, allowing attackers root access. Urgent patching and mitigation required!

A critical flaw (CVE-2025-41715) in WAGO Device Sphere allows an unauthenticated remote attacker to gain unauthorized access and potentially compromise its database.

CISA has added a high-severity V8 zero-day (CVE-2025-10585) to its exploited vulnerabilities catalog. An urgent Chrome update is available to patch the flaw.
A high-severity flaw in the Salesforce CLI installer (CVE-2025-9844) allows for arbitrary code execution and privilege escalation on affected systems.

A critical, unpatched OnePlus flaw (CVE-2025-10184) allows any app to read SMS data without permission, breaking MFA protections. PoC is available.

A critical XSS flaw (CVE-2025-59545) in DNN's Prompt module allows attackers to execute code and hijack admin sessions. All users must update immediately.

Google has released an urgent update for Chrome, patching three high-severity flaws in its V8 JavaScript engine, two of which were discovered by AI.

SolarWinds has released an urgent hotfix for its Web Help Desk software, patching an unauthenticated RCE vulnerability (CVE-2025-26399) that bypasses earlier fixes.

A critical XSS flaw in the Lectora e-learning platform (CVE-2025-9125) allows for malicious code injection, posing a risk of session hijacking and redirection.

Libraesva has issued an urgent advisory for a command injection flaw in its ESG. The bug, which has been exploited, allows remote command execution via a malicious email.
CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide
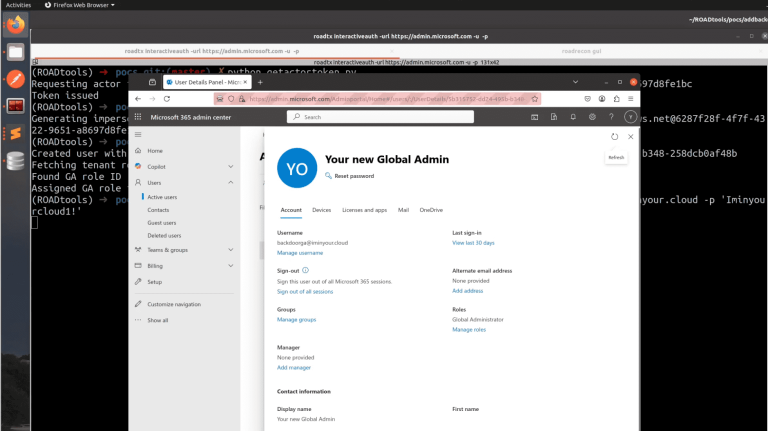
CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide
A critical flaw (CVE-2025-55241) in Microsoft Entra ID could have allowed a compromise of every tenant worldwide by bypassing security with "Actor tokens."
A decade-old browser flaw, "BiDi Swap," allows attackers to craft deceptive URLs for phishing. The bug, found by Varonis, exploits mixed-text direction.