
 Do Son
A new report reveals a CWMP service flaw in TP-Link routers that can be exploited for RCE. Researchers have published a detailed write-up and a PoC on GitHub.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

CISA warns of critical vulnerabilities in ProGauge MagLink fuel monitors, leaving fuel stations and industrial sites at risk of denial-of-service and unauthorized access.

Nokia has issued a security advisory for two high-severity flaws (RCE and authentication bypass) in its CBIS and NCS platforms. Immediate patching is urged.

A critical vulnerability in HubSpot’s Jinjava template engine (CVE-2025-59340) could lead to remote code execution. Patch immediately to secure your site.

A new 10.0 CVSS score vulnerability in Fortra's GoAnywhere MFT platform allows attackers to execute remote code. Learn how to protect your systems now.

CISA issued a security advisory for Delta Electronics DIALink vulnerabilities, including a critical 10.0 CVSS flaw that could allow authentication bypass.

Jenkins has patched multiple flaws, including a high-severity DoS vulnerability in its bundled Jetty server that could allow unauthenticated attackers to crash the service.

Google has released an urgent Chrome update, patching a V8 zero-day (CVE-2025-10585) being exploited in the wild, along with other high-severity flaws.

Two critical vulnerabilities in Planet Technology’s Industrial Cellular Gateways could allow unauthenticated attackers to take over devices, exposing critical infrastructure.

A new Rowhammer attack, "Phoenix," bypasses DDR5 protections on all tested SK Hynix devices, enabling memory corruption and privilege escalation.
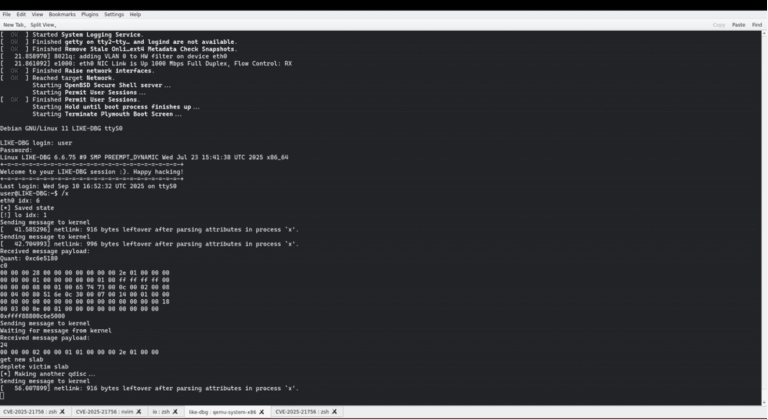
A new Linux kernel vulnerability, CVE-2025-21692, can be exploited to achieve remote code execution by manipulating the ETS qdisc, a simple but critical flaw.

A critical vulnerability (CVE-2025-9242) in WatchGuard's Fireware OS could allow an unauthenticated remote attacker to execute arbitrary code.

NVIDIA has released a critical security update for its Triton Inference Server, fixing multiple high-severity flaws that could lead to remote code execution and DoS.

HPE Aruba Networking has patched multiple high-severity flaws in its SD-WAN gateways. The bugs could lead to RCE, privilege escalation, and unauthorized access.

A medium-severity vulnerability (CVE-2025-9708) in the Kubernetes C# client allows MITM attacks and API impersonation. Update now to patch.

A new Linux kernel flaw, CVE-2025-38501, exposes KSMBD servers to unauthenticated remote DoS attacks. A public PoC is available now.

A critical flaw in the Case Theme User WordPress plugin (CVSS 9.8) allows unauthenticated attackers to hijack admin accounts. The vulnerability is under active exploitation.

Two medium-severity flaws in Spring Security and the Spring Framework allow authorization bypasses in applications that use method-level security on generic types.

A new report details a 0-click RCE exploit chain in the Linux kernel's ksmbd module that allows an authenticated user to gain root access. A PoC has been published.

Samsung has released an emergency patch for a critical zero-day vulnerability (CVE-2025-21043) actively exploited in Android devices. Update now to protect against RCE attacks.

A critical flaw (CVE-2025-58434) in FlowiseAI allows unauthenticated attackers to hijack any account. The bug has a CVSS 9.8 score, and a PoC has been released.

Two critical vulnerabilities (CVSS 10 & 9.8) in Digiever NVRs allow unauthenticated attackers to steal credentials and execute commands. Update your firmware immediately.