
 Do Son
Critical VS Code Live Server flaw CVE-2025-65717 (CVSS 9.1) lets attackers steal source code and credentials via malicious links. Protect your workspace now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

Splunk Enterprise Windows flaws (CVSS 7.7) CVE-2026-20143 & CVE-2026-20140 allow system takeover via DLL and Python search path hijacking. Patch immediately.

Critical Pterodactyl API flaw (CVE-2026-26016) allows cross-node authorization bypass. Attackers can destroy game servers. Update to version 1.12.1 now.

Node.js DoS flaw CVE-2026-26278 in fast-xml-parser freezes event loops via XML entity expansion. 46M weekly downloads affected. Update to version 5.3.6.

Apache Camel patches critical flaws in Keycloak (CVE-2026-23552) and LevelDB (CVE-2026-25747) components that allow auth bypass and RCE. Update to 4.18.0.
Jenkins patches a high-severity stored XSS flaw (CVE-2026-27099) and an info disclosure bug. Update to version 2.551 or LTS 2.541.2 to secure pipelines.

Google releases an urgent Chrome update to patch high-severity flaws in PDFium (CVE-2026-2648) and the V8 engine (CVE-2026-2649). Update to 145 now.

NVIDIA warns of 7.8-rated vulnerabilities in Megatron Bridge. Learn how "educational" tutorials could let attackers hijack your AI training infrastructure.

CISA warns of Honeywell CCTV flaw CVE-2026-1670. Unauthenticated attackers can reset passwords & hijack feeds. Update firmware immediately.

Urgent: PostgreSQL patches 5 flaws, including 3 critical RCEs (CVSS 8.8). Attackers can execute code as OS user via text manipulation. Update v14-18.
Mandiant reveals UNC6201 exploiting Dell RecoverPoint zero-day CVE-2026-22769. Attackers use "Ghost NICs" & GRIMBOLT malware. Patch now.

Ivanti EPMM under attack via zero-days CVE-2026-1281 & 1340. Hackers use bash scripts to plant dormant backdoors. Patch immediately.

CISA adds 4 flaws to KEV: Ancient Windows ActiveX bug (CVE-2008-0015) & new Chrome zero-day (CVE-2026-2441). Patch now to prevent exploitation.

Apache NiFi flaw CVE-2026-25903 allows unauthorized users to modify restricted components. Update to version 2.8.0 immediately to secure data pipelines.
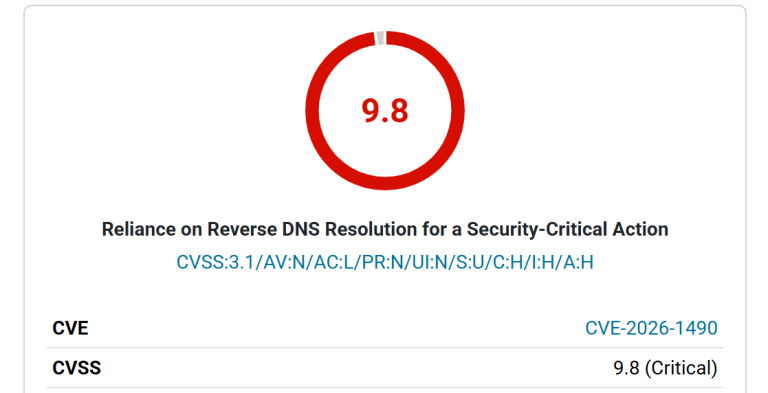
CleanTalk flaw CVE-2026-1490 (CVSS 9.8) exposes 200k sites to RCE via DNS spoofing. Attackers bypass auth to install plugins. Update to v6.72 now.

CISA warns of critical Airleader Master vulnerability CVE-2026-1358. Unauthenticated attackers can upload files and gain RCE. Update to 6.386 now.

Critical FileZen flaw CVE-2026-25108 is under active attack. Antivirus feature allows command injection. Update to V5.0.11 immediately to secure data.
CISA warns of critical ZLAN5143D flaws CVE-2026-25084 & CVE-2026-24789. Attackers can bypass login & reset passwords. Isolate devices now.
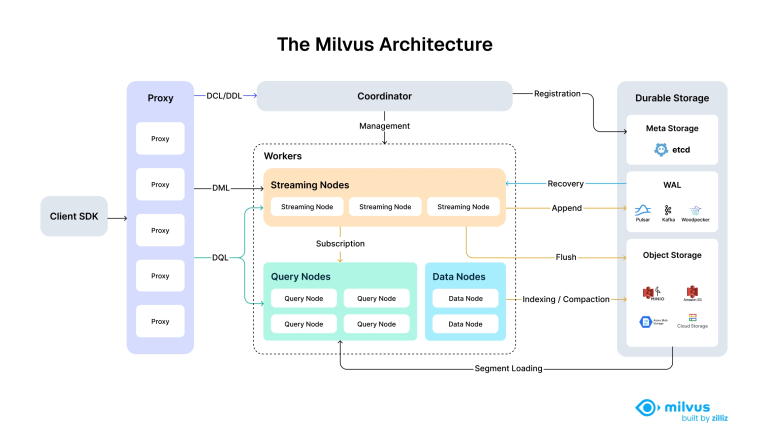
Critical Milvus flaw (CVSS 9.8) exposes port 9091. Unauthenticated attackers can steal secrets & delete data. Update to v2.5.27 or v2.6.10 immediately.
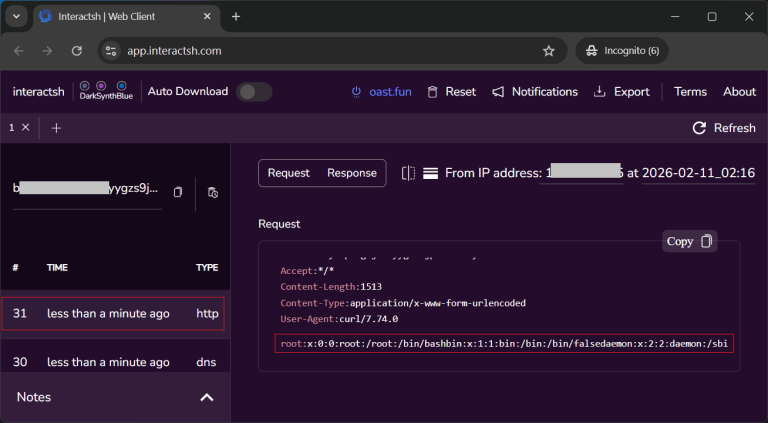
Arctic Wolf warns of CVE-2026-1731, a critical BeyondTrust flaw exploited in the wild. Attackers use it to deploy backdoors. Patch self-hosted instances now.

Google patches critical zero-day CVE-2026-2441. Attackers are exploiting this CSS use-after-free flaw in the wild. Update to Chrome 145 immediately.

Zimbra 10.1.16 patches critical XSS, XXE, and LDAP injection flaws. Update immediately to secure your email collaboration suite and restore PDF previews.