
 Do Son
A critical 9.3 CVSS XSS vulnerability (CVE-2026-29191) in ZITADEL's SAML endpoint allows unauthenticated 1-click account takeover. Upgrade immediately.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

A critical 9.8 CVSS flaw (CVE-2026-27944) in Nginx UI lets hackers download and decrypt full system backups via an open API. Update and rotate secrets!
CERT/CC reveals a major privacy flaw (CVE-2025-13476) in Viber's Cloak mode, allowing network censors to easily identify and block proxy traffic. Update now.

A new Check Point Research report reveals how Iranian-nexus threat actors compromise IP cameras in the Middle East for real-time missile reconnaissance.

A critical 9.8 CVSS flaw (CVE-2026-29058) in AVideo-Encoder allows unauthenticated remote attackers to execute arbitrary system commands. Patch now.

Researchers discovered three major flaws in Amazon’s AWS-LC cryptographic library, allowing hackers to bypass digital signature validation. Update now.

A critical 10.0 CVSS flaw (CVE-2026-20127) in Cisco Catalyst SD-WAN is actively exploited in the wild. A public PoC is now available. Patch immediately!
An integer overflow flaw (CVE-2025-66168) in Apache ActiveMQ's MQTT module allows authenticated attackers to crash brokers. Update your systems immediately.

Cisco warns that two vulnerabilities (CVE-2026-20122 and CVE-2026-20128) in its Catalyst SD-WAN Manager are being actively exploited. Update immediately.
A critical 10.0 CVSS zero-click flaw (CVE-2026-20079) in Cisco Secure FMC gives unauthenticated attackers root access. Patch your systems immediately.
A critical 10.0 CVSS flaw (CVE-2026-29000) in the pac4j-jwt library allows attackers to forge JWTs and bypass authentication. Patch immediately.

Google releases an urgent security update for Chrome, patching 10 flaws including 3 critical memory corruption vulnerabilities. Update to version 145 now.
A critical 10.0 CVSS unauthenticated RCE flaw (CVE-2026-20131) in Cisco Secure FMC allows hackers root access via insecure Java deserialization. Patch now.
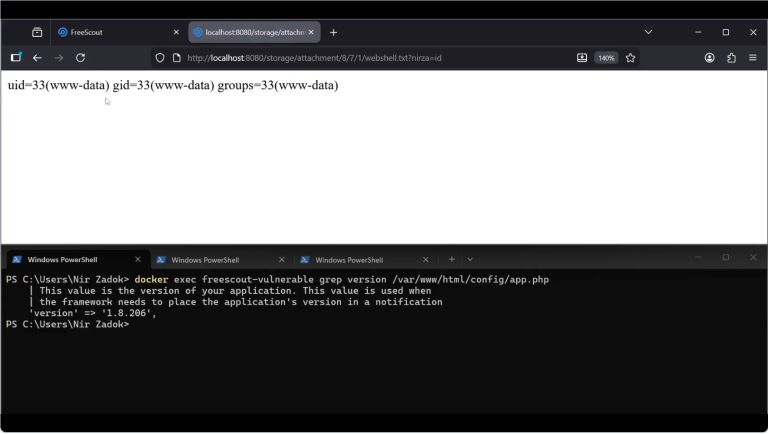
A critical 10.0 CVSS unauthenticated remote code execution flaw (CVE-2026-28289) in FreeScout allows full server takeover via an invisible character exploit.
A critical 9.4 CVSS flaw (CVE-2026-1775) in Labkotec LID-3300IP ice detectors allows hackers to hijack wind turbines and airports. Hardware upgrade needed.

Google Threat Intelligence uncovers "Coruna", a repurposed iOS exploit kit now used by state-sponsored and financially motivated hackers to steal crypto.

Critical authentication flaws (CVE-2026-26288) in Everon's OCPP backend allowed hackers to hijack EV chargers, forcing a complete platform shutdown.
Nokia discovers a critical 9.1 RCE flaw (CVE-2026-28370) in OpenStack Vitrage's RCA service. Patch immediately to prevent total host server takeovers.

Django releases security updates (6.0.3, 5.2.12, 4.2.29) to fix a Windows DoS flaw (CVE-2026-25673) and file permission risks. Upgrade your framework now.

CISA adds actively exploited Qualcomm (CVE-2026-21385) and VMware (CVE-2026-22719) flaws to its KEV catalog. See the impact and patch deadlines inside.
AVideo patches two critical flaws (CVE-2026-28501 & 28502) allowing unauthenticated SQL injection and remote code execution. Update to version 23 now.

A critical 9.8 CVSS flaw (CVE-2026-1492) in the WordPress User Registration & Membership plugin lets unauthenticated attackers create admin accounts.