 Do Son
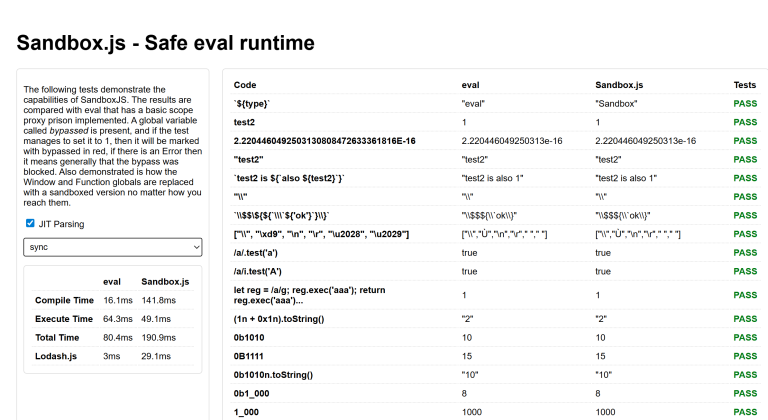
Critical 10.0 CVSS flaw in SandboxJS (CVE-2026-26954) allows attackers to escape the sandbox and achieve Remote Code Execution. Patch to version 0.8.34 now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

SentinelOne DFIR reveals how attackers exploit FortiGate NGFW flaws to extract credentials, abuse Active Directory, and establish persistent network access.
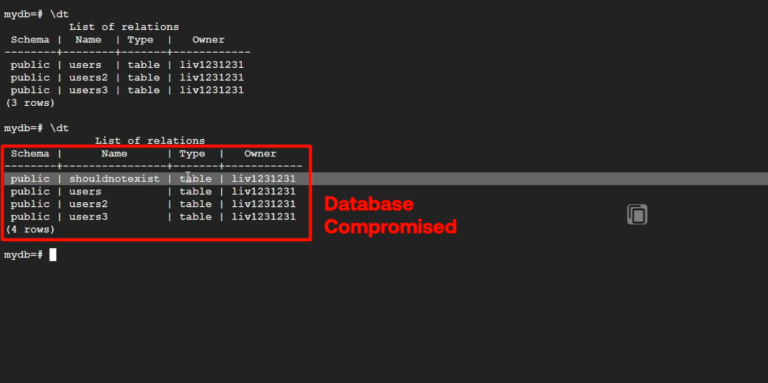
Tenable exposes "LeakyLooker"—9 cross-tenant flaws in Google Looker Studio that let hackers manipulate and exfiltrate GCP data. Google has patched them.
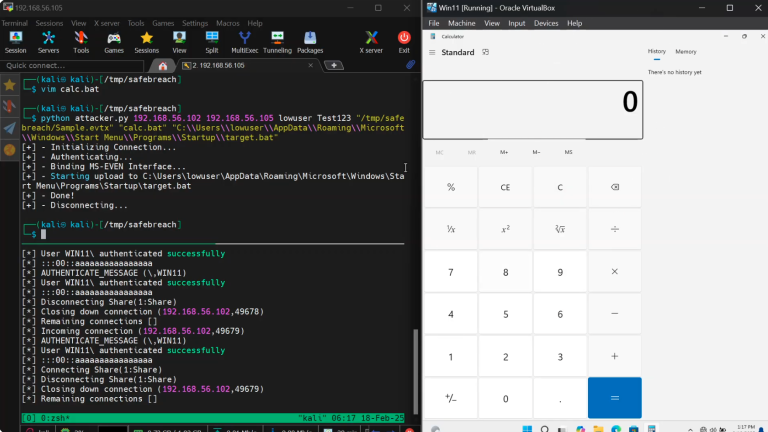
SafeBreach Labs releases PoC exploit code for EventLogin (CVE-2025-29969), a TOCTOU flaw in Windows MS-EVEN RPC allowing remote file writes. Patch now.

Ledger Donjon uncovers a critical MediaTek TEE flaw allowing attackers to extract PINs and crypto seed phrases in 45 seconds. Patch now.
A critical 9.8 CVSS vulnerability (CVE-2026-32136) in AdGuard Home lets unauthenticated attackers hijack network DNS settings. Update to v0.107.73 now.

Winter CMS urgently patches a critical 10.0 CVSS privilege escalation flaw (CVE-2026-27591) allowing low-level backend users to gain full system control.

Veeam urgently patches critical 9.9 CVSS RCE flaws (CVE-2026-21666, CVE-2026-21708) in Backup & Replication 12.3.2. Update your servers immediately.
Apple releases emergency iOS 15.8.7 and 16.7.15 updates for older iPhones to block the actively exploited "Coruna" WebKit and Kernel exploit kit. Patch now.

CrackArmor exposes 12.6M Linux servers to root escalation. Qualys TRU discovers 9 AppArmor flaws letting users bypass security and escape containers.

Protect your Spark clusters: Apache Livy 0.9.0 patches two important file access and path traversal vulnerabilities (CVE-2025-60012 & CVE-2025-66249).

Veeam releases a critical security update fixing 9.9 CVSS RCE flaws (CVE-2026-21669, CVE-2026-21708) in Backup & Replication. Patch servers immediately.

A pre-auth flaw in OpenSSH's GSSAPI Key Exchange (CVE-2026-3497) exposes Ubuntu and Debian servers to heap corruption and data leaks. Patch now.

Google releases an emergency Chrome update to patch two actively exploited zero-day vulnerabilities (CVE-2026-3909 & CVE-2026-3910). Update immediately.
A critical 9.4 CVSS tag poisoning attack (CVE-2026-31976) hit the xygeni-action GitHub Action, injecting a C2 backdoor into CI/CD pipelines. Update now.
CISA warns of a critical 10.0 CVSS RCE flaw (CVE-2025-68613) in n8n workflow automation. Update to version 1.122.0 immediately to prevent server takeover.

Splunk warns of a high-severity RCE flaw (CVE-2026-20163) in its REST API. Attackers with edit_cmd rights can execute arbitrary commands. Patch immediately.
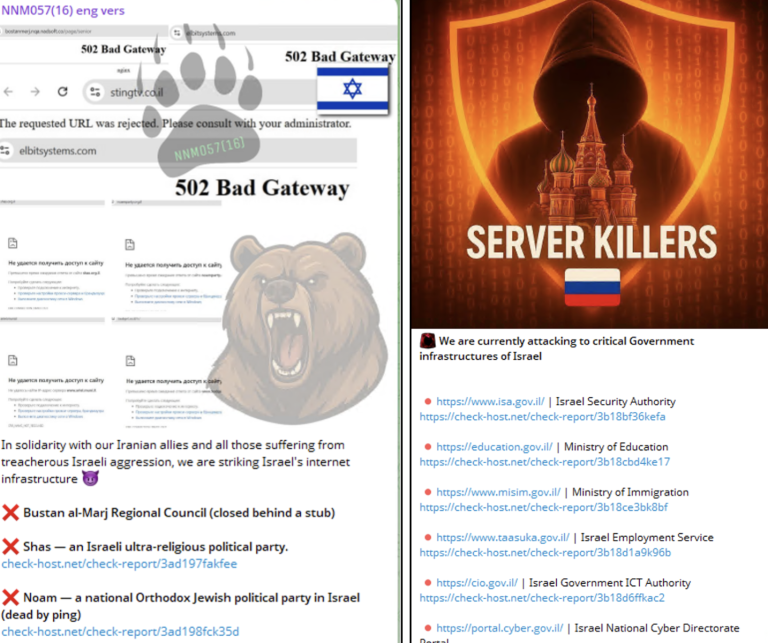
Rapid7 reveals a surge in state-directed cyber espionage and noisy hacktivism. Learn how actors like MuddyWater exploit critical CVEs to breach networks.
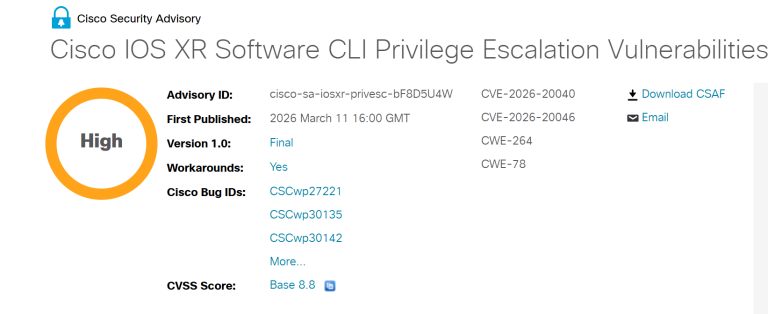
Cisco patches critical privilege escalation flaws (CVE-2026-20040, CVE-2026-20046) in IOS XR software that allow local attackers to gain full root access.

Google releases Chrome 146, fixing 29 vulnerabilities including a critical heap buffer overflow in WebML (CVE-2026-3913). Update your browser immediately.

GitLab issues urgent security updates (18.9.2, 18.8.6, 18.7.6) fixing critical XSS (CVE-2026-1090) and DoS flaws. Patch self-managed instances today.

HPE Aruba patches a critical 9.8 CVSS bypass in AOS-CX switches that allows unauthenticated password resets. Upgrade to 10.17.1001+ to secure your network now.