
 Do Son
Active exploitation alert: The PolyShell flaw in the Magento REST API allows unauthenticated RCE via malicious images. Learn how to protect your store now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Industrial connectivity specialist Helmholz GmbH & Co. KG has issued an urgent security advisory regarding multiple vulnerabilities...

TP-Link releases critical firmware updates for Archer NX200, NX210, NX500, and NX600 models to patch authentication bypass and command injection flaws.

Spring Cloud Config faces a high-severity CVSS 8.6 flaw (CVE-2026-22739). Attackers can manipulate profiles to access local files or launch SSRF attacks.

Google releases Chrome 146.0.7680.164/165, patching 8 high-severity flaws including use-after-free and buffer overflows. Update your desktop browser now.

Cloud Software Group warns of a critical 9.3 CVSS memory overread in NetScaler. Patch now to prevent data exposure and session hijacking.

Wazuh patches two critical 9.1 CVSS flaws (CVE-2026-25769 & CVE-2026-25770) allowing total cluster takeover. Upgrade to v4.14.3 now to stay protected.
A critical 9.1 CVSS flaw in gRPC-Go (CVE-2026-33186) allows attackers to bypass authorization by omitting a leading slash. Upgrade to v1.79.3 immediately.
Roundcube v1.6.14 patches a critical pre-authentication file write flaw and account hijacking bugs. Secure your webmail server with this high-priority update.

A critical 10.0 CVSS flaw in WAGO managed switches (CVE-2026-3587) allows unauthenticated remote takeover via an undocumented CLI backdoor. Update immediately.
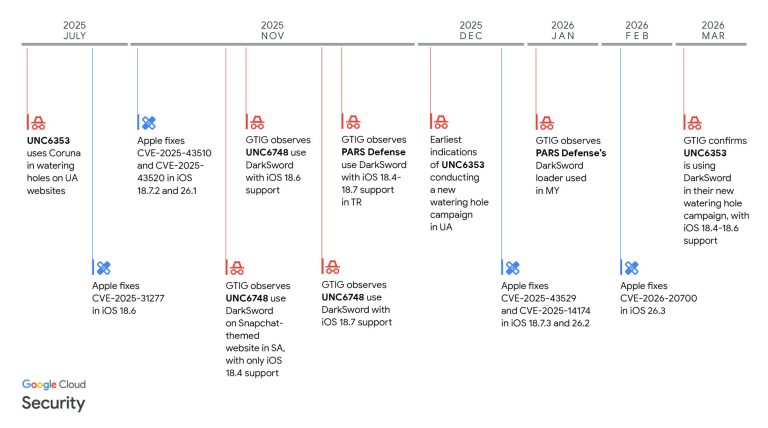
Google uncovers DarkSword, a sophisticated iOS full-chain exploit used globally to deploy spyware via zero-day vulnerabilities. Update to iOS 26.3 now.

Rockwell Automation issues an urgent warning: disconnect industrial controllers from the internet immediately to protect against active threat actors.
Eclypsium researchers reveal how compromised IP-KVM switches bypass EDR and software security to grant attackers total, BIOS-level system takeover.
CISA adds 5 actively exploited flaws to its KEV catalog, including a critical 10.0 CVSS Craft CMS bug and Apple zero-days linked to DarkSword malware.

Netwrix issues an urgent advisory for critical vulnerabilities in its Password Secure platform allowing arbitrary code execution. Update to v26.3.100 now.

QNAP warns of a critical 9.3 CVSS flaw (CVE-2026-22898) allowing remote attackers to bypass authentication and access QVR Pro surveillance systems. Patch now.

Oracle warns of a critical 9.8 CVSS vulnerability (CVE-2026-21992) allowing unauthenticated attackers to take over Fusion Middleware and Identity Manager.

PoC exploit code is now public for CVE-2026-20643. Apple issues its first Background Security Improvement to fix this cross-origin Navigation API flaw.
Two high-severity flaws (CVE-2026-22731 & CVE-2026-22733) in Spring Boot Actuators allow authentication bypass. Update your framework today to stay secure.

Exploit code and details for CVE-2025-59284 are now public. Discover how a Windows libarchive flaw leaks NetNTLMv2 hashes via malicious .tar archives.

A high-severity 8.8 CVSS flaw (CVE-2026-4342) in ingress-nginx allows attackers to inject malicious code and steal Kubernetes Secrets. Patch immediately.

Proofpoint details 'CursorJack', a novel exploit using malicious MCP deeplinks in the Cursor AI editor to execute arbitrary code on developer machines.