
 Do Son
Fortinet warns CVE-2026-35616 (CVSS 9.1) in FortiClient EMS is being exploited in the wild. Unauthenticated RCE risk—apply emergency hotfixes immediately!
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

Apache Traffic Server fixes two CVSS 7.5 flaws (CVE-2025-58136 & CVE-2025-65114). Prevent DoS and request smuggling—update to 10.1.2 or 9.2.13 now!
Payload CMS fixes a critical 9.1 CVSS flaw (CVE-2026-34751) in its password reset flow. Attackers could hijack accounts. Update to v3.79.1 immediately!

Juju hits a perfect 10.0 CVSS score (CVE-2026-4370). A TLS flaw on port 17666 lets attackers hijack clusters. Update to 3.6.20 or 4.0.5 now!

Critical 8.8 CVSS flaw in libinput allows sandbox escape via malicious Lua plugins. Affects GNOME, KDE, and Fedora. Update to 1.31.1 or 1.30.3 now!
Artifex MuPDF faces a 7.8 CVSS integer overflow (CVE-2026-3308) allowing RCE via "crafted" PDFs. With no official patch, sandboxing is vital. Update now.

OpenSSH 10.3 fixes critical gaps, including client-side command execution and scp privilege escalation flaws. Update your remote access stacks immediately.

Progress ShareFile hit by critical 9.8 CVSS RCE flaws (CVE-2026-2699). Unauthenticated attackers can hijack configuration and execute code. Update to v5.12.4!

TP-Link warns of high-severity flaws (CVSS 8.7) in Tapo C520WS cameras. Attackers can bypass auth or blind your security. Update to firmware 1.2.4 now!
A critical 8.1 CVSS flaw in Perfmatters (200k+ installs) allows unauthenticated attackers to delete wp-config.php and hijack sites. Update to 2.6.0 now!

Joomla releases critical 8.6 CVSS patches for CVE-2026-23898 & CVE-2026-23899. Prevent arbitrary file deletion and API leaks—update to 5.4.4 or 6.0.4 today!

Lodash (CVE-2026-4800) faces an 8.1 CVSS code injection flaw in the _.template function. Attackers can bypass validation via imports. Update to 4.18.0 now!

NVIDIA fixes high-severity vulnerabilities (CVSS 8.3) in Jetson Linux for Xavier, Orin, and Thor. Protect your autonomous systems—update to 36.5 or 35.6.4.
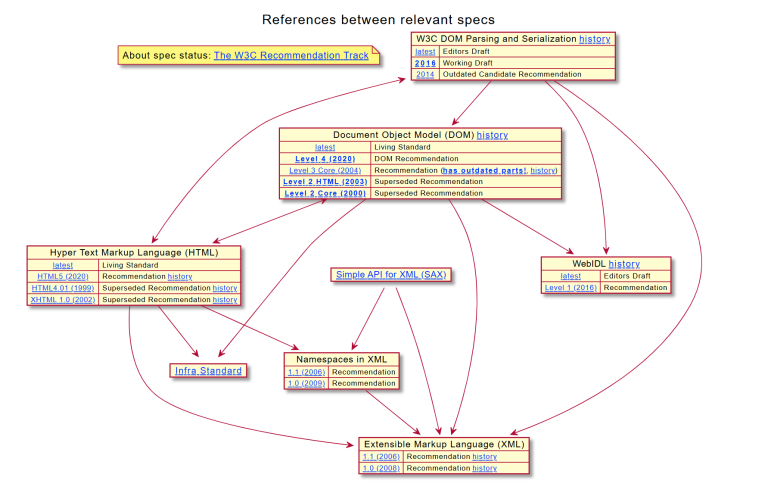
Fix CVE-2026-34601 in @xmldom/xmldom (CVSS 7.5). A CDATA injection flaw allows attackers to bypass "safe zones" and manipulate business logic. Update now!

CISA alerts to a 9.8 CVSS flaw in Anritsu Spectrum Monitors (CVE-2026-3356). No patch is coming for this authentication bypass. Secure your network now!

Apple releases iOS 18.7.7 to combat the "DarkSword" exploit kit. Protect your legacy iPhone or iPad from this state-level threat by updating today.

Gigabyte Control Center faces a critical 9.2 severity flaw (CVE-2026-4415). Unauthenticated attackers can write files and execute code—update to 25.12.10.01 now.

Cisco patches a critical 9.8 CVSS flaw (CVE-2026-20093) in IMC. Unauthenticated attackers can change admin passwords and seize full control. Update now!

Cisco patches a critical 9.8 CVSS flaw (CVE-2026-20160) in SSM On-Prem. Unauthenticated attackers gain root access via exposed APIs. Update to 9-202601 now!

Kaspersky reveals Coruna, an elite iOS exploit kit targeting A17 & M3 chips. Reusing Operation Triangulation flaws, it’s now hitting the mainstream. Patch now!


NocoBase patches a CVSS 10.0 RCE vulnerability (CVE-2026-34156). A simple console object bypasses the sandbox for root access. Update to 2.0.28 now!