
 Do Son
Movable Type patches a critical 9.8 CVSS RCE vulnerability in its Listing Framework. Secure your CMS against Perl code execution and SQLi—update today!
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

Apache Tomcat discloses 10 vulnerabilities including encryption bypasses and Kubernetes token leaks. Upgrade now to secure your Java-based web applications.

A critical CVSS 10 flaw in Axios (CVE-2026-40175) allows attackers to bypass AWS IMDSv2 and achieve RCE via header injection. Upgrade to v1.15.0 now!
Nix patches a critical 9.0 CVSS sandbox escape. Learn how CVE-2026-39860 allows unprivileged users to seize root control via symlink manipulation. Update now!

Checkmk patches a critical 9.3 CVSS local privilege escalation flaw in the 'omd' command. Stop site users from seizing root access—update your sites today!

HPE Aruba Networking patches a critical 8.8 CVSS open redirect in its Private 5G Core. Prevent credential harvesting—update to version 1.25.3.1 immediately.

TP-Link urges Archer AX53 v1.0 users to update firmware to fix 5 critical flaws, including OS command injection & file leaks. Secure your network now!
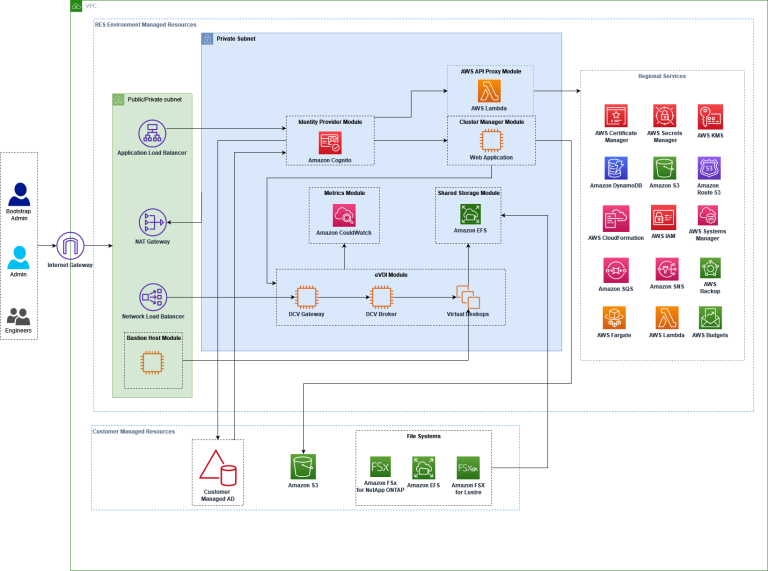
AWS patches critical RES flaws (CVE-2026-5707/8/9) allowing root access and instance profile hijacking. Protect your cloud lab—update to v2026.03 now.
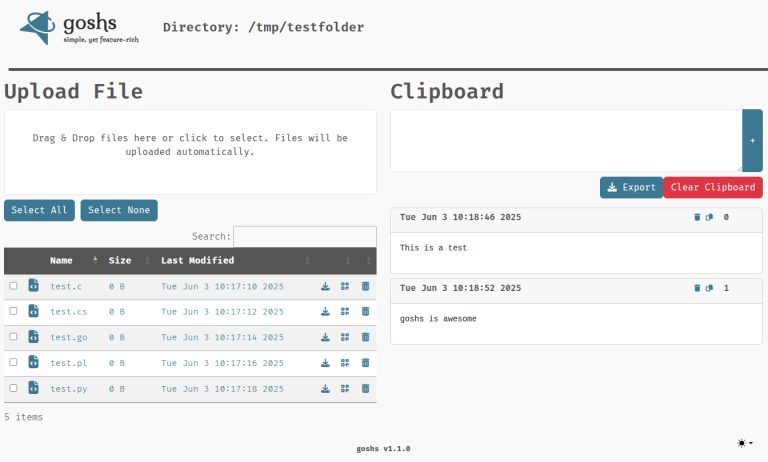
Critical 9.8 flaws in goshs v2.0.0-beta.2 allow unauthenticated attackers to write or delete any file on your system. Update to v2.0.0-beta.3 immediately!

Juniper warns of a critical 9.8 CVSS flaw in JSI vLWC. A default password allows unauthenticated attackers to take full device control. Update to 3.0.94 now!
Everest Forms patches a critical 9.8 CVSS PHP Object Injection vulnerability affecting 100,000+ sites. Update to v3.4.4 now to prevent full site takeover!
Vite patches critical flaws (CVE-2026-39364 & CVE-2026-39363) allowing arbitrary file reads and .env leaks via WebSockets and query params. Upgrade to 8.0.5!

React patches a 7.5 CVSS DoS vulnerability in Server Components (CVE-2026-23869). Stop CPU exhaustion attacks—update your 19.x dependencies now!

Critical 9.3 CVSS flaw (CVE-2026-34078) in Flatpak allows apps to escape sandboxes and access all host files. Secure your Linux system—update to v1.16.4 now!

Palo Alto Networks patches critical flaws in Cortex XDR and ADEM, including a SYSTEM-level privilege escalation. Secure your security tools—patch today!

GitLab releases critical patches (18.10.3+) for WebSocket flaws, Terraform DoS, and unauthorized privilege demotions. Update your self-managed instances!

SonicWall patches critical SMA 1000 flaws, including a 7.2 SQL injection for privilege escalation and Unicode-based MFA bypasses. Secure your VPN—update now!
Google Chrome 147 is out with critical security fixes for WebML and V8. Protect your browser from overflows and memory leaks—update to version 147 now!

CISA adds critical Ivanti EPMM flaw (CVE-2026-1340) to KEV catalog. The 9.8 CVSS code injection allows unauthenticated RCE. Patch mandated by April 11!
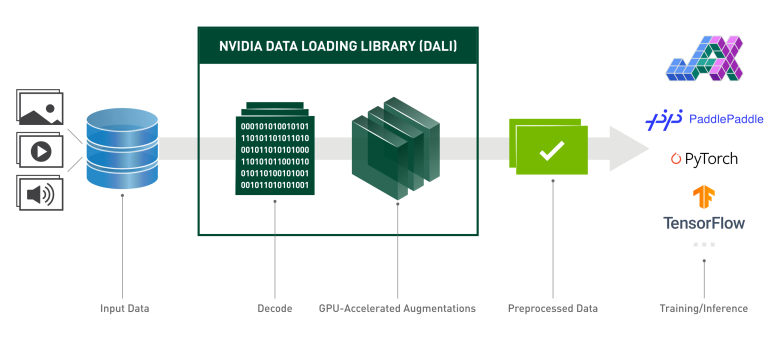
NVIDIA patches high-severity flaws in DALI and Triton Inference Server. Prevent arbitrary code execution and DoS—upgrade to DALI v2.0 and Triton r26.02 now.

AWS patches a high-severity (8.7) Firecracker flaw allowing root guests to trigger memory corruption via the virtio-pci transport. Update your microVMs now.
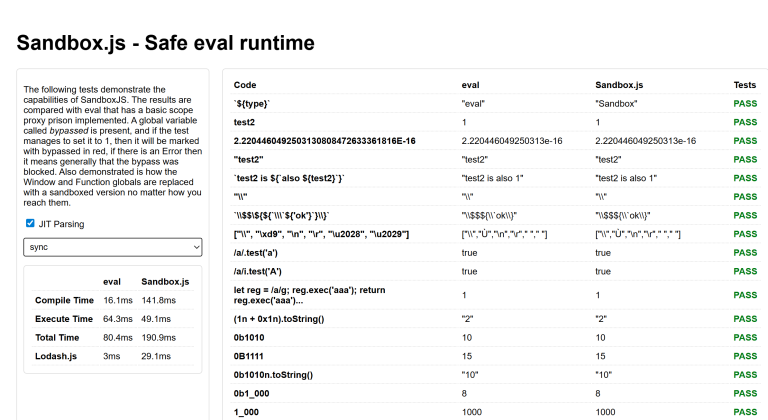
CVE-2026-34208: A critical 10.0 flaw in SandboxJS allows code to escape and poison host objects like Math.random. Secure your environment—update immediately!