
 Do Son
Apache ActiveMQ patches a critical 2026 RCE flaw. Learn how CVE-2026-34197 uses Jolokia and Spring XML to hijack the JVM. Update to 5.19.5 or 6.2.3 now!
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

Weaver E-cology 10.0 faces a critical 9.3 CVSS RCE (CVE-2026-22679). Unauthenticated attackers can hijack servers via a debug endpoint. Patch immediately!

Shadowserver warns of active exploitation of CVE-2021-4473 in Tianxin systems. This 9.3 CVSS flaw allows unauthenticated RCE. Patch your firmware immediately!

A critical Adobe Reader zero-day allows attackers to steal local files and achieve system control via malicious PDFs. Learn how the unpatched exploit works.

IBM patches critical flaws in Verify Identity Access, including a 9.3 CVSS root escalation and 8.1 auth bypass. Secure your identity gateway—update now!

OpenSSL's April 2026 advisory reveals 7 flaws, including a moderate RSA memory leak (CVE-2026-31790). Learn if your version is affected and how to patch.
Critical 9.6 CVSS flaws in Budibase allow unauthenticated RCE and data exfiltration via SSRF. Secure your internal tools—update to v3.33.4 now.

CVE-2026-34612: A critical 10.0 flaw in Kestra allows RCE via SQL injection in label searches. Protect your orchestration server—update to v1.3.7 now!

A critical 9.8 CVSS flaw in Convoy (CVE-2026-33746) allows unauthenticated admin access via forged JWTs. Update to v4.5.1 immediately to secure your KVM.

Electron patches 5 flaws (CVSS 7.0-8.4) allowing sandbox escapes and context isolation bypass. Update to v41, 40, or 39 to secure your desktop app now.

BlueHammer is a functional 0-day exploit targeting Windows Defender’s update engine to achieve SYSTEM privileges. Here is how the unpatched LPE works.

GPUBreach: A new GPU Rowhammer attack from UofT that bypasses IOMMU and ECC to achieve full system root on NVIDIA systems. GitHub code arrives April 13.
Google’s April 2026 Android bulletin fixes a critical zero-interaction DoS in the Framework and high-severity StrongBox HSM flaws. Update your device now.
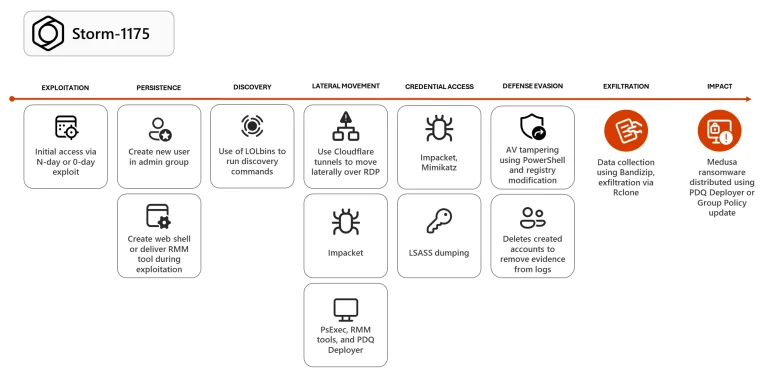
Microsoft exposes Storm-1175: a high-speed threat actor deploying Medusa ransomware in under 24 hours via zero-day exploits. Learn how to stop the blitz.

A critical 9.8 CVSS flaw in Ninja Forms - File Upload plugin allows unauthenticated RCE. 50,000+ WordPress sites are at risk. Update to v3.3.27 now!

Keycloak 26.5.7 fixes an MFA bypass that could let attackers skip two-factor checks. Upgrade your identity server to close the gap.

CVE-2026-34838: A critical 10.0 flaw in GroupOffice allows authenticated users to trigger RCE via insecure deserialization. Update to v26.0.12 immediately!
CERT@VDE warns of critical RCE and SQLi flaws in MB Connect Line's mbCONNECT24 (up to v2.19.4). Unauthenticated attackers can gain full system control. Patch now!

CVE-2026-34950: A critical 9.1 CVSS flaw in fast-jwt allows authentication bypass via leading whitespace. Learn how a regex error leads to algorithm confusion.

Unit 42 reveals how GCP Vertex AI agents can become "double agents," exfiltrating data and accessing Google’s internal code. Learn why BYOSA is essential.

Google’s 2025 VRP hit an all-time high with $17.1M in payouts. Discover how the new AI VRP and elite bugSWAT events are shaping the future of security.

Dgraph patches a critical 10.0 CVSS flaw (CVE-2026-33976). Unauthenticated attackers can overwrite databases and read local files. Update to v25.3.1 now!