
 Do Son
Synology patches critical DSM flaws (CVSS 8.0) allowing file manipulation and data leaks. Secure your NAS—upgrade to DSM 7.3, 7.2.2, or 7.2.1 immediately!
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

A critical 9.1 CVSS flaw in OAuth2 Proxy allows unauthenticated users to bypass security via User-Agent spoofing. Secure your upstream apps—patch v7.15.2 today.
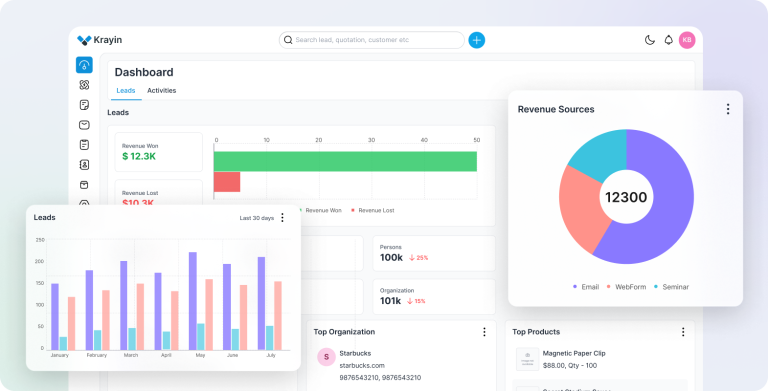
Krayin CRM faces a critical CVSS 10 RCE flaw in its TinyMCE upload endpoint. Authenticated users can seize server control. Patch version 2.2.x immediately!
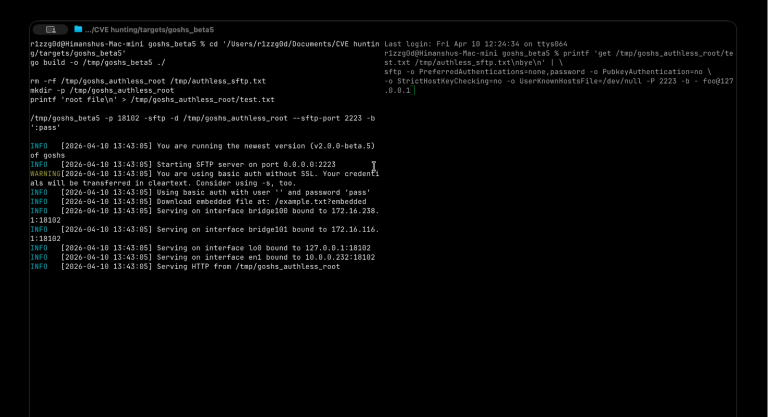
Critical 9.8 flaw in goshs (CVE-2026-40884) allows unauthenticated SFTP access when using specific auth syntax. Secure your files—upgrade to v2.0.0-beta.6 now!

Faced with a massive surge in CVEs, NIST has overhauled the NVD. Starting April 2026, only high-risk flaws get full analysis. Check the new triage rules.
Cisco alerts on a critical 9.9 CVSS flaw in ISE. Even "Read-Only" admins can escalate to root and trigger a total network lockout. Patch immediately.
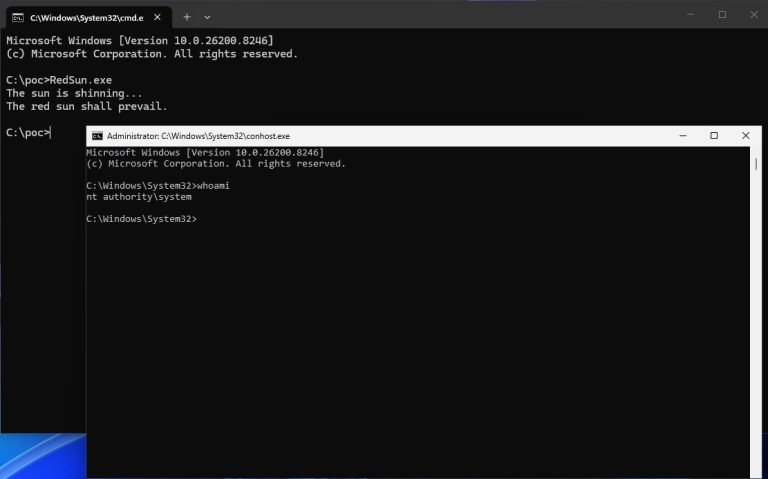
Windows Defender "RedSun" zero-day revealed! This unpatched EoP flaw turns antivirus into a delivery tool for malicious payloads. PoC is public—patch now!
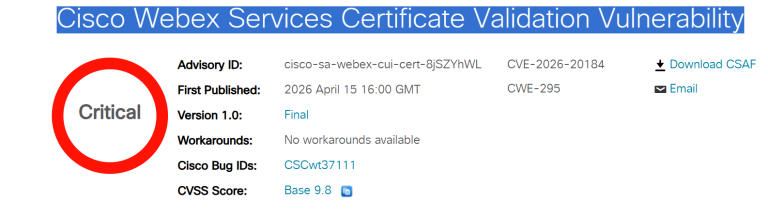
Cisco Webex CVE-2026-20184 allows unauthenticated user impersonation via SSO flaw. Fix requires a manual certificate update in Control Hub. Act now!

Splunk fixes CVE-2026-20204, a critical RCE flaw where low-privilege users can hijack servers via temp files. Patch Enterprise and Cloud instances now!
Google patches 31 Chrome flaws, including a $90K graphics engine bug. Update to version 147.0.7727.101 now to block critical sandbox escapes and RCE risks.
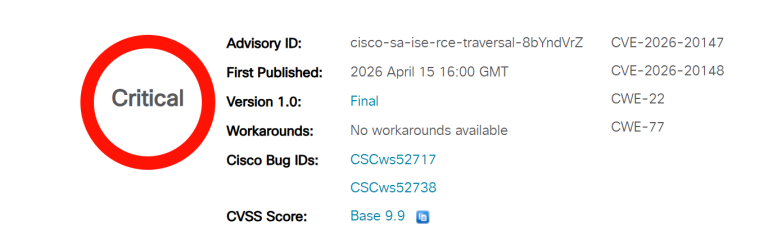
Cisco warns of a critical 9.1 RCE flaw in Identity Services Engine (ISE). Attackers can escalate to root access—apply official security patches now!
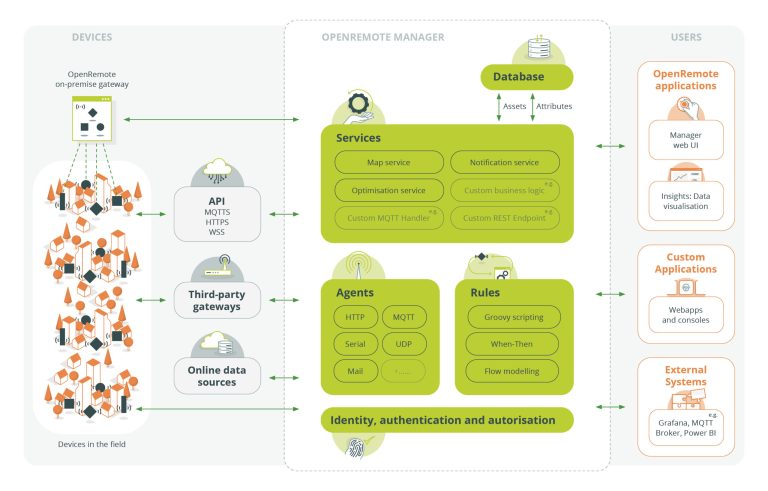
OpenRemote CVE-2026-39842 is a critical CVSS 10 flaw allowing RCE via JavaScript and Groovy injection. Secure your IoT assets—upgrade to v1.22.0 now!
Vendure Core faces a critical 9.1 SQL Injection via the Shop API. Unauthenticated attackers can hijack databases—upgrade to 3.6.2, 3.5.7, or 2.3.4 now!
AVideo’s YPTSocket plugin faces a critical CVSS 10 vulnerability. Unauthenticated attackers can hijack every active session at once. No patch is available.

MinIO faces a critical 8.8 CVSS vulnerability allowing unauthenticated object writes by bypassing signature checks. Secure your AI/ML data—upgrade now!
Adobe patches critical RCE and security bypass flaws in ColdFusion 2023 & 2025. Protect your enterprise servers from takeover—update to the latest version now.

Fortinet issues a critical 9.1 CVSS alert for FortiSandbox. Unauthenticated auth bypass and command injection risks. Patch to 5.0.6 or 4.4.9 immediately.
CISA adds Microsoft SharePoint spoofing (CVE-2026-32201) and legacy Office RCE (CVE-2009-0238) to its KEV Catalog. Remediation deadline: April 28, 2026.

Fastify (25M+ downloads) reveals CVE-2026-33806. A public PoC exploit shows how a single space bypasses schema validation. Upgrade to v5.8.5 now to stay safe.

OpenStack Keystone vulnerability allows disabled LDAP users to authenticate. Logic flaw in attribute mapping affects releases up to 2026.1. Patch now!
Urgent Patch Alert: SharePoint Spoofing Under Active Attack as Microsoft Releases April 2026 Updates

Urgent Patch Alert: SharePoint Spoofing Under Active Attack as Microsoft Releases April 2026 Updates
Microsoft’s April 2026 Patch Tuesday fixes 163 flaws, including an exploited SharePoint spoofing bug (CVE-2026-32201). Patch by April 28 per CISA mandate.
Orthanc v1.12.11 patches 9 critical flaws, including RCE risks and "decompression bombs" in DICOM servers. Secure your healthcare data—upgrade now!