
 Do Son
Cisco warns of active exploitation for CVE-2026-20133 in Catalyst SD-WAN Manager. Unauthenticated attackers can leak OS data. Patch by April 24, 2026.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

The critical "Pack2TheRoot" flaw (CVE-2026-41651) in PackageKit gives root access on Linux. It went undetected for 12 years. Update to version 1.3.5 now!
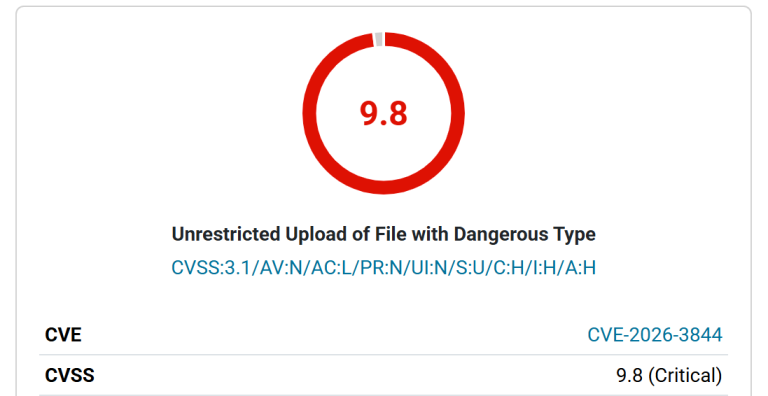
Critical 9.8 CVSS RCE hits 400,000+ WordPress sites using the Breeze plugin. Attackers are exploiting arbitrary file uploads. Update to v2.4.5 immediately!
CVE-2026-33626: A critical SSRF in LMDeploy exploited in under 13 hours. Learn how attackers hijack AI nodes and how to secure your inference cloud now.

CISA adds BlueHammer (CVE-2026-33825) to the KEV catalog. This Microsoft Defender LPE exploit uses TOCTOU to hijack SAM databases. Patch by May 6, 2026.
ElectricSQL reveals a critical 10.0 CVSS SQL injection (CVE-2026-40906). Attackers can hijack PostgreSQL and bypass tenant isolation. Patch to v1.5.0 now.

PHPUnit CVE-2026-41570 allows RCE via invisible newline injection in CI/CD pipelines. Secure your build servers—update to 12.5.22 or 13.1.6 today.

NVIDIA patches critical flaws in KAI Scheduler and CUDA-Q. CVE-2026-24189 and CVE-2026-24177 risk data leaks and DoS. Secure your GPU workloads—update today!

GitLab fixes high-severity GraphQL CSRF and Web IDE vulnerabilities in versions 18.11.1, 18.10.4, and 18.9.6. Protect your sessions and projects—patch now!
Critical 10.0 CVSS flaw in Firebird Database allows RCE via path traversal in the engine loader. Attackers gain root/SYSTEM privileges. Patch to 5.0.4+ now.

Mozilla used Anthropic’s Claude Mythos to fix 271 Firefox vulnerabilities. Discover how AI is finally flipping the script on the cybersecurity "cost asymmetry."

Akamai SIRT warns of a new Mirai campaign weaponizing EOL D-Link routers via CVE-2025-29635. Protect your network from zombie botnets—retire old hardware now.

CrowdStrike reveals a critical 9.8 CVSS flaw in LogScale Self-Hosted. Unauthenticated attackers can read arbitrary server files. Patch to v1.235.1+ now!

Atlassian Bamboo Data Center hit by critical 9.4 RCE (CVE-2026-21571). Attackers can hijack your build pipeline. Secure your supply chain—patch now!
Microsoft's OOB update for .NET 10 (CVE-2026-40372) hits Linux/macOS users. Authentication is at risk. Stop the bypass and rotate your keys today.

Spring Security reveals 7 flaws, including a critical 9.6 CVSS vulnerability in version 7.0. From auth bypass to X.509 impersonation, upgrade to 7.0.5 now.

glibc version 2.43 and older face heap overflows and memory leaks. Learn about CVE-2026-5358, CVE-2026-5450, and CVE-2026-5928. Update your Linux systems now.

Two critical CVSS 10.0 RCE flaws in Spinnaker's Clouddriver and Echo services allow full JVM and shell access. Patch your multi-cloud pipelines immediately.

SGLang faces a critical 9.8 CVSS RCE flaw (CVE-2026-5760). Malicious GGUF models can hijack AI servers via unsandboxed Jinja2 templates. Learn how to fix it.

Progress Software warns of 5 critical MOVEit WAF & ADC flaws. RCE and WAF bypass risks allow total system hijack. Upgrade to v7.2.63.0 now to stay secure.

OVN reveals two critical heap over-read flaws in ICMP and DHCPv6 processing. Learn how crafted packets can siphon sensitive memory and find the patch versions.

CISA adds 8 vulnerabilities to the KEV Catalog, including Cisco, PaperCut, and Zimbra flaws. Actively exploited threats require immediate patching.