
 Do Son
CISA warns "Copy Fail" (CVE-2026-31431) is exploited in the wild. Millions of Linux systems since 2017 are vulnerable to instant root privilege takeover.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
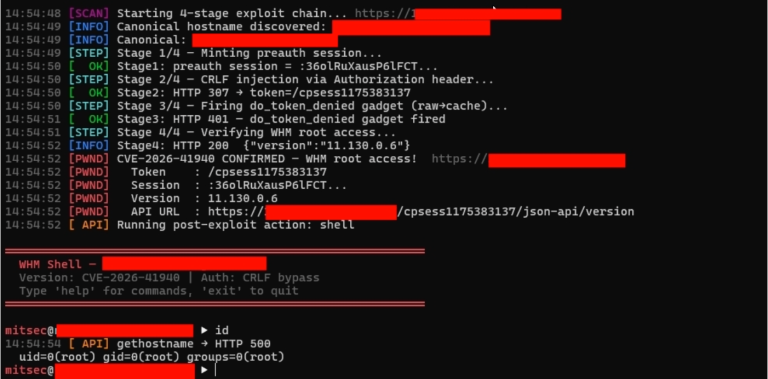
CISA warns of cPanel CVE-2026-41940 (CVSS 9.8). 44,000 IPs compromised via authentication bypass, fueling ransomware and botnets. Patch by May 3rd!

libmodsecurity3 faces critical 8.2 & 7.5 CVSS flaws. A simple one-line script can crash WAF worker processes. Protect your server by upgrading to v3.0.15 now.

CoreDNS 1.14.3 addresses 5 critical flaws in DoH, DoQ, and gRPC. Fix authentication bypasses and DoS risks by upgrading your DNS infrastructure today.

Wazuh patches a critical 9.0 CVSS flaw (CVE-2026-30893) in cluster sync. Malicious peers can achieve RCE and lateral movement. Upgrade your clusters now.

NVIDIA patches a critical 8.6 CVSS flaw in NemoClaw. Prompt injection could leak sensitive host secrets. Upgrade to v0.0.18 to secure your AI agent sandboxes.

Jenkins patches high-severity RCE in Credentials Binding and XSS in GitHub/HTML Publisher plugins. Secure your CI/CD pipeline by upgrading today.

SonicWall discloses critical SonicOS flaws (CVE-2026-0204) hitting Gen6 to Gen8 hardware. Apply the 2026 firmware patch now to prevent unauthorized access.

Critical Root RCE (CVE-2026-6644) hits ASUSTOR ADM. With PoC code now public, 19,000 NAS devices are at risk. Update to ADM 5.1.3.RGO1 immediately.

Linux "Copy Fail" (CVE-2026-31431) technical details and PoC are now public. Learn how a 732-byte script grants root access by corrupting the page cache.

glibc warns of critical flaws (CVE-2026-5435 & CVE-2026-6238) in deprecated DNS functions. Patch legacy apps to avoid buffer overflows and memory leaks.
Jakob Wolffhechel reveals "Shittrix," 89 critical flaws in Citrix XenServer & XCP-ng. CVSS 9.9 bugs allow full host takeover. Assume compromise today.
Critical 9.2 CVSS flaw in WattBox 800/820 controllers (CVE-2026-41446) allows root RCE using plaintext hardware labels. Upgrade to firmware v2.10.0.0 now.

NVIDIA issued an urgent patch for a critical 9.8 CVSS flaw in the FLARE SDK. Stop unauthenticated RCE and data tampering. Upgrade to v2.7.2 immediately.
CISA warns as North Korean and Russian hackers weaponize ConnectWise and Windows Shell flaws. Patch by May 12, 2026, to prevent state-sponsored espionage.
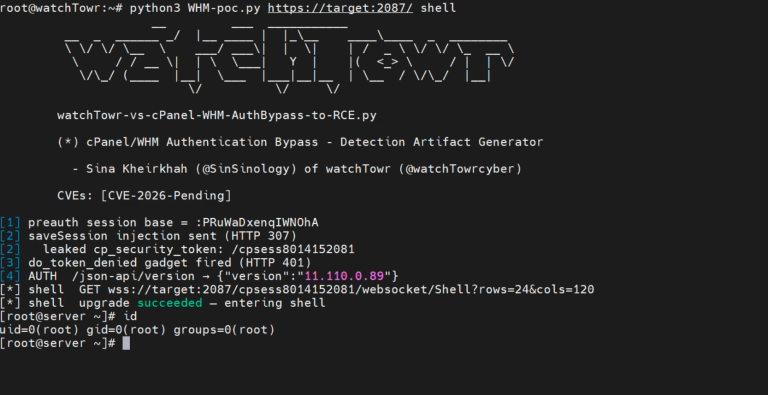
cPanel issues emergency patches for a critical authentication vulnerability affecting all supported versions. Run /scripts/upcp --force immediately to patch.

Google Chrome version 147 is here with 30 vital security fixes. High-severity Use After Free bugs and V8 flaws are patched. Update your browser today.

Wiz Research reveals CVE-2026-3854, a critical GitHub RCE. One git push could expose millions of repos. GHES users must patch to v3.19.3 immediately.
Langflow patches a critical 9.6 CVSS path traversal vulnerability (CVE-2026-42048). Learn how an unsafe bulk delete function put entire filesystems at risk.

Apache Thrift fixes critical cross-language vulnerabilities (MitM, memory corruption, DoS). Secure your Java, Go, and C++ stacks by upgrading to version 0.23.0.

Critical 9.0 CVSS RCE in Nginx UI (CVE-2026-42238) exploits a 10-minute unauthenticated window. Attackers can seize root control. Patch to the latest version now.

Critical RCE flaws hit Apache Camel via header injection and unsafe deserialization. Secure your integrations and upgrade to version 4.20.0 today.