
 Do Son
Microsoft’s May 2026 update fixes 137 vulnerabilities, including 30 Critical RCE and EoP flaws. Prioritize patches for Netlogon, Office, and M365 Copilot now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Critical Alert: CVE-2026-43898 (CVSS 10) in SandboxJS allows a total sandbox escape and RCE. Update to version 0.9.6 immediately to secure your host.
Sysdig warns: PraisonAI (CVE-2026-44338) exploited in under 4 hours. Attackers bypassed auth to hijack agents and drain API quotas. Update to 4.6.34 now!
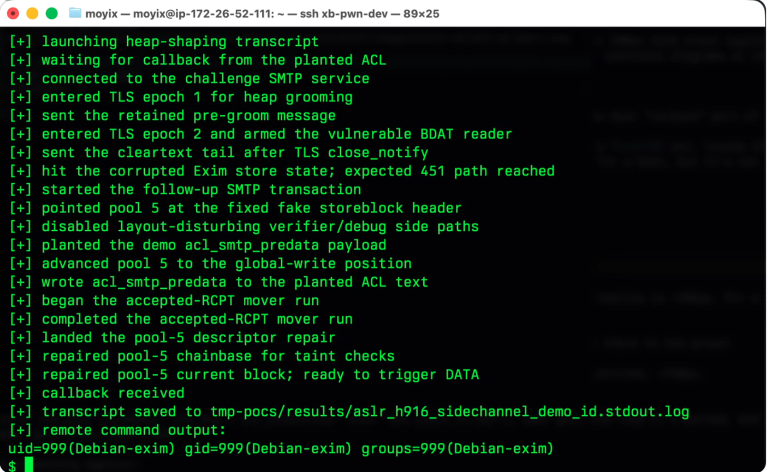
Urgent: Exim fixes a 9.8 severity RCE (CVE-2026-45185) affecting GnuTLS builds. A single-byte heap corruption allows for server takeover. Update to 4.99.3 now!

Urgent: Fortinet warns of 9.1 severity flaws in FortiSandbox (CVE-2026-26083) and FortiAuthenticator (CVE-2026-44277). Patch now to prevent unauthorized RCE.

Urgent: dnsmasq patches 6 critical flaws (CVE-2026-2291+) enabling DNS poisoning and root access. Update your router firmware to version 2.92rel2 now!
Urgent: Casdoor IAM platform hit by critical file write flaw (CVE-2026-44213). Attackers can bypass sandboxes to overwrite databases and gain host access.

Urgent: Siemens patches a 9.3 severity Path Traversal (CVE-2026-41551) in ROS#. Attackers can read/write arbitrary files on robotics systems. Update to V2.2.2!
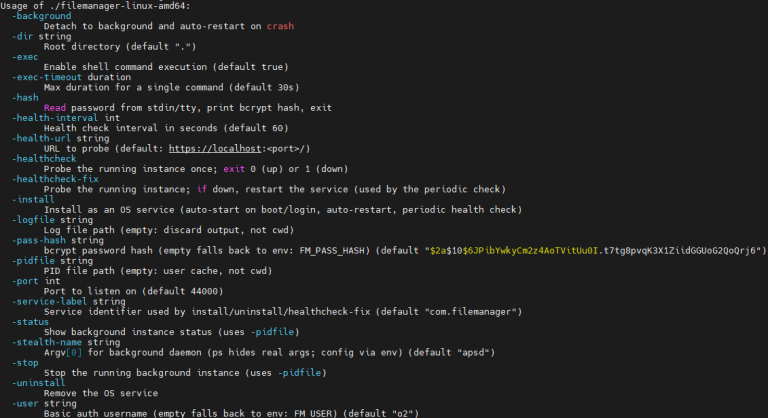
Urgent: cPanel & WHM hit by global 9.8 CVSS auth bypass. Over 2,000 IPs are actively hijacking servers for data theft and ransomware. Patch immediately!

Urgent: Dell patches a 9.8 severity credential flaw (CVE-2026-40636) in ECS and ObjectScale. Secure your enterprise storage by upgrading to version 4.3.0.0.

SAP’s May 2026 Patch Day fixes two 9.6 severity flaws in S/4HANA and Commerce Cloud. Prevent SQL injection and RCE by updating your SAP landscape today.
Urgent: PrestaShop patches a 9.3 severity XSS flaw (CVE-2026-44212) that allows unauthenticated attackers to hijack your store's back office. Update now!
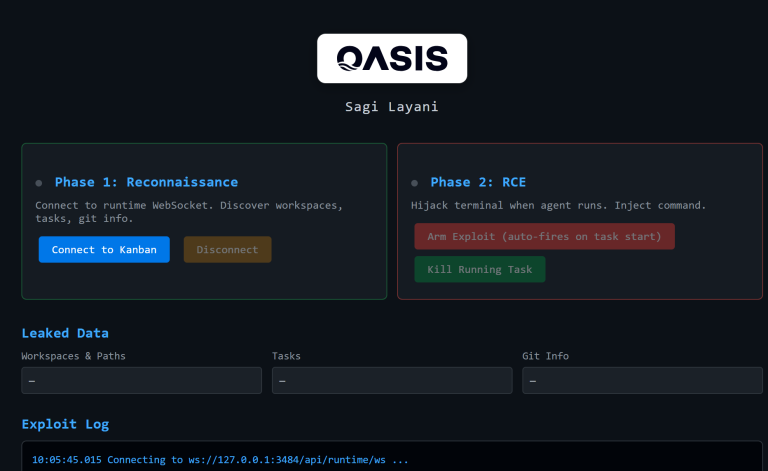
Critical Alert: CVE-2026-44211 (CVSS 9.6) in Cline AI allows malicious sites to hijack your terminal and steal data via WebSockets. Update your CLI tools now.
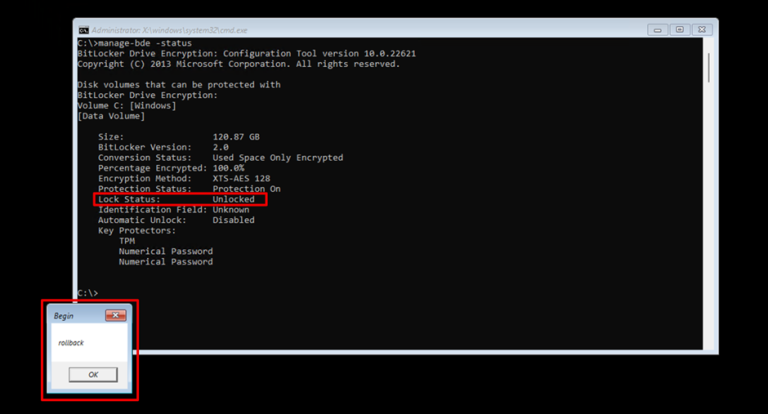
Public PoC Alert: The BitUnlocker Downgrade Attack bypasses BitLocker on patched Windows 11 machines in under 5 minutes. Learn how to secure your TPM with a PIN.
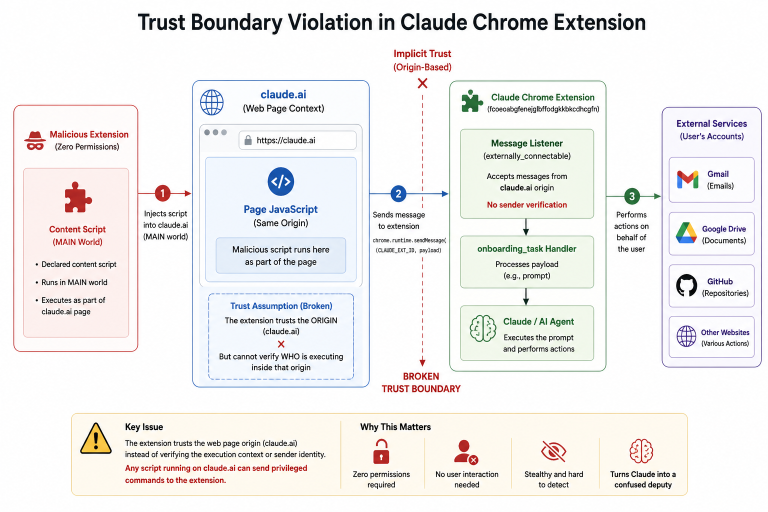
LayerX uncovers a critical flaw in Anthropic’s Claude extension. Learn how attackers can hijack AI agents to steal data and bypass security policies.
PHP releases urgent security patches for a 9.5 severity RCE in the SOAP extension and a PHP-FPM XSS flaw. Update to 8.2.31, 8.3.31, 8.4.21, or 8.5.6 now!

Urgent: Apache CloudStack patches critical flaws (CVE-2026-25199, CVE-2026-25077) enabling VM hijacking and KVM host RCE. Secure your cloud environment now.

Update cPanel immediately! High-severity vulnerabilities (CVSS 8.8) allow Perl injection and privilege escalation. Protect your hosting environment now.

Kaspersky reports a record surge in CVEs for Q1 2026. Discover how AI-driven exploits, authentication bypasses, and new C2 trends are reshaping cyber defense.
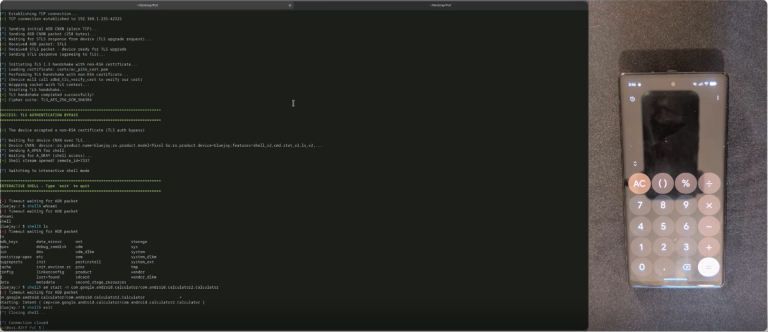
BARGHEST reveals CVE-2026-0073: a zero-click Android ADB bypass over Wi-Fi. Public PoC and exploit details are now live. Secure your mobile device today!
Protect your AI apps. Spring AI issues urgent patches for three critical vulnerabilities causing data destruction, memory poisoning, and user data leaks.

Protect your Grav CMS deployments. Attackers are chaining CVE-2026-42613 and CVE-2026-42607 to achieve unauthenticated remote code execution. Patch today!