
 Do Son
Cisco Catalyst SD-WAN CVE-2026-20182 (CVSS 10) exploited in the wild. Attackers bypassing auth to seize admin control. Upgrade your network fabric now!
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

NGINX 1.30.1 fixes a 9.2 CVSS RCE flaw (CVE-2026-42945) and five other critical vulnerabilities. Protect your web infrastructure and update immediately!

Palo Alto Networks patches CVE-2026-0263 and CVE-2026-0265. Fixes for IKEv2 RCE and CAS bypass are now available. Update your PAN-OS firewalls immediately!

CVE-2026-32661 exploited in the wild. A 9.8 CVSS flaw in GUARDIANWALL MailSuite allows unauthenticated RCE. Apply Canon's official patches immediately.

200,000+ sites hit by CVE-2026-8181. A 9.8 CVSS Burst Statistics flaw allows RCE via auth bypass. 5,000+ attacks blocked. Update to 3.4.2 immediately!
Urgent: AMD Zen 2 processors (Ryzen/EPYC) hit by CVE-2025-54518. Hardware flaw allows instruction corruption and privilege escalation. Update your BIOS now!

GitLab patches high-severity XSS (8.7 CVSS) and unauthenticated DoS flaws in versions 18.11.3, 18.10.6, and 18.9.7. Secure your DevOps pipeline now!

Ivanti issues an urgent patch for CVE-2026-8043, a critical 9.6 CVSS flaw in Xtraction allowing attackers to read files and write malicious HTML. Update now!

Urgent: A memory corruption flaw in MongoDB time-series collections (CVE-2026-8053) enables server takeover. Patch to versions 8.3.2, 8.0.23, or 7.0.34 now.

Urgent: Public PoC for OPNsense CVE-2026-44194 and CVE-2026-45158. Critical flaws allow root command execution via DHCP and User sync. Update to 26.1.8 now!

Composer CVE-2026-45793 leaks GitHub tokens into CI/CD logs due to a validation error. Update to version 2.9.8 now and audit your GitHub Action logs.

Public PoC for NGINX CVE-2026-42945. An 18-year-old RCE flaw in the rewrite module enables server takeover. Update to NGINX 1.31.0 or 1.30.1 immediately.

Public PoC for Fragnesia. This universal Linux LPE exploit allows unprivileged users to seize root via the page cache. Patch your kernel immediately!
Urgent: Public PoC exploit code released for YellowKey (BitLocker bypass) and GreenPlasma (SYSTEM elevation). Windows 11 and Server 2025 are at high risk.

Critical Siemens Alert: 9.3 severity XSS flaws hit SIMATIC S7 PLCs. Attackers can hijack sessions via web interfaces. Update to V3.1.6 or follow mitigations.
Critical Alert: CVE-2026-25244 (CVSS 9.8) in WebdriverIO allows RCE via unsanitized git branch names. Secure your CI/CD pipeline and update to 9.24.0 now.

Microsoft’s May 2026 update fixes 137 vulnerabilities, including 30 Critical RCE and EoP flaws. Prioritize patches for Netlogon, Office, and M365 Copilot now.
Critical Alert: CVE-2026-43898 (CVSS 10) in SandboxJS allows a total sandbox escape and RCE. Update to version 0.9.6 immediately to secure your host.
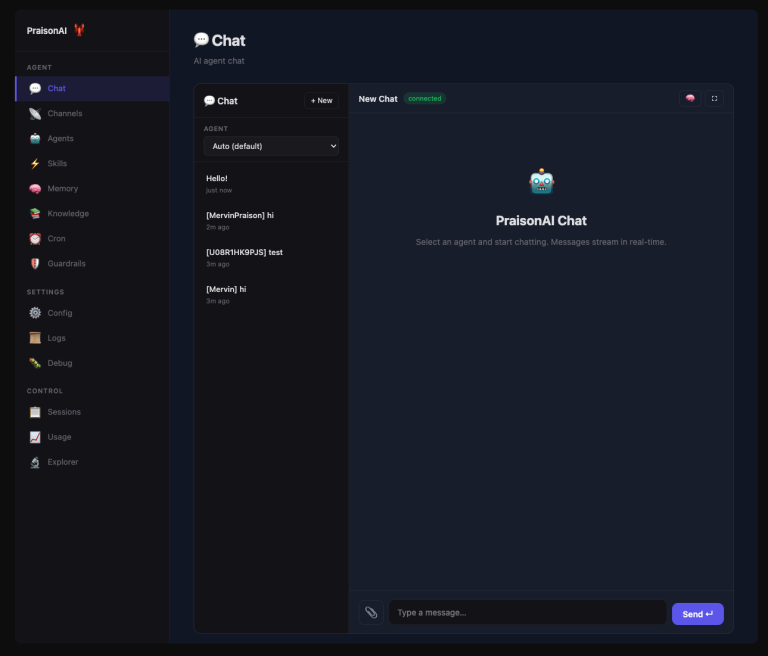
Sysdig warns: PraisonAI (CVE-2026-44338) exploited in under 4 hours. Attackers bypassed auth to hijack agents and drain API quotas. Update to 4.6.34 now!
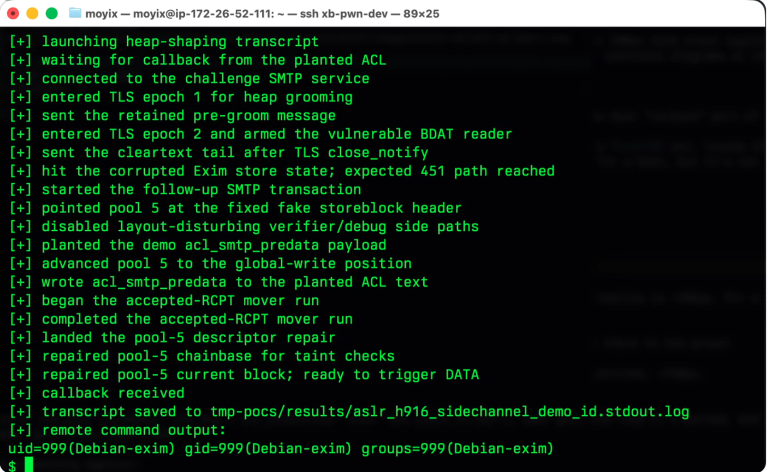
Urgent: Exim fixes a 9.8 severity RCE (CVE-2026-45185) affecting GnuTLS builds. A single-byte heap corruption allows for server takeover. Update to 4.99.3 now!

Urgent: Fortinet warns of 9.1 severity flaws in FortiSandbox (CVE-2026-26083) and FortiAuthenticator (CVE-2026-44277). Patch now to prevent unauthorized RCE.

Urgent: dnsmasq patches 6 critical flaws (CVE-2026-2291+) enabling DNS poisoning and root access. Update your router firmware to version 2.92rel2 now!