
 Do Son
Critical Casdoor authentication bypass flaws allow cross organization privilege escalation. Learn how to secure your identity infrastructure today.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

Google patches a critical Android zero day flaw in the June 2026 security bulletin. Learn how to secure your device from active exploitation now.

Multiple critical Rancher security flaws allow widespread cluster privilege escalation. Patch your Kubernetes container environments immediately.

A critical TP-Link router vulnerability affects Archer models. Download the latest CVE-2026-5509 patch immediately to secure your network environment.

Esri released a critical ArcGIS Server security patch addressing a severe directory traversal vulnerability. Protect your enterprise data and apply it now.
A critical Cache Warmer RCE flaw allows Magento PHP object injection. Learn how to secure your e-commerce storefront today.

Secure your servers against a major Plesk privilege escalation flaw. Learn how the latest CVE-2026-44962 patch protects Linux infrastructure.

A maximum-severity Liquidjs remote code execution flaw impacts millions. Learn about this template engine vulnerability and update now.

A critical Netlogon RCE vulnerability is actively exploited in the wild. Learn how to secure your Windows domain controllers immediately.
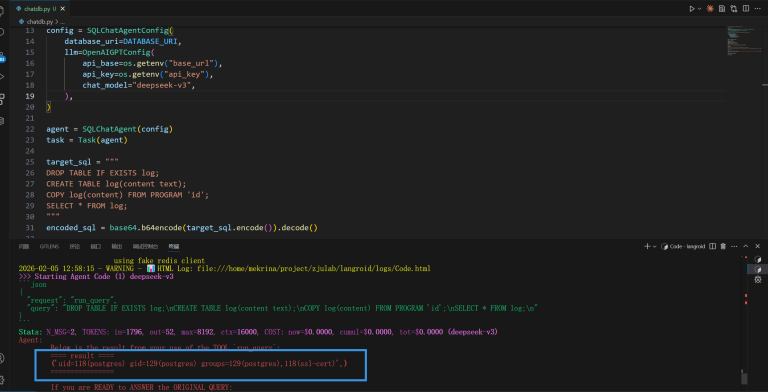
A critical Langroid vulnerability causes RCE via prompt injection. Learn how this LLM security flaw impacts database hosts and how to patch it.

New IBM Aspera vulnerabilities could allow remote code execution and authentication bypass. Update your High-Speed Transfer applications today.

Learn about the new Notepad++ security flaws. Public Notepad++ exploit code triggers arbitrary code execution. Update to version v8.9.6.1 now.

A critical Eppendorf bioreactor security flaw exposes systems via a hard-coded VNC password. Learn how to secure your BioFlo 320 device.

A critical MCP Toolbox vulnerability exposes enterprise databases. Learn how this security flaw allows session hijacking and how to fix it.
A critical Comet Backup RCE vulnerability has been found. Learn about the CVE-2026-32999 patch released to secure backup servers and user data.
A newly fixed Apache Ignite vulnerability allows arbitrary file read attacks via path traversal. Learn how to secure your database immediately.
IBM released a critical WebSphere remote code execution update. Apply the request smuggling patch immediately to protect your server environment.
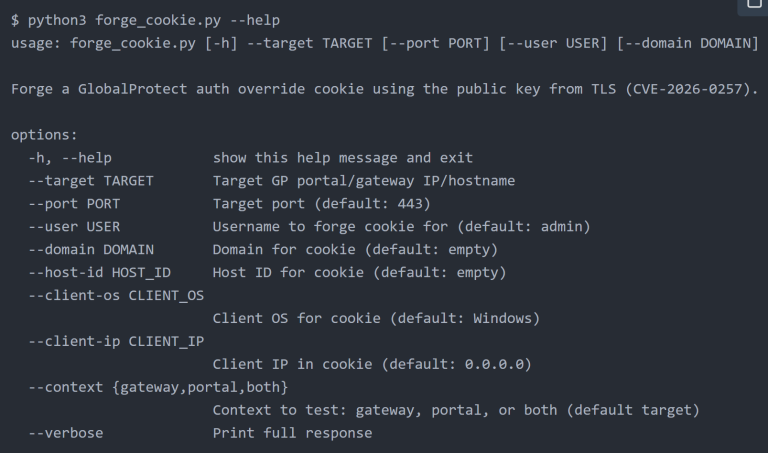
The PAN-OS authentication bypass flaw is actively exploited in the wild. Learn how to secure your GlobalProtect VPN gateways today.
Stay secure with the latest Oracle security patch updates. Learn how these fixes address critical software vulnerabilities across multiple enterprise platforms.
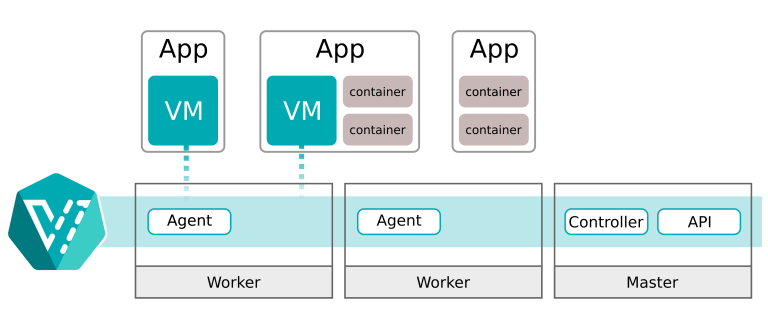
Discover how the critical KubeVirt privilege escalation flaw (CVE-2026-7374) allows container runtime hijacking and creates a cluster takeover risk.

The Samba Team dropped fixes for critical Samba vulnerabilities. Read about the remote code execution flaws carrying perfect 10.0 CVSS scores.

Discover the latest Jenkins plugin security flaws. Learn how unvalidated LDAP referrals and arbitrary file reads impact your controller servers.