 Do Son
Fix the critical SystemLink authentication bypass today. This severe privilege escalation bug allows unauthenticated attackers to steal enterprise dashboard data.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
A critical Cisco Unified CM vulnerability is exposed. This public PoC code disclosure highlights a severe SSRF risk in WebDialer.

A critical Everest Forms Pro flaw faces active WordPress exploitation. Update immediately to prevent unauthorized remote code execution attacks.

New Axios proxy vulnerabilities expose apps. A critical prototype pollution gadget allows full traffic interception. Secure patches are now available.

The newly uncovered SymJack AI attack technique highlights critical gaps in AI coding agent security. Learn how symlink hijacks exploit developers.
Acer router security flaws expose cleartext credentials. Learn how these critical firmware bugs threaten home networks and how to update.

An urgent NVIDIA NVTabular vulnerability patch fixes high-severity bugs. Secure your systems against this untrusted deserialization flaw.
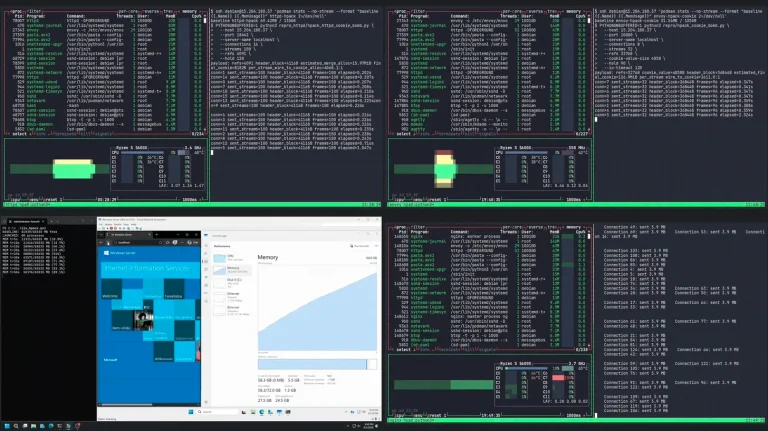
Researchers disclosed a public PoC for an HTTP/2 'bomb' that exhausts server resources and causes denial of service. Mitigation steps inside.

A high-severity Apache Solr default credentials vulnerability is exposed. Learn the critical CVE-2026-44825 workaround to secure your clusters.

A critical GitHub token stealing bug targets github.dev web spaces. Learn how it exploits the VSCode webview security model to hijack private repositories.
Severe InHand router flaws expose industrial networks to command injection vulnerabilities. Update your industrial firmware immediately to patch these bugs.

CISA added new actively exploited vulnerabilities to its catalog. Learn how the Android privilege escalation flaw impacts corporate environments.

A critical USR-W610 vulnerability exposes hardcoded administrative credentials. Learn how to secure your PUSR IoT converters from exploitation.

A critical Langflow RCE vulnerability impacts the Shareable Playground feature. Learn about the new security patches available.

A severe Laravel CRLF injection vulnerability exposes web apps to mail relay abuse. Apply the latest CVE-2026-48019 patch to protect your infrastructure.

Critical XCharge C6 vulnerabilities expose EV chargers to exploitation. Learn how recent updates address these EV charger security flaws immediately.

An active Kirki plugin vulnerability allows a critical WordPress account takeover. Learn how this 9.8 CVSS flaw impacts 150,000 active websites.

A high-severity Ivanti ITSM vulnerability is fixed. Learn how to address this authenticated privilege escalation flaw on cloud and on-premises setups.

A critical Apache Fesod SSRF vulnerability has been found. Learn about the CVE-2026-49328 patch released to protect internal network resources.

A critical KMW CCTV vulnerability allows an unauthenticated password reset. Secure your surveillance cameras and patch your firmware immediately.

Multiple Fleet security vulnerabilities expose private environments to cross namespace secret disclosure and SSRF attacks. Patch your systems now.