
 Do Son
Chrome security update to version 149 patches 28 flaws, including critical CVE-2026-12007, CVE-2026-12008, and CVE-2026-12010 bugs.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Critical UniFi OS vulnerabilities boast a 9.9 CVSS score. Patch these Ubiquiti security flaws to prevent command injection and secure your network today.

Fix critical AMD security vulnerabilities and hardware security flaws now. Learn about CVE-2025-54509 and CVE-2025-10263 updates.
Fix critical Apache Answer vulnerabilities and security flaws today. Upgrade your platform to stay safe from unauthorized access and server crashes.

A critical 9.8 CVSS HTTP.sys RCE vulnerability (CVE-2026-47291) threatens millions of users. Secure your Windows HTTP stack exploit risks now.

New patches fix critical Spring HATEOAS flaws including CVE-2026-41006 and CVE-2026-41007 to prevent heap exhaustion and bypasses.
Deploy the latest Spring GraphQL security patches to remediate critical unsafe deserialization flaws and cross-site WebSocket hijacking vulnerabilities.
A critical PeopleSoft RCE security bug allows an unauthenticated HTTP exploit to execute code. Learn how to patch CVE-2026-35273 immediately.

A CVSS 9.8 flaw highlights new Splunk Enterprise vulnerabilities. Patch CVE-2026-20253, CVE-2026-20251, and others to prevent remote attacks on your servers.
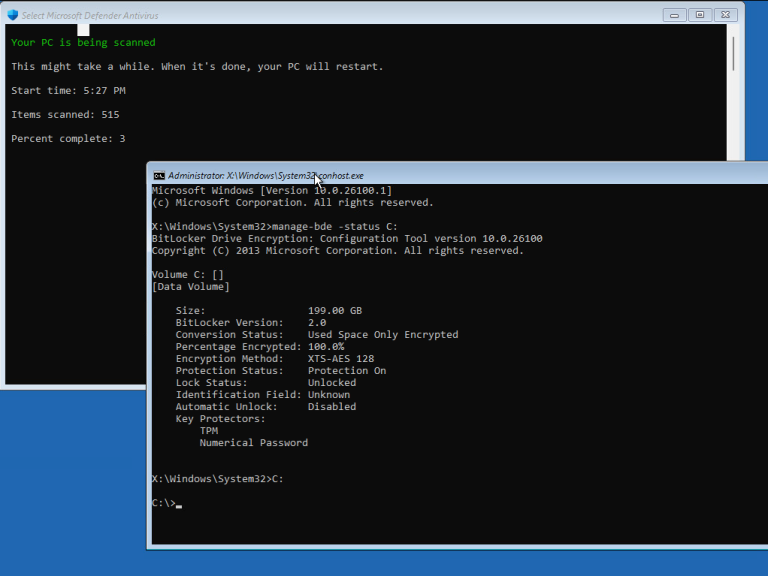
A new GreatXML BitLocker bypass PoC exploit is publicly disclosed. Learn how this Windows Defender vulnerability grants unrestricted volume access.

A new Dahua security advisory warns of critical Dahua product vulnerabilities, including CVE-2026-29116. Update your IPC and SD devices to prevent DoS attacks.
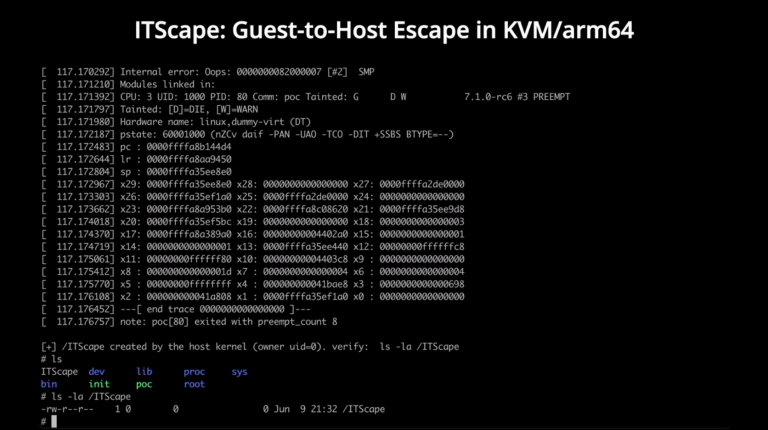
The ITScape KVM escape vulnerability (CVE-2026-46316) threatens arm64 clouds. Details and a guest-to-host escape exploit PoC are now publicly disclosed.

A critical Jenkins security advisory 2026 warns of deserialization and XSS flaws like CVE-2026-53435. Patch your CI/CD pipelines immediately!

Discover the latest GitLab security updates in patch release 19.0.2. Protect your self-managed servers from critical vulnerabilities like CVE-2026-6552.
Severe NVIDIA DALI vulnerabilities allow remote code execution and data tampering. Learn how to secure your systems against the CVE-2026-24180 exploit today.

A critical PhpSpreadsheet RCE vulnerability impacts 312 million users. Learn how the CVE-2026-45034 exploit bypasses patches and triggers code execution.

A new strongSwan CVE-2026-47895 vulnerability allows remote code execution via a libstrongswan double-free exploit. Patch your VPN servers now!

Five new Spring Data vulnerabilities threaten applications with SpEL expression injection and DoS attacks. Upgrade your Spring frameworks immediately!
A critical UpdraftPlus CVE-2026-10795 vulnerability threatens 3 million sites. Hackers are exploiting this UpdraftPlus authentication bypass in the wild.
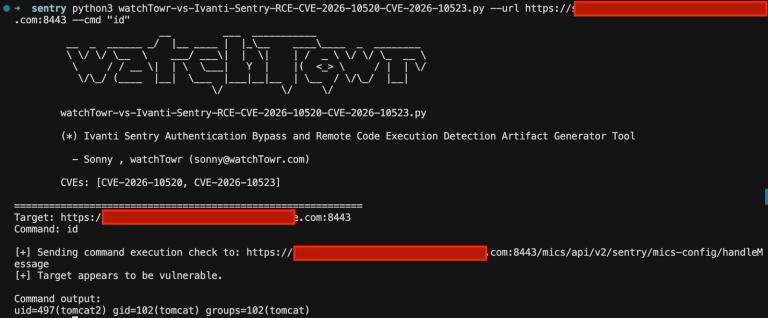
Critical Ivanti Sentry RCE details and a publicly disclosed PoC exploit are out. Patch the CVSS 10 and 9.9 flaws immediately to secure your network.

New OpenSSL security patches address a critical use-after-free bug that introduces an immediate remote code execution risk across enterprise systems.

A new Microsoft Defender zero day exploit leaks online, exposing a severe race condition vulnerability affecting fully patched Windows installations.