
 Do Son
A Cloud Foundry UAA vulnerability (CVE-2026-41005) enables SAML authentication bypass, letting attackers forge trusted assertions. Upgrade now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Three NVIDIA NeMo vulnerabilities (CVE-2026-24155, CVE-2026-24252, CVE-2026-24228) enable code execution. Update NeMo Framework to v2.7.3 now.

A MongoDB Server vulnerability chain, including a use-after-free flaw (CVE-2026-11933), lets attackers crash servers or leak memory. Patch now.
A ShapedPlugin supply chain attack (CVE-2026-10735) injected malware into WordPress Pro plugins. Discover the impact and how to protect your site today.

Three Tornado security vulnerabilities (CVE-2026-49853, CVE-2026-49855, CVE-2026-49854) risk credential leaks and DoS. Update to Tornado 6.5.6 now.
A critical Vitest RCE vulnerability (CVE-2026-53633, CVSS 9.8) has public PoC code. Browser Mode flaw enables config overwrite and remote code execution.
A Haskell TLS vulnerability (CVE-2026-9648) lets attackers bypass X.509 NameConstraints to impersonate domains. Update crypton-x509-validation to 1.9.1.

CISA warns of 7 Naxclow IoT vulnerabilities, including a hard-coded key (CVE-2026-28742) enabling device takeover of doorbells and cameras.

Two pre-auth FreeSWITCH heap buffer overflow bugs (CVE-2026-49841, CVE-2026-49840) hit mod_verto and libesl. Update to v1.11.1 to stay safe.

A critical phpBB authentication bypass (CVE-2026-48611) lets attackers hijack any account on thousands of forums. Update to 3.3.17 now.

CVE-2026-54420, a LiteSpeed cPanel privilege escalation flaw, is exploited in the wild to gain root on shared hosting. Patch to plugin v2.4.8 now.
Cisco warns CVE-2026-20262, a Cisco SD-WAN vulnerability enabling arbitrary file write, is exploited in the wild. Patch SD-WAN Manager now.

A Jenkins RCE vulnerability (CVE-2026-53435) is under active exploitation. Honeypots are seeing attacks now, so patch your Jenkins controller fast.

Two critical FreePBX RCE vulnerabilities in Superfecta and UCP modules expose servers to authenticated arbitrary code execution and command injection.

Public details and PoC exploit code expose a critical Wazuh CVSS 10 vulnerability allowing attackers to smuggle OpenSearch bulk operations.

A patched WinRAR vulnerability in Ukraine is still exploited via CVE-2025-8088 to deploy GIFTEDCROOK and espionage tools, says Trend Micro.

Fixes roll out as vulnerable UEFI shim bootloaders allow attackers to achieve a critical Secure Boot bypass prior to OS initialization.

A critical CodeIgniter vulnerability (CVE-2026-48062, CVSS 9.8) lets attackers bypass upload checks and trigger arbitrary code execution. Update now.
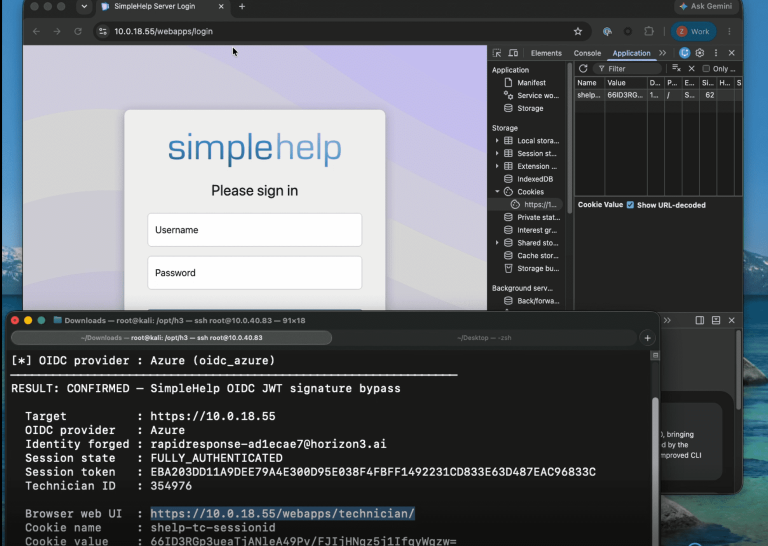
A critical SimpleHelp authentication bypass flaw leaves servers open. Attackers exploit the OIDC authentication flow to gain technician control.

New updates patch critical Squid proxy vulnerabilities. Secure your server against a heap buffer overflow attack and out-of-bounds reads today.

Discover important Apache CXF vulnerabilities, including severe JNDI injection flaws. Patch CVE-2026-50634 and secure your network endpoints today.

New updates patch critical Spring security vulnerabilities, mitigating cross-site scripting and server-side request forgery risks across multiple versions.