
 Do Son
A PAN-OS buffer overflow, CVE-2026-0288, enables arbitrary code execution on Palo Alto firewalls. Patch now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

Google's latest Chrome security update fixes 27 flaws, including two critical use-after-free bugs. Update to 150.0.7871.114 now.

Foxit fixed 28 flaws in Foxit PDF Reader and PDF Editor. Twenty allow arbitrary code execution via crafted PDFs. Update to 2026.1.2 now.

OpenSSH 10.4 ships eight security fixes, including a client use-after-free (CVE-2026-60002) plus SFTP and SCP path bugs. Update now.

A critical Ghost cache poisoning bug lets an unauthenticated x-ghost-preview header hijack staff accounts. Update to Ghost v6.37.0 now.
A Network UPS Tools RCE (CVE-2026-54161) lets a malicious upsd trigger upsmon command injection as root. No patch exists yet, so mitigate now.

New pretix vulnerabilities include a critical session takeover chain (CVE-2026-13602) and an SSRF API key leak. Update to 2026.5.3 now.

APISIX authentication bypass CVE-2026-39999 lets attackers forge JWTs via algorithm confusion. APISIX 3.16.0 is affected; upgrade to 3.16.1.

Nebula reveals a severe Android remote root exploit chain combining a Firefox vulnerability and a 15-year-old Linux kernel flaw.

Censys research finds 70% of WordPress sites run end-of-life PHP. Outdated plugins and defaults leave millions of sites wide open to attack.
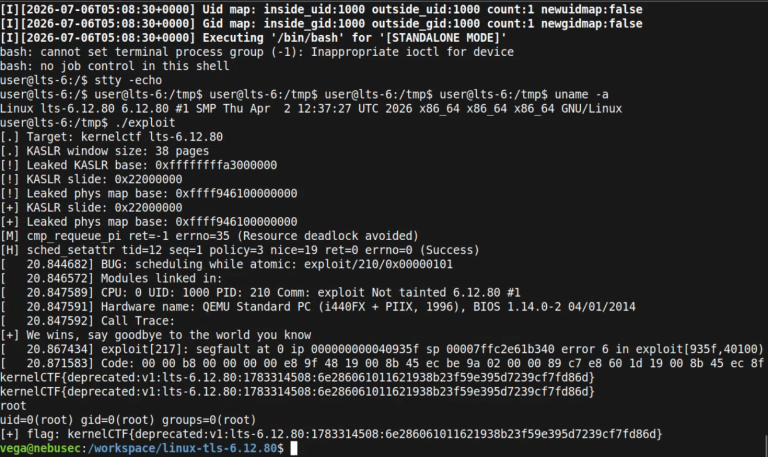
Researchers disclosed GhostLock (CVE-2026-43499) with public PoC code. The 15-year Linux kernel bug enables privilege escalation and container escape.
CISA added four actively exploited flaws to its KEV Catalog, including critical Joomla, Langflow, and ColdFusion bugs. Agencies must patch by July 10.
BMC patches Control-M command injection flaw CVE-2026-10539, an unauthenticated remote command injection bug rated CVSS 9.5.

A SharePoint remote code execution flaw (CVE-2026-33112) is now public with full details and PoC. A low-privilege user can run code. Patch now.
Ubiquiti's UniFi security advisory 066 patches 25 flaws, including a critical command injection (CVE-2026-50746) scoring 10.0. Update your devices now.
A critical IBM Power HMC vulnerability (CVE-2026-12943) allows unauthenticated attackers to execute commands. Patch your systems immediately.

CVE-2026-11405 is a Tenda authentication backdoor. It allows full administrative access without valid credentials. Protect your network with these steps.
BeyondTrust patched two critical pre-authentication vulnerabilities (CVE-2026-40138, CVE-2026-40139, CVE-2026-40140). Update Remote Support instances now.

Researchers disclosed a PoC for the Januscape KVM escape (CVE-2026-53359). This use-after-free KVM bug impacts public clouds, allowing host panics and LPE.

Discover the new Cursor IDE RCE vulnerability called DuneSlide. This critical sandbox escape flaw assigned CVE-2026-50548 threatens developer environments.
A widespread OpenSSL error handling flaw makes apt fail HTTPS in FIPS mode. A stale error queue entry gets misread as fatal. Audit your code.

Two PHP flaws are patched. CVE-2026-12184 is a PHP remote DoS that crashes PHP-FPM, and CVE-2026-14355 causes memory corruption. Update PHP now.