 Do Son
Four critical Coolify vulnerabilities let low-privileged users reach remote code execution and cross-tenant server access. Update to v4.1.2 now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
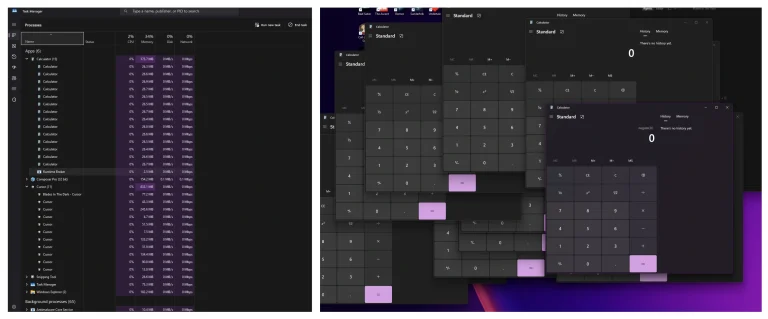
A high-severity Cursor zero day vulnerability allows automatic remote code execution via malicious git.exe files. Read how this flaw remains unpatched.
Rockwell Automation vulnerability CVE-2026-10577 (CVSS 10) exposes an unauthenticated debug port in 1715 Redundant I/O modules. Update to firmware 3.011.
Notepad++ vulnerabilities now have public PoC exploit code. CVE-2026-52886, CVE-2026-54758, and CVE-2026-57233 are fixed in v8.9.7. Update now.
Google's Chrome security update 150.0.7871.124 fixes 15 flaws, including critical use-after-free bugs CVE-2026-15764 and CVE-2026-15765. Update now.
CISA warns SharePoint vulnerabilities CVE-2026-32201, CVE-2026-45659, and CVE-2026-56164 are exploited in the wild. Patch and harden servers now.

SonicWall SMA1000 SSRF flaw CVE-2026-15409 (CVSS 10.0) is exploited in the wild. Upgrade to hotfix 12.4.3-03453 or 12.5.0-02835 now.
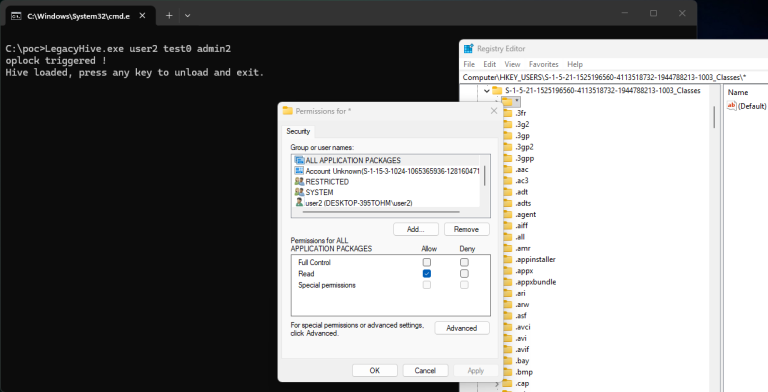
LegacyHive exploit code is public. This unpatched Windows privilege escalation flaw from Nightmare-Eclipse defeats the July 2026 patch.

Microsoft's July 2026 Patch Tuesday fixes 570 flaws. Zero-days CVE-2026-56155 and CVE-2026-56164 are exploited in the wild. Patch now.

Critical Dell vulnerabilities like CVE-2026-53483 allow attackers to take complete control of system. Patch PowerProtect flaws to stop remote exploits.
A Debian webhost was rooted while missing fixes for Bad Epoll (CVE-2026-46242) and an IPv6 frag escape. Public PoC exploit code is now out.

X.Org Server ships fixes for two flaws, including CVE-2026-56000, a CVSS 9.0 use-after-free. Update xorg-server and Xwayland now.
PHP Composer patched three flaws, including CVE-2026-59948, an arbitrary file write that can run code outside your project. Update to 2.10.2 or 2.2.29.
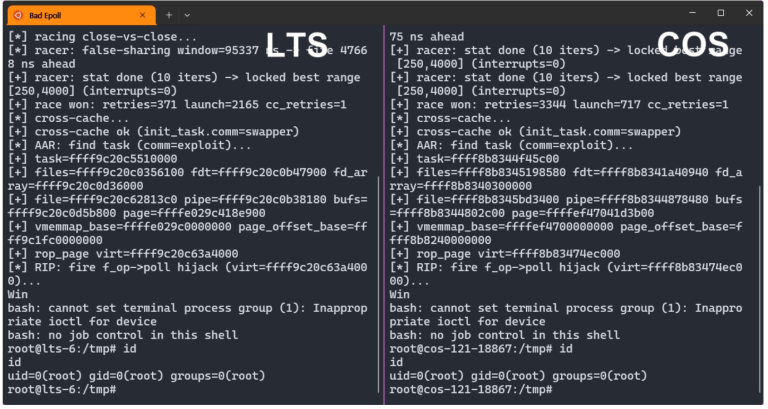
Bad Epoll (CVE-2026-46242) is a Linux kernel UAF enabling root privilege escalation. Full details and PoC exploit code are now public. Patch now.
VMware Avi Load Balancer Authentication Bypass (CVE-2026-47865, CVSS 9.8) Headlines Seven-Flaw Patch

VMware Avi Load Balancer Authentication Bypass (CVE-2026-47865, CVSS 9.8) Headlines Seven-Flaw Patch
VMware Avi Load Balancer patches CVE-2026-47865 (CVSS 9.8), a critical authentication bypass, plus six more flaws. Upgrade the Avi Controller now.

SAP Security Patch Day July 2026 fixes CVE-2026-44747 (CVSS 9.9), a memory corruption flaw in NetWeaver AS ABAP, plus two more critical bugs.

Discover how new prompt injection attacks threaten AI security. Hackers use prompt injection techniques to manipulate AI agents and bypass safety controls.
WinFsp vulnerabilities CVE-2026-3006 and CVE-2026-7162 enable local privilege escalation to SYSTEM on Windows. Update to WinFsp 2026 Beta2 now.
Netwrix Password Secure vulnerabilities (CVSS 9.9) allow authenticated remote code execution on the server. Update to version 26.6.100 now.

CVE-2026-6875 (CVSS 9.5) is a ServiceNow sandbox escape in the AI Platform allowing unauthenticated remote code execution. Patch to fixed releases now.
CVE-2026-53513 is a Better Auth SSRF flaw (CVSS 9.6) in the SSO plugin. It exposes cloud metadata and enables account takeover. Patch to 1.6.11 now.
A critical privilege escalation flaw (CVE-2026-20744) affects Hydro-Québec EV charging stations. Learn how this vulnerability impacts the backend.