
 Do Son
Attackers are exploiting a ServiceNow sandbox escape RCE in the wild. Public proof-of-concept details for CVE-2026-6875 pre-auth code execution are out.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Cloudflare deploys emergency WAF rules to block the critical WordPress wp2shell vulnerability. Update your site now to prevent severe RCE security risks.
Ubuntu Pro Client vulnerability CVE-2026-11386 (CVSS 9.0) lets a spoofed contract server inject APT sources and run code with root privileges.
WordPress pre-auth RCE CVE-2026-63030 chains a REST batch bug with SQL injection. Details and a public PoC are out. Update to WordPress 7.0.2 now.
Kyverno vulnerability CVE-2026-54523 (CVSS 9.6) is public with PoC exploit code. It lets a tenant gain admin in any namespace. Update to v1.18.2.
Citrix patched CVE-2026-53565, a Citrix Secure Access vulnerability letting local users gain SYSTEM, plus the CVE-2026-53566 out-of-bounds read bug.

Chrome security update 150.0.7871.128 patches 7 flaws, including three critical use-after-free bugs in CameraCapture, GPU, and Network. Update now.

TP-Link Kasa vulnerability CVE-2026-9770 (CVSS 8.6) lets local attackers intercept admin credentials on EC70 and EC71 cameras. Update firmware now.
CISA KEV catalog adds three actively exploited flaws: FortiSandbox CVE-2026-25089, CVE-2026-39808, and SharePoint CVE-2026-58644. Patch by July 19.
7-Zip vulnerability CVE-2026-14266 (CVSS 7.0) allows remote code execution via crafted XZ data. Update to 7-Zip 26.02. No exploitation confirmed.
CVE-2026-15378 is a blind SSRF in Red Hat OpenShift AI. The guardrails-detectors flaw exposes cloud credentials and Kubernetes secrets.
Metabase patched CVE-2026-59827 (CVSS 9.9) and CVE-2026-59826 (CVSS 9.1). These flaws enable remote code execution via unsafe H2 deserialization.
Apache IoTDB fixes five flaws in its time-series database, including privilege escalation and an unauthenticated DoS. Upgrade to 2.0.10 now.
SonicWall SMA1000 vulnerability CVE-2026-15409 (CVSS 10.0) is exploited in the wild. Public PoC enables remote code execution patch now.
Dell patched CVE-2026-56688, a PowerFlex command execution bug. This OS command injection flaw lets a privileged attacker run code as root.
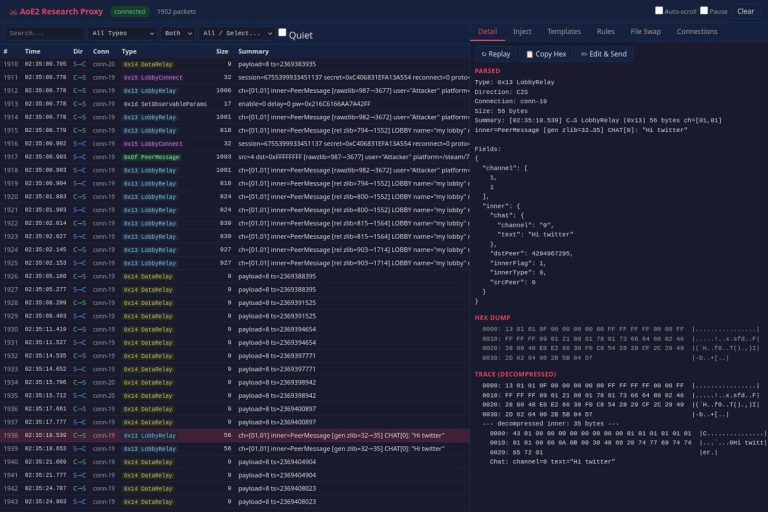
Microsoft patched a severe Age of Empires CVE. Attackers exploited game lobbies for remote code execution. Update your game immediately to stay safe.
CISA KEV catalog now lists CVE-2026-46817, a critical Oracle E-Business Suite flaw, and CVE-2023-4346 in KNX devices. Both are exploited in the wild.
Splunk patched three Splunk Enterprise vulnerabilities: CVE-2026-20296 CSRF, CVE-2026-20297 path traversal, and CVE-2026-20298 credential exposure.
F5 patched the NGINX code execution flaw CVE-2026-42533, along with CVE-2026-60005 and CVE-2026-56434. Update NGINX Plus and Open Source builds now.
Zoom vulnerability CVE-2026-53412 (CVSS 9.8) allows unauthenticated account takeover over the network. Update Zoom Workplace for Windows to 7.0.0 now.
JetBrains vulnerabilities patched: CVE-2026-62422 (CVSS 10) YouTrack authentication bypass, IntelliJ IDEA RCE CVE-2026-59792, and four TeamCity flaws.