 Do Son
TL;DR A new ProFTPD ACL bypass, CVE-2026-35025, scores 8.6 on CVSS. It lets a logged-in FTP user...
Vulnerability Report

TL;DR Plone patched three critical flaws across two add-on packages. The worst is a Plone RCE vulnerability...

TL;DR Adobe shipped fixes for 11 Adobe ColdFusion vulnerabilities on 30 June 2026. Six earn a perfect...

TL;DR Cloud Software Group patched six NetScaler vulnerabilities in NetScaler ADC and NetScaler Gateway. Three rate CVSS...
TL;DR NLnet Labs recently released version 4.14.3 of the Name Server Daemon (NSD) to patch four severe...

TL;DR NVIDIA patched several severe vulnerabilities across its AI platforms. The most critical flaw is a 9.8...

TL;DR WSO2 patched seven vulnerabilities across its API platform, including WSO2 API Manager, in June 2026. The...

TL;DR Synology fixed three vulnerabilities in Synology MailPlus Server, the email package for its NAS devices. The...
On 29 June 2026, CISA added CVE-2026-48558 to its Known Exploited Vulnerabilities catalog. The flaw is a...
TL;DR Developers patched six high-severity wolfSSL security vulnerabilities in the embedded SSL library. These flaws include an...

TL;DR Four critical security flaws currently impact all versions of the EVoke Systems Charging Station Management System....
TL;DR Cacti fixed four critical flaws in version 1.2.31. Three allow pre-authentication SQL injection, and one allows...
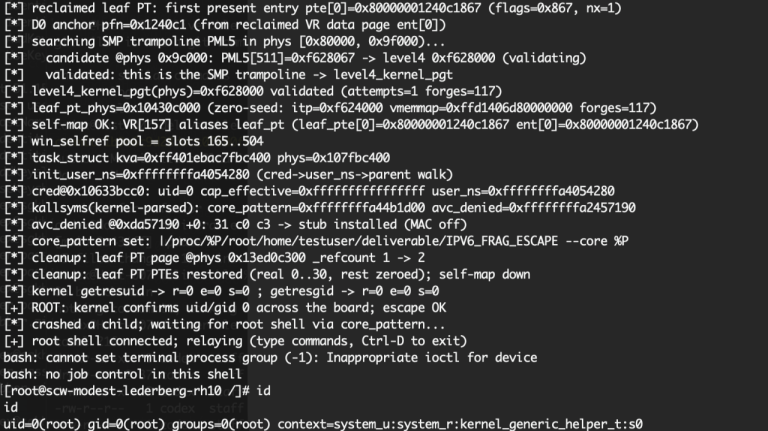
Security researcher Massimiliano Oldani has published IPV6_FRAG_ESCAPE, a working proof-of-concept for an IPv6 container escape on CentOS...

TL;DR Attackers are exploiting a Cisco Unified CM RCE flaw in live attacks. Tracked as CVE-2026-20230, it...
TL;DR Dell released urgent security updates for its thin client management platform. Two critical Dell Wyse vulnerabilities...
A critical Gemini CLI vulnerability (CVE-2026-12537) exposes developer workflows to maximum severity attacks. Google disclosed this CVSS...

A critical Hoppscotch mass assignment vulnerability threatens self-hosted API deployments. The flaw, tracked as CVE-2026-50160, allows unauthenticated...
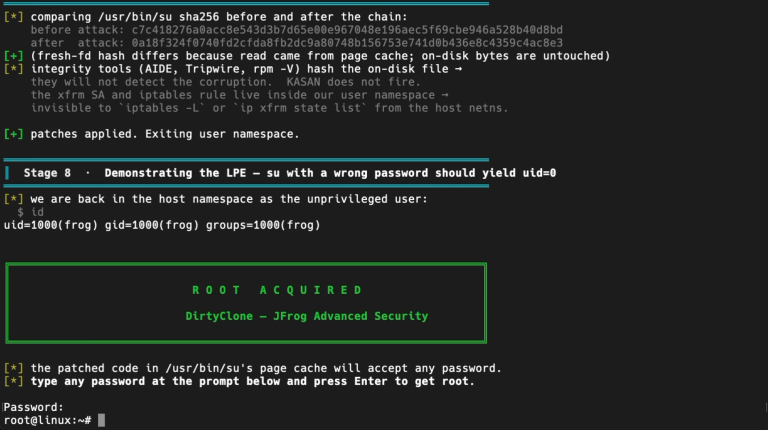
TL;DR DirtyClone is a Linux kernel privilege escalation flaw tracked as CVE-2026-43503. It scores 8.8 on the...
TL;DR Researchers publicly disclosed a libssh2 vulnerability tracked as CVE-2026-58050. The flaw lets a malicious SSH server...
TL;DR Security experts disclosed a high-severity flaw (CVE-2026-11940) in Python. A critical CPython tarfile vulnerability allows directory...

TL;DR A critical FOSSBilling template injection flaw, CVE-2026-28496, carries a CVSS score of 9.4. Attackers can read...

TL;DR The Python Software Foundation fixed a python.org authentication bypass on February 24, 2026. The flaw sat...