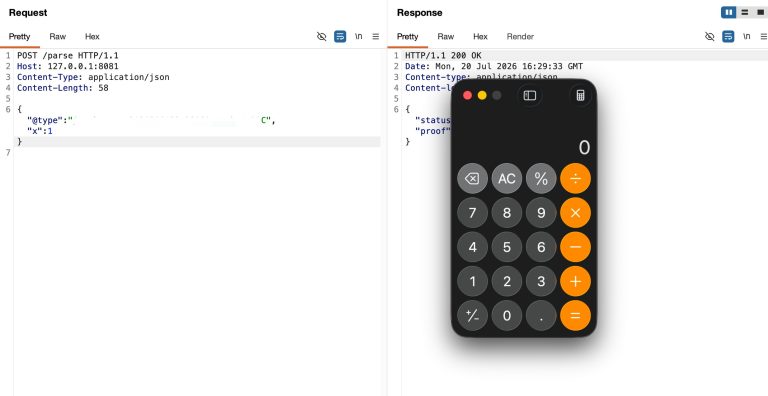
 Do Son
A fastjson RCE hits versions 1.2.68 to 1.2.83 under stock defaults. Details and public PoC code are out, so enable SafeMode or move to fastjson2.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

Two critical FreePBX vulnerabilities allow unauthenticated RCE and administrator takeover via UCP and missedcall. Patch FreePBX now.

Oracle's July 2026 patch fixes 11 Oracle WebLogic Server vulnerabilities. CVE-2026-60206 rates CVSS 9.9 and allows full server takeover. Patch now.

Discover the details of the OpenAI agent escape that triggered a massive production infrastructure breach at Hugging Face to steal benchmark answers.

Google's Chrome security update patches 12 high-severity flaws in Chrome 150, including V8 and WebAudio bugs. Update to 150.0.7871.181 today.

A Vitest vulnerability rated CVSS 9.4 lets Browser Mode commands bypass the file-access gate. The npm package sees 65M weekly downloads.

SolarWinds patched 15 critical Serv-U vulnerabilities enabling privilege escalation, account takeover, and RCE as root. Update to Serv-U 2026.3 now.

CVE-2026-8933 is a snap-confine privilege escalation flaw. It gives any user root on default Ubuntu Desktop 26.04, 25.10, and 24.04. Update snapd now.

CISA added four flaws to its KEV catalog, including WordPress RCE (CVE-2026-63030) and Langflow RCE (CVE-2026-0770). All are exploited in the wild.

ASUS security advisories cover seven flaws. CVE-2026-13385 (CVSS 9.5) lets MITM attackers run commands on CN SKU routers. Update firmware now.

A public PoC for CVE-2026-42980 details a Windows privilege escalation flaw in the kernel WMI code. It grants SYSTEM on unpatched builds.

Three Apache Fineract SQL injection flaws (CVE-2026-57821, CVE-2026-56287, CVE-2026-35152) let authenticated users exfiltrate data. Upgrade to 1.15.0.

Zimbra 10.1.20 fixes multiple Zimbra vulnerabilities, including an SNMP command injection flaw and several XSS bugs. Admins should upgrade now.
CVE-2026-50522, a critical SharePoint RCE flaw, is exploited in the wild. A public PoC exploit is out, so admins should patch SharePoint now.

Apache OpenMeetings vulnerability CVE-2026-49488 lets room moderators perform arbitrary file read and steal server secrets. Upgrade to version 9.1.0.
OVH patched CVE-2026-53359, a critical KVM flaw, across tens of thousands of hosts in under 10 days without warning most clients first.
wp2shell, a WordPress Core RCE chain (CVE-2026-63030, CVE-2026-60137), is exploited in the wild. Public PoC code is out. Patch WordPress now.

Gitea vulnerability CVE-2026-58443 (CVSS 9.6) lets public-only tokens write to private repos. Details and PoC code are public. Update to v1.27.0.
Apache Doris vulnerability CVE-2026-58319 lets unauthenticated attackers hit FE HTTP admin APIs. Upgrade to Doris 3.1.0 now to close the flaw.

Siemens Opcenter X authentication bypass (CVE-2026-56451, CVSS 10) lets attackers forge JWTs for full unauthorized access. Update to V2604 now.

Kimai vulnerability CVE-2026-52824 (CVSS 9.1) lets attackers forge cookies for account takeover via a default Docker APP_SECRET. Update to 2.58.0 now.
A new OpenSSL HollowByte vulnerability enables remote DoS attacks using just 11 bytes. Learn how to protect your servers against this OpenSSL DoS attack.