 Do Son
A critical Veeam Backup vulnerability (CVE-2026-44963) allows remote code execution. Patch immediately to avoid ransomware targeting CVE-2023-27532.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

CVE-2026-4769 exposes WAGO System I/O field devices. An early-boot flaw lets an unauthenticated attacker reach full system compromise.
A new Apache Log4j flaw, CVE-2026-49844, makes log4j-api emit invalid JSON from non-finite numbers. Patch to 2.25.5 or 2.26.1 now.
A decompress npm vulnerability (CVE-2026-53486, CVSS 9.1) lets crafted archives write files outside the target folder via path traversal. Patch now.
Three Apache IoTDB vulnerabilities include a critical path traversal (CVE-2026-24014) and an authentication bypass. Upgrade to 2.0.8 now.
Four Apache Camel vulnerabilities allow header injection, server-side request forgery, secret disclosure, and an authentication bypass. Patch to 4.21.0 now.
CISA warns of a Gardyn IoT Hub flaw. CVE-2026-13768 (CVSS 10) enables unauthenticated remote code execution on smart garden devices. Update now.
Three FreeBSD privilege escalation flaws, including a kernel use-after-free, let local users gain root. Patch FreeBSD 14 and 15 now.
A Kafka authentication bypass lets attackers replay expired JWTs against 4.0.x brokers. The OAUTHBEARER path checks nbf but not exp. No fix yet.
CVE-2026-13753 exposes a missing authorization vulnerability in HP Deskjet 2800 printers. Unauthenticated attackers can extract sensitive Wi-Fi credentials.
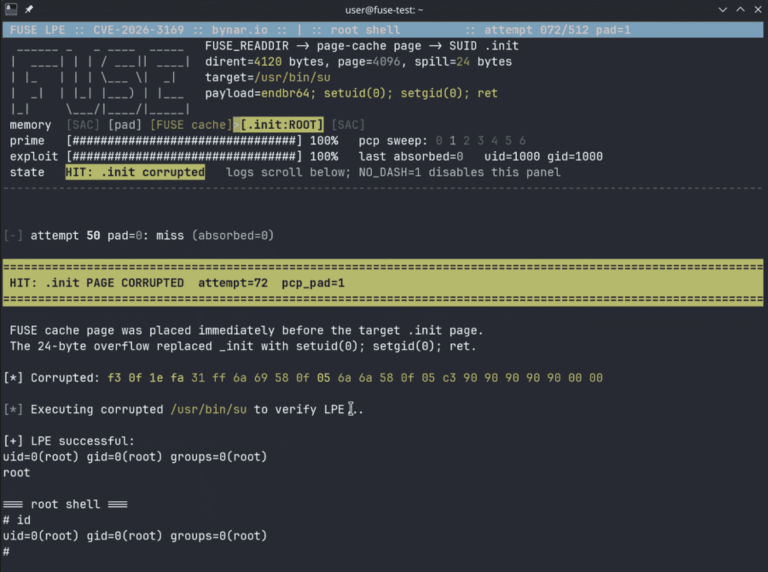
Public PoC and full details are out for CVE-2026-31694, a Linux kernel FUSE page cache overflow that gives local privilege escalation to root. Patch now.
Four GNU Guix vulnerabilities in guix substitute and guix pull allow remote privilege escalation, file overwrite, and local file disclosure. Update now.
CVE-2026-1207 is a Django SQL injection flaw (CVSS 8.3) in PostGIS raster lookups. Canada's CCCS says it is exploited in the wild. Patch now.

A Roundcube zero-click XSS, CVE-2026-54433, lets an email run script with no click. Roundcube 1.7.2 also fixes a second stored XSS. Update now.

Three Apache Lucene.NET vulnerability fixes land, including a Lucene.Net.Replicator path traversal flaw enabling unauthenticated file read. Patch now.
A critical Feast Feature Server flaw (CVE-2026-23537) lets unauthenticated attackers perform arbitrary file write and risk remote code execution. Act now.
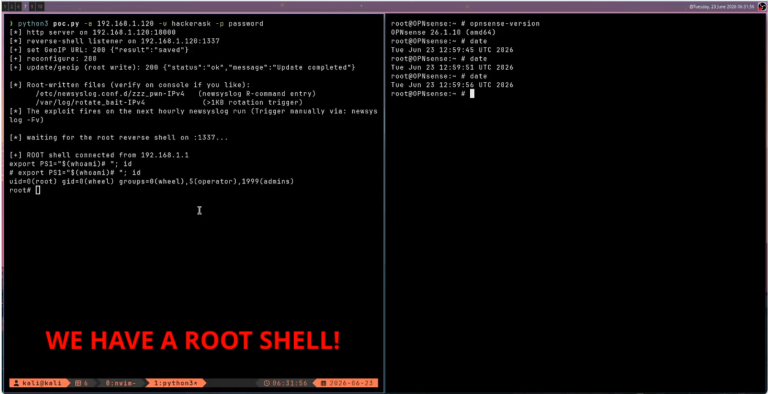
OPNsense root RCE flaws are public with PoC code. CVE-2026-57155 (9.9) chains an arbitrary file write to root. Patch 26.1.11 or 26.4.1p1 now.
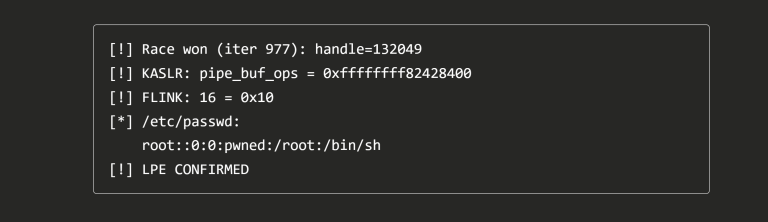
Public PoC and write-up detail a Linux kernel privilege escalation flaw (CVE-2026-46215) in DRM GEM. A local user gets root in ~99% of runs.
Progress patched three MOVEit Transfer flaws, including a stored XSS bug (CVE-2026-11903). No exploitation is confirmed. Update now.
Microsoft patched the RoguePlanet Microsoft Defender zero-day, CVE-2026-50656, a race condition that grants SYSTEM privileges. A public PoC exists.

A critical HPLIP vulnerability, CVE-2026-14544 (CVSS 9.8), lets a remote attacker gain arbitrary code execution via crafted print data. Patch now.
The GitLab patch release fixes 8 flaws, including a high-severity cross-site scripting bug (CVE-2026-6896). Update to 19.1.2 now.