
 Do Son
A critical Langflow RCE vulnerability (CVE-2026-10561) scores CVSS 10 and enables unauthenticated remote code execution. Upgrade to 1.9.4 now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

Google's Chrome 149 security update patches 18 flaws, including four critical WebGL and Autofill use-after-free bugs. Update to 149.0.7827.196.

Discover critical Gitea security flaws exposing servers to account takeovers and SSRF attacks. Read about CVE-2026-20896 and CVE-2026-22874 patches today.

A critical CVSS 9.2 Java deserialization vulnerability allows an OpenDJ unauthenticated RCE. Patch CVE-2026-46495 immediately to protect your servers.
A CVSS 8.7 TP-Link router command injection flaw allows unauthenticated remote code execution. Patch CVE-2026-11834 to stop this DHCP option vulnerability.
CISA flags an AVer PTC camera flaw, CVE-2026-40624, enabling remote code execution. The CVSS 9.8 RCE bug affects four PTC models.

Three containerd critical vulnerabilities, including CVE-2026-53492, allow attackers to execute host commands and poison image caches. Patch immediately.

Three Webmin vulnerabilities, including a critical authentication bypass (CVE-2026-56020), expose servers. Update to Webmin 2.641 to stay safe.
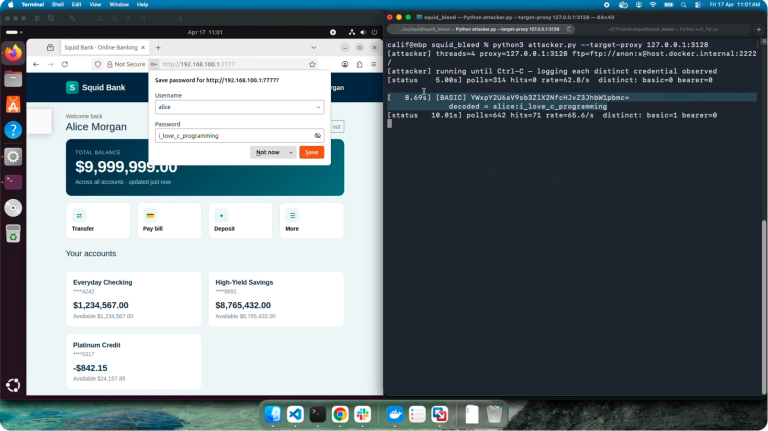
The Squidbleed vulnerability is a Squid proxy memory leak exposing user credentials. CVE-2026-47729 details and PoC exploit code are now public.

CISA added four actively exploited vulnerabilities to its KEV catalog, hitting Ubiquiti UniFi OS and Lantronix EDS5000. Patch before June 26, 2026.
Three critical Tinyproxy request smuggling vulnerabilities, including CVE-2026-54388, expose networks to severe attacks. Update your proxy servers immediately.

A critical libssh2 vulnerability, CVE-2026-55200, lets remote attackers trigger an out-of-bounds write and achieve remote code execution. Patch now.

Three critical MariaDB server vulnerabilities, including a CVSS 10 flaw, allow attackers to execute shell commands. Patch your database servers immediately.
Mitel patched 12 critical MiCollab vulnerabilities, several at CVSS 10.0. Unauthenticated command injection and SQL injection flaws need urgent updates.
ESET found vendor-signed UEFI applications vulnerable to a Secure Boot bypass. Attackers can run pre-boot code. Update firmware and the UEFI DBX now.

Two critical HAProxy vulnerabilities threaten reverse-proxy security. These flaws allow denial of service and smuggling attacks. Patch servers immediately.

QNAP QuMagie vulnerabilities let unauthenticated attackers access media files, causing information disclosure. Patch QuMagie and License Center now.
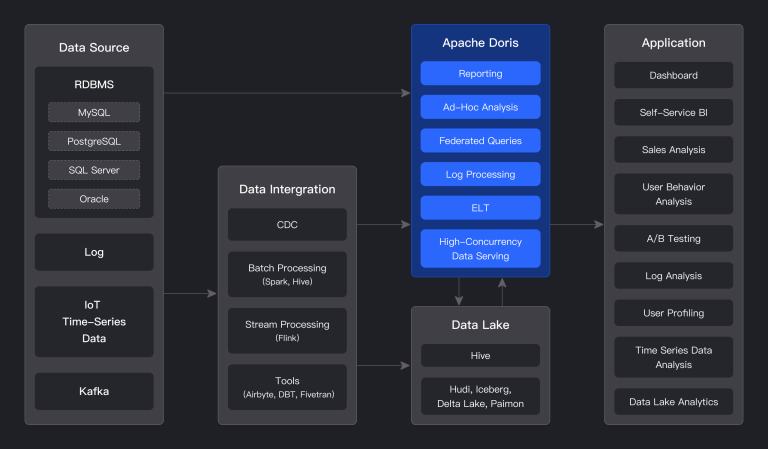
A critical Apache Doris SQL injection vulnerability identified as CVE-2025-66336 allows attackers to bypass authentication. Upgrade your servers now.
Four undici vulnerabilities (CVE-2026-6734, CVE-2026-9697) affect the Node.js HTTP client, which sees 133M weekly downloads. Update undici now.
CVE-2026-55518 is a critical Avo authorization bypass flaw enabling privilege escalation in Ruby on Rails admin panels. Update to Avo 3.32.1 now.

Three critical pgAdmin 4 vulnerabilities (CVE-2026-12046, CVE-2026-12048, CVE-2026-12045) risk XSS and RCE. Update to pgAdmin 4 9.16 now.

A public PoC exploit for the FreeBSD kTLS vulnerability (CVE-2026-45257) enables local privilege escalation to root. Patch your FreeBSD systems now.