 Do Son
Urgent: CrowdSec warns CVE-2024-9643 in Four-Faith routers has hit mass exploitation phase. Attackers abuse hardcoded logins to build botnets. Patch now!
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

PostgreSQL releases updates for versions 14-18 fixing 11 vulnerabilities (CVSS 8.8). Plus, critical End-of-Life deadline issued for Postgres 14.

Technical details and GitHub PoC exploits disclosed for PostgreSQL pgcrypto CVE-2026-2005. Low-privilege users can seize root superuser RCE. Patch now!

CVE-2026-46442 in Flowise allows authenticated users to escape the NodeVM sandbox and execute system commands. Secure your AI infrastructure now!
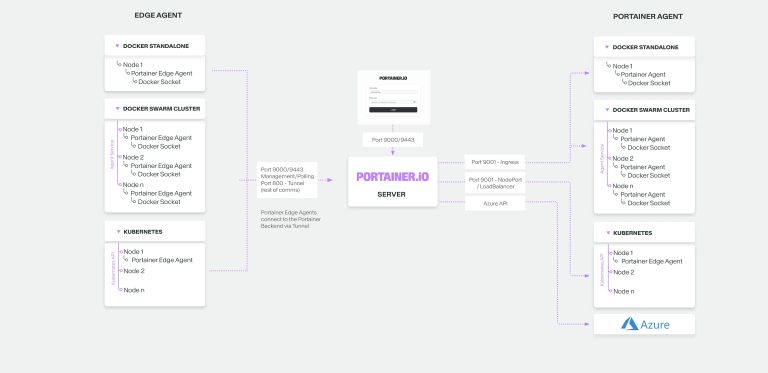
Portainer fixes two critical 9.4 CVSS flaws (CVE-2026-44848/49) allowing instant container escape to host root. Patch your environments now!
Marten .NET library suffers a critical 9.8 CVSS SQL injection flaw (CVE-2026-45288). Learn how to block the exploit and patch your databases now!

Critical CVE-2026-35194 flaw in Apache Flink allows RCE via SQL injection on TaskManagers. Upgrade your clusters immediately to secure your data!
Two critical flaws in Strapi CMS (CVE-2026-27886 & CVE-2026-22599) allow unauthenticated admin takeover and SQL injection. Update your nodes now!

n8n fixes three critical 9.4 CVSS flaws (CVE-2026-44790/91/89). Authenticated users can break sandboxes for local file read and server-level RCE. Patch now!

The GhostLock whitepaper exposes a critical blind spot in ransomware defense. Low-privilege users can freeze SMB shares with zero data encryption.

Details and PoC code for the "MiniPlasma" zero-day exploit are now public. See how a 6-year-old flaw grants SYSTEM access on fully patched Windows 11.
Quest KACE SMA CVE-2025-32975 (CVSS 10) exploited in the wild. Attackers bypass auth to seize admin control. Patch to version 14.1.101 or 14.0.341 now!

VMware Fusion CVE-2026-41702 allows local users to gain root access via a TOCTOU race condition. Secure your host and update to 26H1 immediately!
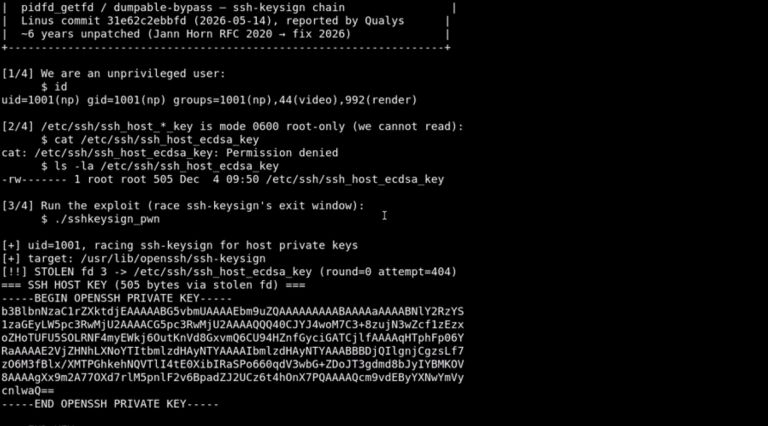
Technical details and PoC exploits disclosed for Linux Kernel ptrace flaw. Unprivileged users can steal root file descriptors. Patch to May 14 release!

cPanel & WHM fix 5 critical vulnerabilities (CVE-2026-29205). Fixes for arbitrary file read, SQLi, and privilege escalation are now live. Update now!

ELECOM routers hit by critical 9.8 CVSS flaws (CVE-2026-42062). Unauthenticated attackers can execute OS commands and bypass auth. Update firmware now!

Cisco fixes a critical 8.6 CVSS XXE flaw (CVE-2026-20224) in Catalyst SD-WAN Manager. Unauthenticated attackers can read arbitrary files. Patch now!

CVE-2026-8178 in Amazon Redshift JDBC Driver allows RCE via unsafe class loading. Protect your data warehouse and update to version 2.2.2 now!

pgAdmin 4 v9.15 fixes a 9.4 CVSS auth bypass and multiple RCE flaws. Attackers can execute OS commands via SQL tools. Upgrade your pgAdmin server now!

CVE-2026-44477 in CloudNativePG allows low-privilege users to gain root-level RCE via metrics exporters. Update to version 1.29.1 or 1.28.3 now!
Exploited in the Wild: Critical OWA Spoofing Flaw (CVE-2026-42897) Hits On-Premises Exchange Servers
Exploited in the Wild: Critical OWA Spoofing Flaw (CVE-2026-42897) Hits On-Premises Exchange Servers
CVE-2026-42897 exploited in the wild. A 8.1 CVSS OWA flaw allows RCE via malicious emails. Verify your Exchange Emergency Mitigation (EM) status now!

Google Chrome patches 79 vulnerabilities, including 14 "Critical" RCE threats. Update to version 148.0.7778.167 now to protect your data and browser.