
 Do Son
The Dirty Frag Linux vulnerability (CVE-2026-43284) is being actively exploited in the wild. Learn how to secure your servers from this root LPE exploit.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Security researchers expose catastrophic flaws in Sandboxie. CVE-2026-34459 enables a direct sandbox escape to SYSTEM privileges. Update to v1.17.3 today.

Protect your app from CVE-2026-23870. Learn how this high-severity React Server Components DoS flaw crashes servers and how to patch your React 19 build today.
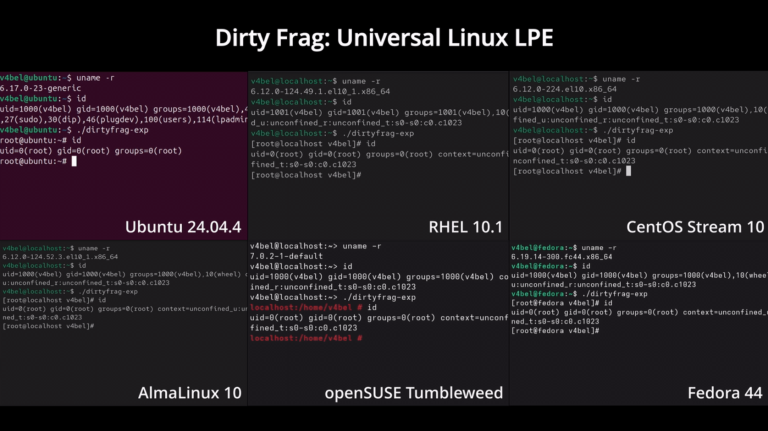
Dirty Frag PoC released! Researcher v4bel discloses a universal Linux root exploit targeting the page cache. No patches yet—apply module mitigations now!

Rancher Fleet fixes a 9.9 CVSS flaw (CVE-2026-41050) allowing tenants to bypass ServiceAccount isolation and steal secrets. Upgrade your GitOps engine now!

Zabbix fixes high-severity XSS (CVE-2026-23926) and Oracle injection flaws. Don't let your monitoring tool become a backdoor—upgrade your Zabbix server now!

Ivanti confirms active exploitation of EPMM (CVE-2026-6973). Attackers are using old credentials to hijack mobile management. Patch to v12.8.0.1 immediately!
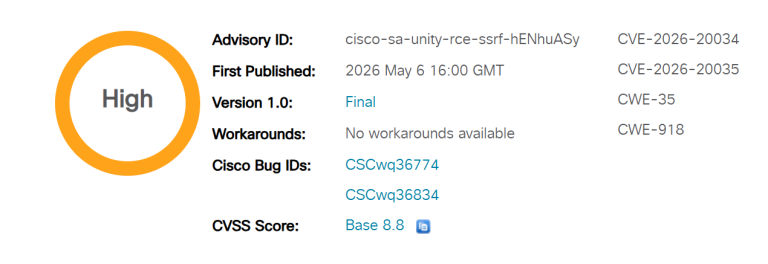
Cisco warns of critical RCE (CVE-2026-20034) and SSRF flaws in Unity Connection. Authenticated root access and unauthenticated network probing are possible. Patch now!
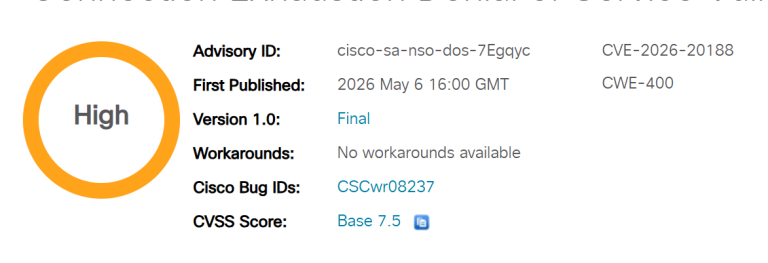
Cisco warns of a critical DoS flaw (CVE-2026-20188) in CNC and NSO. Unauthenticated attackers can freeze network management. Patch to CNC 7.2 or NSO 6.4.1.3 now!

WatchGuard Agent v1.25.03.0000 fixes critical privilege escalation flaws (CVE-2026-6787) and buffer overflows. Secure your Windows endpoints and patch now!

ArcadeDB 26.4.1 fixes a critical 9.0 CVSS authorization bypass (CVE-2026-44221) that dismantles database isolation. Secure your multi-model data and patch now!
Spring Cloud Config fixes a 9.1 CVSS directory traversal (CVE-2026-40982) and a GCP secret leak. Secure your distributed system—upgrade to the latest patches!

Bitcoin Core v29.0 fixes a high-severity use-after-free bug (CVE-2024-52911) that could allow attackers to remotely crash nodes. Upgrade your node today.

Palo Alto Networks warns of active root RCE (CVE-2026-0300) in PAN-OS. State-sponsored cluster CL-STA-1132 is targeting edge assets. Patch and restrict now!
Chrome’s Security Overhaul: 127 Fixes and $100k+ in Bounties Power the New Chrome 148 Stable Release

Chrome’s Security Overhaul: 127 Fixes and $100k+ in Bounties Power the New Chrome 148 Stable Release
Google Chrome 148 is out with 127 security fixes, including 3 Critical flaws in Blink and V8. Protect your data—check your version and update today!

Redis releases critical patches for 5 vulnerabilities, including RCE via the RESTORE command (CVSS 7.7). Secure your self-managed Redis instances immediately!
Apache Wicket 10.9.0 fixes 3 Critical flaws: Path Traversal (CVE-2026-43975), Session Fixation, and Resource Guard bypass. Secure your Java apps and patch now!
OpenMRS v2.8.6 fixes a critical 9.1 CVSS SSTI flaw and Zip Slip RCE. Protect global patient health records and upgrade your EMR infrastructure immediately!
Critical 9.0 CVSS flaw in Thymeleaf (CVE-2026-41901) allows SSTI and arbitrary code execution. Secure your Java web apps—upgrade to v3.1.5.RELEASE now!

Security researcher Tom reveals Microsoft Edge stores all saved credentials in plaintext memory. Learn why Microsoft calls this a feature, not a bug.
A critical 7.5 CVSS flaw in Nix (CVE-2026-44028) allows standard users to gain root privileges via a stack overflow. Update your Nix installation immediately!

A critical 9.6 CVSS flaw in Argo CD (CVE-2026-42880) allows read-only users to extract plaintext Kubernetes secrets via Server-Side Diffs. Patch to v3.3.9 now!