 Do Son
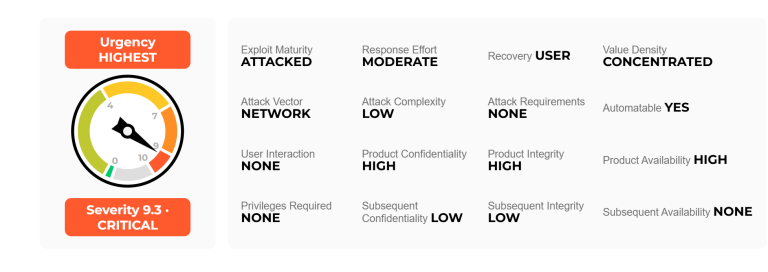
Palo Alto Networks confirms CVE-2026-0300 is being exploited in the wild. The 9.3 CVSS flaw allows unauthenticated root RCE. Secure your PAN-OS firewalls now!
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

Critical 9.8 CVSS flaws in vm2 affect 5.7M monthly users, allowing RCE via WASM and Promise bypasses. Upgrade to vm2 v3.11.0 immediately to secure your host.

Apache Thrift v0.23.0 fixes critical Rust DoS, Java MitM, and Node.js path traversal flaws. Secure your cross-language microservices and upgrade immediately!

SUSE Rancher v2.14.1 fixes an 8.4 CVSS path traversal flaw (CVE-2026-25705) in UI Extensions. Prevent binary hijacking and host access—upgrade immediately!

Public PoC exploit released for OPNsense! A critical root-level RCE and lockout bypass allow total firewall takeover. Upgrade to OPNsense 26.1.7 immediately.
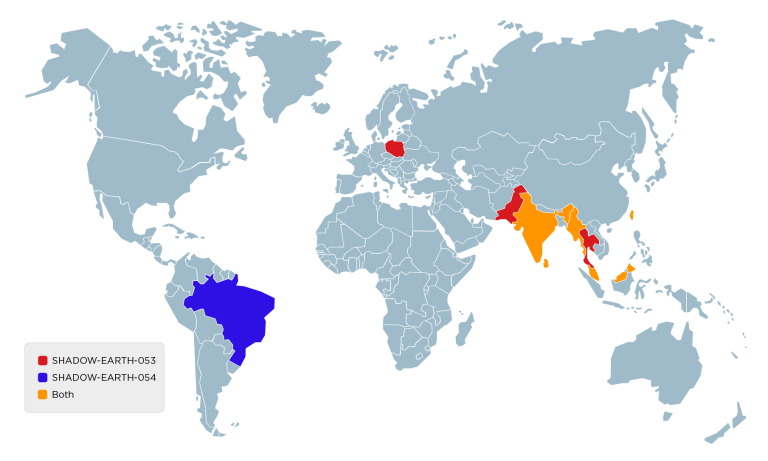
SHADOW-EARTH-053 is breaching governments and NATO using old ProxyLogon flaws and ShadowPad. Learn how this China-aligned group stays hidden via registry loading.

Qualcomm’s May 2026 bulletin reveals critical 9.8 CVSS flaws in Software Center & Bootloaders. Remote RCE and memory corruption affect millions of devices.

A critical injection flaw (CVE-2026-40563) in Apache Atlas lets attackers manipulate Gremlin logic to extract restricted enterprise data. Patch to v2.5.0!

Apache releases v2.4.67 to fix an HTTP/2 Double Free RCE (CVE-2026-23918) and auth bypasses. Millions of servers are affected—upgrade your infrastructure now!

Apache Polaris 1.4.1 fixes critical flaws allowing attackers to bypass S3/GCS boundaries and seize cloud credentials. Patch your Iceberg catalog now!

Google warns of CVE-2026-0073: a critical zero-click Android vulnerability allowing remote code execution via Wireless ADB. Patch to May 2026 level now!

Apache Neethi v3.2.2 patches critical flaws, including an exponential complexity attack and infinite loops. Secure your Java web services and patch today!

Gotenberg PDF API hit with a rare CVSS 10 flaw. Unauthenticated RCE, file overwrites, and SSRF bypasses discovered. Upgrade to version 8.32 immediately.

GnuTLS v3.8.13 fixes critical heap overwrites, identity truncation, and OCSP bypasses. Secure your Linux comms and upgrade to the latest version now.
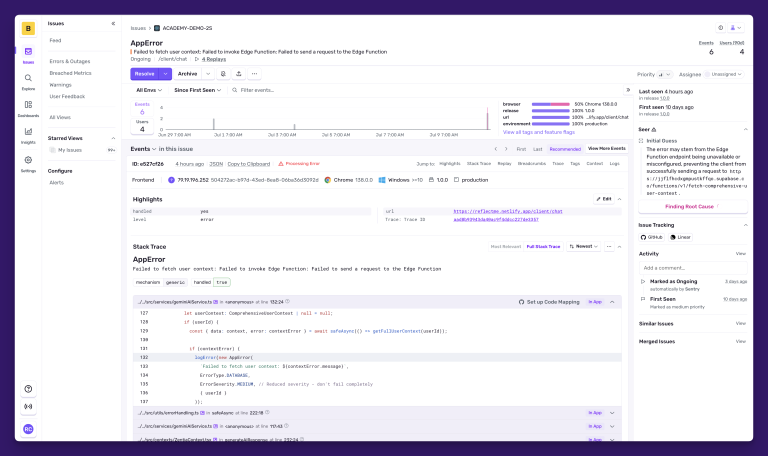
Sentry reveals a critical 9.1 CVSS flaw (CVE-2026-42354) in SAML SSO. Multi-org instances are at risk of account takeover via identity linking. Patch now!

A critical 9.1 CVSS flaw in a Go auth library causes a Patreon "identity collision," merging all users into one account. Upgrade to v2.1.2 immediately!
A critical 9.9 CVSS IDOR flaw in Comet Backup allows complete cross-tenant account takeovers. Self-hosted administrators must patch servers immediately!

Apache MINA issues emergency patches for two 9.8 CVSS RCE flaws left behind by mistake. Unauthenticated attackers can bypass filters via deserialization.

MOVEit Automation faces a critical 9.8 CVSS flaw (CVE-2026-4670). Attackers can bypass auth to seize admin control and expose data. Patch immediately.

FreeBSD warns of CVE-2026-42511: a critical dhclient flaw allowing rogue DHCP servers to execute code as root via BOOTP file injection. Patch and reboot now!

Snyk warns of active in-the-wild exploitation of the Qinglong platform. Two authentication bypass flaws grant attackers RCE to deploy .fullgc cryptominers.
A critical 9.8 CVSS vulnerability in the Temporary Login plugin puts 40,000+ WordPress sites at risk of account takeover. Patch to version 1.1.0 now!