
 Do Son
Splunk releases coordinated patches for CVE-2026-20240 and adjacent flaws exposing raw session cookies, data filters, and triggering server DoS.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

Altium patches dual critical 9.4 CVSS flaws (CVE-2026-9129 & CVE-2026-9102) allowing authenticated users to execute remote code and steal files.

PowerDNS coordinates patches for CVE-2026-42001 and adjacent flaws that trigger server crashes, GSS-TSIG memory corruption, and view data leaks. Patch now!
CISA updates its KEV Catalog with critical flaws in Langflow (CVE-2025-34291) and Trend Micro Apex One. Federal agencies ordered to patch by June 4, 2026.

Urgent: Millions affected by "nginx-poolslip," a critical Nginx 1.31.0 zero-day that bypasses ASLR via heap feng shui to grant unauthenticated remote RCE.
Coder patches a critical 9.1 CVSS signature bypass (CVE-2026-46354) in Azure identities that allows unauthenticated workspace token theft. Patch now!
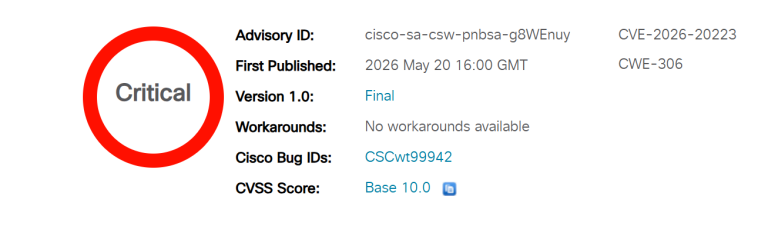
Cisco drops an urgent advisory for CVE-2026-20223 (CVSS 10.0) in Secure Workload. Unauthenticated remote attackers can steal full Site Admin privileges.
Unpatched CVSS 10 flaw (CVE-2026-45829) in ChromaDB allows unauthenticated remote code execution via Hugging Face models. Isolate your servers now!
Google has dropped an urgent Chrome desktop update fixing 16 vulnerabilities, including two critical sandbox subversion flaws in WebRTC and the UI.

Urgent: Drupal releases patches for highly critical SQLi flaw CVE-2026-9082. Unauthenticated attackers can exploit PostgreSQL backends for full remote RCE.

CERT/CC warns of unpatched critical flaws in SGLang (CVE-2026-7301) exposing AI inference models to unauthenticated RCE. Restrict your ports now!

Apache OFBiz releases version 24.09.06 to patch severe RCE flaws, token forgery, and a critical password-reset authentication bypass. Upgrade now!

F5 warns of a critical 9.2 CVSS flaw (CVE-2026-8711) in NGINX JavaScript (njs). Unauthenticated attackers can trigger heap overflows and potential RCE.
ZKTeco patches a critical 9.1 CVSS flaw (CVE-2026-8598) in CCTV cameras leaking admin credentials without authentication. Upgrade your firmware now!
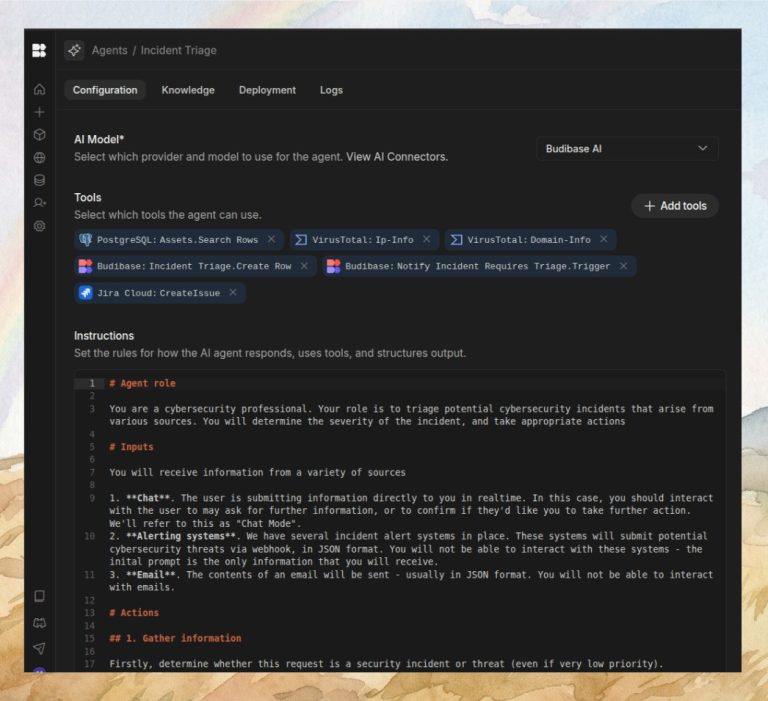
Budibase patches a critical 9.9 CVSS SCIM authorization bypass (CVE-2026-46425). Basic users can delete admins and hijack accounts. Update now!
NVIDIA patches a critical 9.8 CVSS authentication bypass (CVE-2026-24207) in Triton Inference Server. Update to r26.03 to secure AI workloads!

FreePBX fixes critical 9.1 CVSS flaw (CVE-2026-46376) where hardcoded credentials grant unauthenticated portal access. Update your modules now!
Arcane fixes a critical 9.9 CVSS vulnerability (CVE-2026-45625) that allows basic users to steal GitOps credentials in plaintext. Update to 1.19.0!
PoC Exploit Code Publicly Released: New “PinTheft” Linux Flaw Overwrites Page Cache for Instant Root
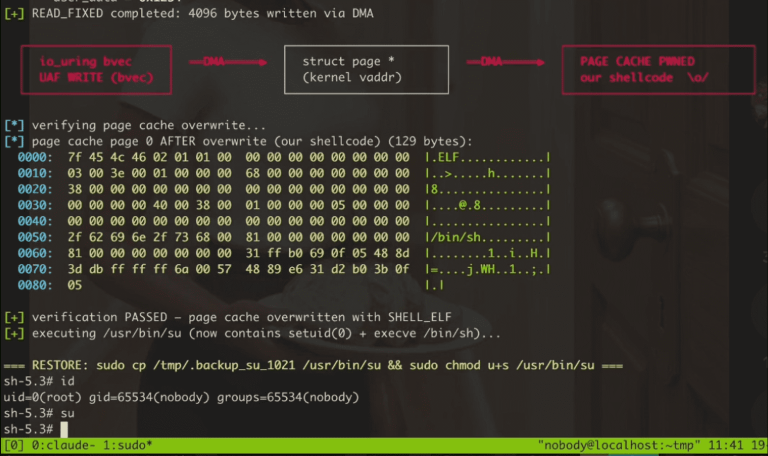
PoC Exploit Code Publicly Released: New “PinTheft” Linux Flaw Overwrites Page Cache for Instant Root
Technical details and a working PoC exploit are public for PinTheft, a critical Linux local privilege escalation bug. Block the RDS module now.
NVIDIA has issued critical security updates for its GPU display drivers and vGPU software to fix a high-severity 8.8 CVSS use-after-free flaw. Patch now!

Critical 18-year-old "NGINX Rift" flaw CVE-2026-42945 is under active exploitation. Learn how to patch your proxies and block the unauthenticated heap overflow.

Microsoft pivots on its "by design" stance, updating Edge to version 148.0 to stop caching your entire plaintext password vault in active volatile memory.