
 Do Son
Juju's critical CVSS 10 flaw (CVE-2026-5412) allows low-level users to steal master cloud credentials. Secure your AWS/Azure/GCP environments—upgrade now!
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Google ADK (CVE-2026-4810) faces a critical 9.3 CVSS RCE flaw. Unauthenticated attackers can hijack AI agents on GKE & Cloud Run. Update and redeploy now!
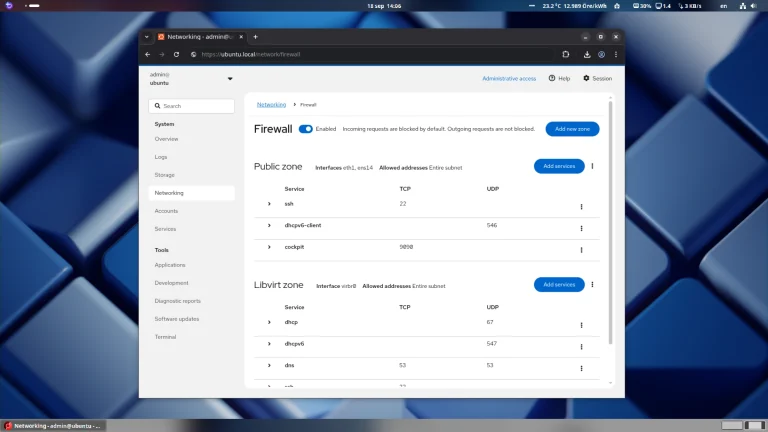
Cockpit CVE-2026-4631 allows unauthenticated RCE on Linux servers via SSH injection. Stop the unauthorized takeover—upgrade to Cockpit version 360 now!

Critical Remote Command Injection flaws in PHP Composer's Perforce integration (CVE-2026-40176 & CVE-2026-40261) could lead to full system compromise. Patch now.

wolfSSL (CVE-2026-5194) faces a critical 9.3 CVSS flaw in ECDSA certificate validation. Attackers can bypass security and spoof trusted hosts. Audit today!
CISA adds 7 active exploits to the KEV catalog, from legacy Office bugs to 2026 Fortinet zero-days. Patch these high-risk flaws now to secure your network.
Qlik issues a critical 9.8 CVSS alert for Talend JobServer and Runtime. Unauthenticated RCE via JMX ports puts data pipelines at risk. Patch immediately.
A maximum10 CVSS score: Paperclip's RCE flaw allows unauthenticated server takeover in 6 API calls. Secure your AI workforce and update to v2026.410.0 now!
Ubiquiti fixes critical 9.8 CVSS RCE flaws in UniFi Play PowerAmp and Audio Port. Don't let attackers control your sound—update your firmware immediately.

SAP’s April 2026 updates fix a critical 9.9 CVSS SQL injection in Business Warehouse and 19 other security flaws. Audit your S/4HANA and BPC systems today.

Microsoft warns of a 50M-user flaw in EngageSDK affecting crypto wallets. An intent redirection bug could leak private data. Update to v5.2.1 now!

Synology urges SSL VPN Client users to update to v1.4.5-0684. Fixes critical 8.1 CVSS flaw allowing PIN theft and traffic interception. Secure your data now!

Mitsubishi Electric warns of 9.3 CVSS flaws in GENESIS64 & ICONICS. Attackers can leak SQL credentials to destroy or tamper with industrial data. Patch now!

Axios CVE-2025-62718 allows a critical NO_PROXY bypass via hostname normalization errors. Protect your internal network from SSRF—patch or normalize today!

Apache Log4j 2.25.4 fixes 4 "silent" flaws, including TLS bypasses and log injection. Secure your infrastructure—upgrade now to prevent data loss.
Apache ActiveMQ patches critical TLSv1.3 memory exhaustion (CVE-2026-39304) and an MQTT regression. Upgrade to 6.2.4 or 5.19.5 to secure your broker!

Apache OpenMeetings 9.0.0 fixes critical flaws including hard-coded "remember-me" keys and REST login credential exposure. Secure your video suite today!
Apache Storm patches a critical RCE via unsafe deserialization and a stored XSS in its UI. Secure your data streams—upgrade to version 2.8.6 today!
LiteLLM patches critical 9.4 CVSS flaws, including OIDC cache collisions and pass-the-hash attacks. Secure your AI infrastructure—upgrade to v1.83.0 now!
Laravel Passport patches a 7.1 CVSS authentication bypass where machine tokens masquerade as human users. Protect your app—upgrade to v13.7.1 now!

Signal's encryption is solid, but iOS is leaking your data. Learn how the FBI uses notification caches to recover deleted messages and how to stop it.
Unauthenticated RCE in marimo (CVE-2026-39987) exploited in the wild in record time. Attackers gained root access in under 10 hours. Patch to v0.23.0 now!