
 Do Son
Kyverno (CVE-2026-4789) faces an unpatched SSRF flaw in its CEL HTTP functions, allowing attackers to bypass K8s namespaces. Secure your cluster now!
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.

Perl (CVE-2026-4176) faces a 9.8 CVSS flaw due to a vulnerable zlib module. Affecting versions since 5.9.4, it demands an urgent update. Learn how to patch.
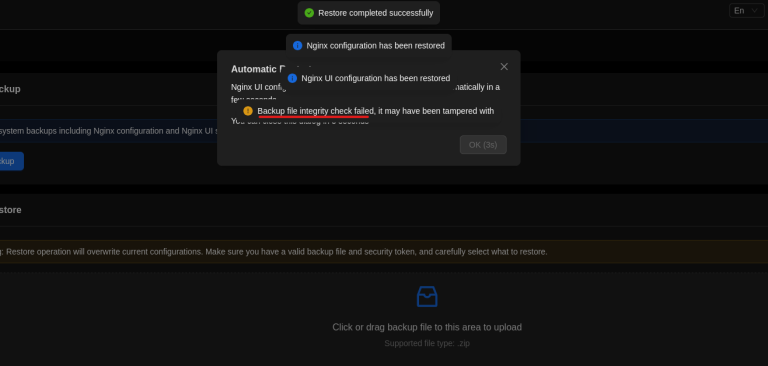
Public PoC exploit and details are out for Nginx UI’s 9.4 CVSS backup flaw (CVE-2026-33026). Attackers can hijack servers via tampered backups. Update now!
CERT/CC warns of critical flaws in CrewAI. Insecure fallbacks and prompt injection enable RCE and SSRF. No full patch yet—learn how to secure your agents.

Public PoC code and full details are out for a 9.8 CVSS flaw in Nginx UI (CVE-2026-33032). With no official patch, servers are at risk. Secure yours now!

CloudSEK warn of instant exploitation for Oracle WebLogic's CVE-2026-21962. With a 10.0 CVSS score, this RCE allows full server takeover. Patch now!
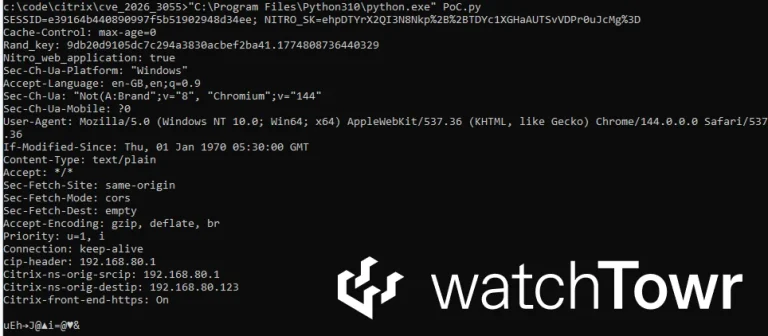
CISA adds Citrix NetScaler CVE-2026-3055 to KEV. This 9.3 CVSS flaw "bleeds" admin sessions via SAML. Federal agencies must patch by April 2, 2026.
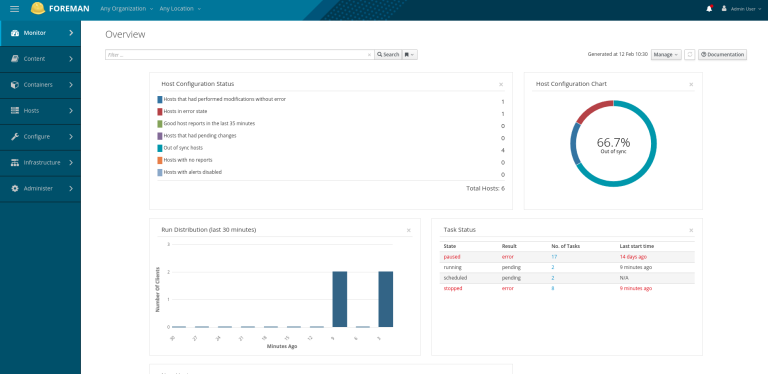
Foreman patches a critical 8.0 CVSS command injection flaw (CVE-2026-1961). Malicious hostnames can trigger RCE via WebSocket proxies. Update to 3.18.1 now!
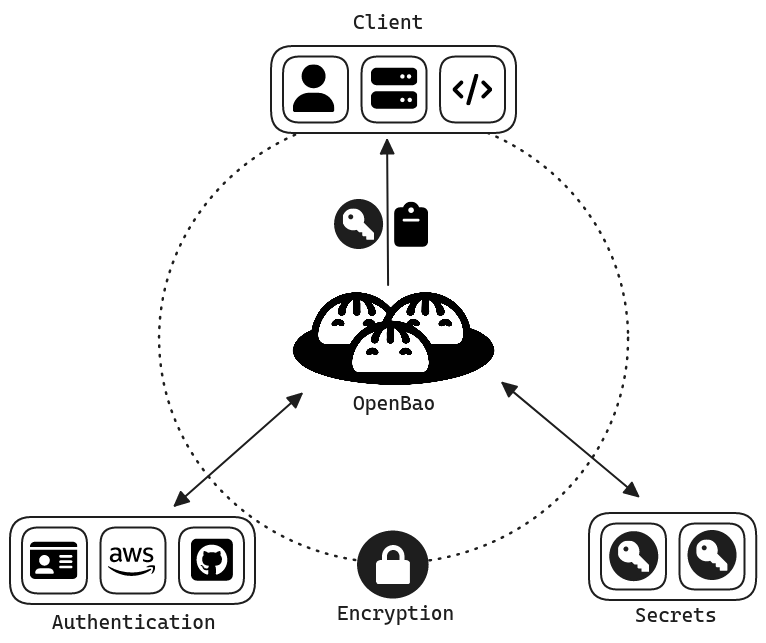
OpenBao patches critical 9.6 and 9.4 CVSS flaws in OIDC flows. Learn how "direct mode" enables session hijacking and XSS token theft. Update to 2.5.2 now.
Node-convict (CVE-2026-33864) faces a 9.4 CVSS Prototype Pollution flaw. Bypass filters and hijack Node.js apps. Update to version 6.2.5 now to stay secure.
OpenTelemetry patches a critical 9.3 RCE flaw (CVE-2026-33701) in its Java agent. Unfiltered RMI deserialization allows full system takeover. Update to 2.26.1.

Researchers reveal critical RCE and ARM-specific flaws in libpng (CVE-2026-33636 & 33416). Affecting decades of apps, these bugs require an immediate update.
Vim patches a critical 8.2 CVSS bug chain in modelines and tabpanels. Opening a malicious file triggers instant RCE. Update to 9.2.0272 now to stay safe.
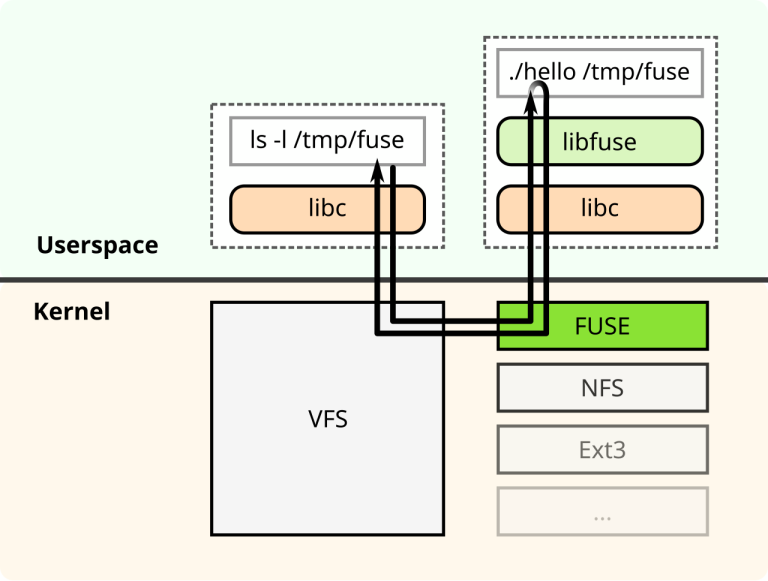
Researchers uncover two flaws in libfuse's io_uring transport (CVE-2026-33150 & 33179). Impacting Kubernetes CSI drivers, these bugs allow RCE and DoS. Patch now!
Scriban’s 9.1 CVSS flaw allows sandbox escapes in .NET apps via a cache bypass. Over 40M downloads affected. Update to version 7.0.0 to secure your templates.
A 2026 "technological ascension" in web skimming uses WebRTC to steal credit cards via UDP, bypassing CSP and WAF. Five global billion-dollar firms hit.

Grafana patches a critical 9.1 RCE (CVE-2026-27876) in SQL expressions that allows SSH hijacking. Update to 12.4.2 now to secure your monitoring host.
CISA adds F5 BIG-IP RCE (CVE-2025-53521) to its KEV Catalog. With a 9.8 CVSS score and active exploits, federal agencies must patch by March 30, 2026.

n8n patches critical 9.4 CVSS RCE flaws in Merge and GSuiteAdmin nodes. Attackers can hijack servers via SQL sandbox escapes or prototype pollution. Update now!

CISA warns of a 9.8 CVSS flaw in Pharos Mosaic Show Controllers (CVE-2026-2417). Unauthenticated attackers can gain root access. Update to version 2.16 now.

MantisBT patches a critical 9.3 CVSS auth bypass (CVE-2026-30849) and high-severity XSS flaws. Learn how MySQL type conversion opens the door. Update now!

A critical 9.8 CVSS zero-click flaw (ZDI-CAN-30207) hits Telegram, affecting 1 billion users. No interaction needed for full system hijack. Patching now!