
 Do Son
AMD recommends using other published mitigations for CVE-2017-5715, currently in Linux users can control which mitigations
Vulnerability
researchers have discovered that there is another way to exploit the Spectre-V2 attacks - Branch History Injection
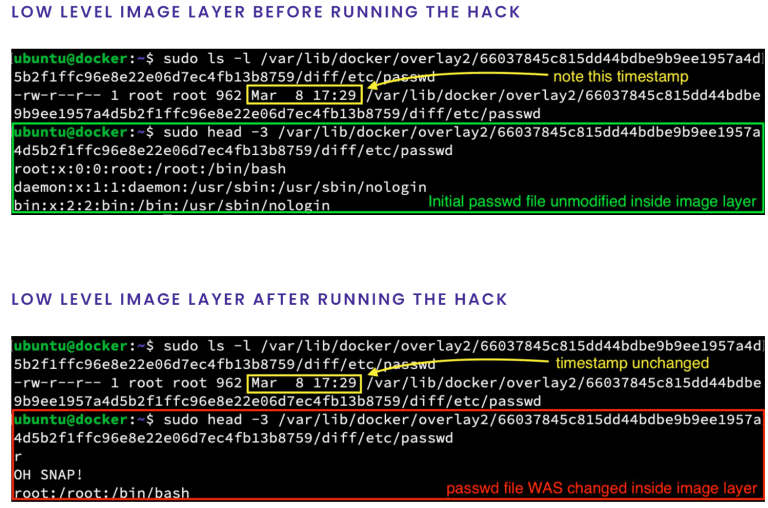
There is a description of how the CVE-2022-0847 vulnerability affects your container images on the website of security firm Snyk
Researchers have successfully reproduced this flaw on Google Pixel 6 running Android 12, Google Pixel 6 is vulnerable to the CVE-2022-0847
The Linux Kernel team has fixed the CVE-2022-0847 vulnerability in versions 5.16.11, 5.15.25, and 5.10.102. POC and EXP have been disclosed
This version does not contain any new features or changes but is only released to fix two newly discovered zero-day vulnerabilities in Firefox

VMware issued a security bulletin to disclose a remote code execution vulnerability (CVE-2022-22947) in Spring Cloud Gateway
CVE-2022-23131 Unsafe client-side session storage leading to authentication bypass/instance takeover via Zabbix Frontend with configured SAML

Recently, Apache APISIX officially released a security bulletin, disclosing a remote code execution vulnerability (CVE-2022-24112)

Google released a security bulletin to reveal the CVE-2022-0609 vulnerability, which is a major security threat to user-after-free
There is a WebKit vulnerability (CVE-2022-22620) that allows hackers to maliciously create web content, resulting in arbitrary code execution

PHP Everywhere plug-in has been used by 30,000 websites around the world. Attackers can exploit the vulnerability on the affected websites to execute arbitrary code

Intel recently released a new security advisory that contains 16 new BIOS-related vulnerabilities. Attackers can exploit these vulnerabilities
security researcher Rory McCune has disclosed a high-risk buffer overflow vulnerability (CVE-2022-0185) in the Linux kernel component
Zerodium increase the Microsoft Outlook zero-click vulnerability bounty from the original $250,000 to a maximum of $400,000.
Linux issued a risk notice of pkexec, the vulnerability number is CVE-2021-4034, the vulnerability level is high risk with the CVSS of 7.8
Apache released a security bulletin that disclosed the SQL injection in JDBC Appender vulnerability (CVE-2022-23305)

Apache released a security bulletin that disclosed the deserialization of untrusted data in JMSSink vulnerability (CVE-2022-23302)

Apache released a security bulletin that disclosed Log4j deserialization vulnerabilities (CVE-2022-23307), which affected the Apache Log4j 1.x version
Zoho officially released a security notice for ManageEngine Desktop Central, the vulnerability number is CVE-2021-44757
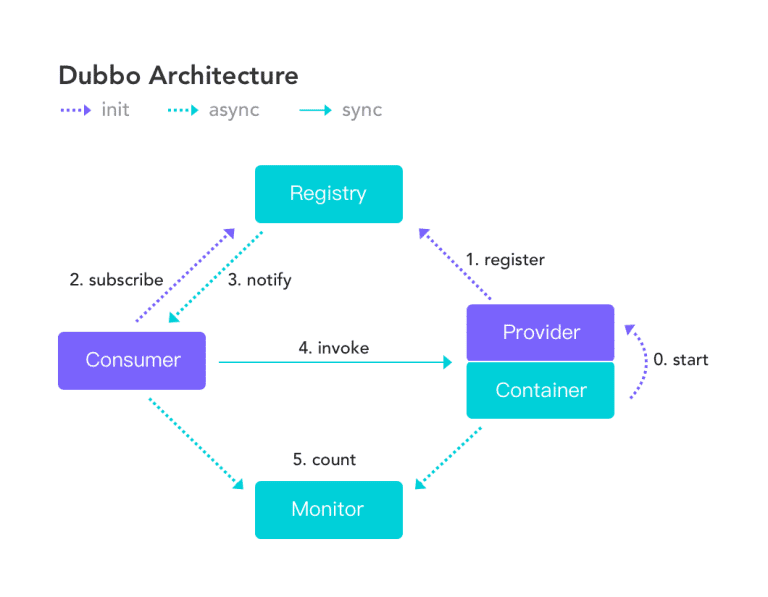
On January 10, Apache issued a security notice to fix a remote code execution vulnerability (CVE-2021-43297) in Dubbo.
CVE-2022-21907 affects all versions of Windows 10 Version 1809 and above, including Windows Server 2019/2022, is very easy to be exploited.