
 Do Son
CVE-2022-26138 affects Confluence Server and Data Center products, and, allows a remote, unauthenticated attacker log into Confluence.
Vulnerability
According to CVE-2022-35741, Apache CloudStack versions 4.5.0 and later are vulnerable to this vulnerability.
Spark released the latest security bulletin, which contains a shell command injection vulnerability (CVE-2022-33891). The severity is important
Tracked as CVE-2022-31107, the flaw is an OAuth account takeover vulnerability with a CVSS severity score of 7.1.
a remote code execution vulnerability (CVE-2022-32224) was disclosed that impacts specific versions of the Ruby on Rails platform.
Tracked as CVE-2022-22047, this bug is an elevation of privilege bug in Windows’ Client/Server Runtime Subsystem (CSRSS)
Amazon issued a security advisory Monday to address a vulnerability (CVE-2022-2385) that could enable an attacker to privilege escalation

Node.js released an advisory to fix seven vulnerabilities including 3 separate HTTP Request Smuggling, one code execution (CVE-2022-32212)

CVE-2022-34265 PoC exploits code is about to be published for a vulnerability that allows an attacker to attack Django web applications.
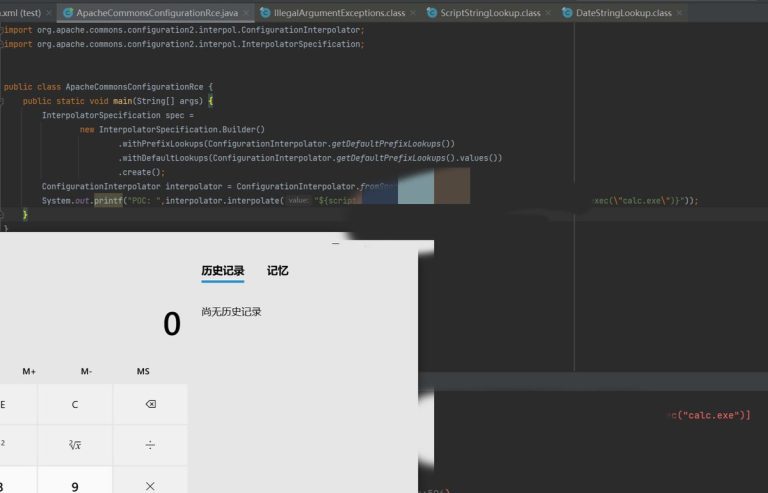
On July 5, 2022, Apache officially issued a risk notice for Apache Commons Configuration remote code execution (CVE-2022-33980) vulnerability.

OpenSSL library has been discovered as susceptible to a remote memory-corruption vulnerability on select systems. Tracked as CVE-2022-2274

CVE-2022-34918 is a heap buffer overflow due to a weak check and has been introduced within the netfilter which can be exploited
Google released a security bulletin to reveal the CVE-2022-2294, which is a major security threat to heap buffer overflow in WebRTC
Researchers released CVE-2022-26763 PoC exploit code for a critical execute arbitrary code vulnerability affecting multiple Apple products
GitLab issued a security notice to fix a vulnerability (CVE-2022-2185) in Community Edition and Enterprise Edition, with a CVSS score of 9.9
Apache Shiro issued a risk notice about the authentication bypass. The vulnerability number is CVE-2022-32532

PT SWARM shared the CVE 2022-31626 PoC with the detailed technique, which can be triggered via a rogue MySQL/MariaDB server
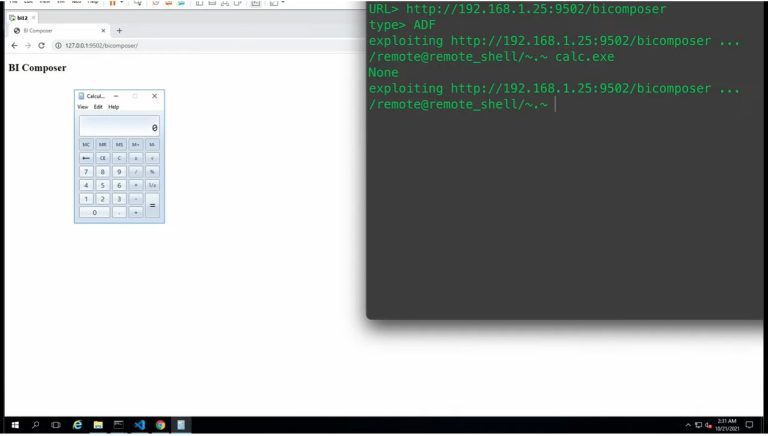
CVE-2022-21445 PoC exploit code is about to be published for a vulnerability that allows an attacker to gain RCE on the server-side
Tomcat released the latest security bulletin on June 23, which contains a cross-site scripting vulnerability (CVE-2022-34305).
VMware issued a security bulletin to disclose a SpEL Expression injection vulnerability (CVE-2022-22980) in Spring Data MongoDB

The flaw tracked as CVE-2022-2068, was reported to the OpenSSL Project by Chancen of Qingteng 73lab. It affects OpenSSL versions 1.0.2, 1.1.1, and 3.0
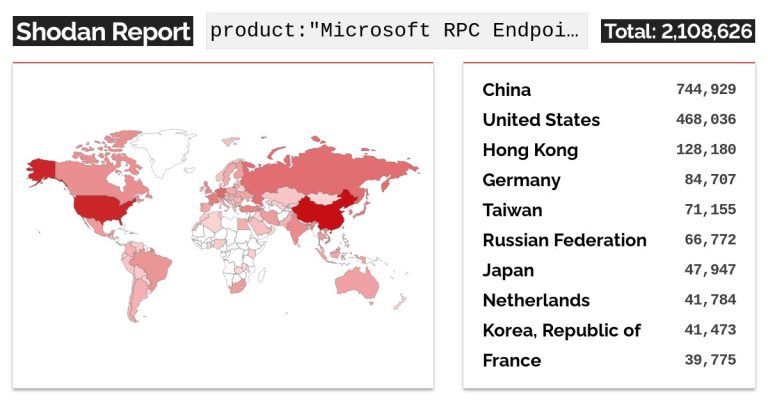
CVE-2022-26809 PoC exploit code is about to be published for a vulnerability that allows an attacker to gain remote code execution